

OneTrust Cookie Consent in 2026: 7 Live Implementation Checks After Google’s June Update
If you ran a OneTrust cookie consent audit on June 16, 2026, you probably found something broken. Google shifted the ground under every CMP that day: ad_storage became the sole control for advertising data flowing into Google Ads. CMPs did not need code changes, but their consent defaults and purpose mappings suddenly mattered in a way they did not the week before.
This guide walks through seven live checks to run on a OneTrust cookie consent deployment in 2026. The goal is not to convince you to buy OneTrust, but to give you a defensible verification routine that holds up to a Data Protection Authority inquiry, a Google Ads rep review, or your own quarterly privacy review.
What OneTrust Cookie Consent Actually Does in 2026
OneTrust’s Cookie Consent product sits in the Consent Management Platform (CMP) category. It scans your domains, classifies cookies and tracking technologies, presents a consent banner and preference center, records consent receipts, and feeds consent signals to downstream marketing and analytics tools.
In its 2026 documentation, OneTrust describes the platform as covering cookie detection, banner customization, geolocation-based consent models, automated blocking, consent receipt logging, and cross-domain consent synchronization. Those are the baseline capabilities. The 2026 product updates added bulk exports of CMP receipts, granular permissions for managing tracking technologies, and tighter alignment with Google Consent Mode v2.
OneTrust is also a Google-certified CMP. That certification is what allows the platform to send the ad_storage, analytics_storage, ad_user_data, and ad_personalization signals that Google reads in Consent Mode v2. If those signals are misconfigured, your Google Ads measurement breaks quietly and your privacy posture is exposed.
Why the June 2026 Google Update Matters
Before June 15, 2026, advertising data in Google’s ecosystem was governed by a mix of Consent Mode signals and platform-level controls. After that date, ad_storage became the single switch for whether advertising data flows into Google Ads. According to OneTrust’s own analysis, the change did not require product updates for CMPs that were already properly configured, but it did require verification.
The practical effect: any OneTrust deployment where the default consent state was set to “accept all,” or where ad_user_data and ad_personalization were not mapped to a user-controllable purpose, now has a measurable compliance gap. Google Ads may continue to report conversions, but those conversions are based on data collected without valid consent under GDPR.
This is not a hypothetical risk. The European Data Protection Board (EDPB) has been clear that Consent Mode v2 parameters must reflect actual user choices, not platform defaults. The EDPB’s 2024-2027 strategy emphasizes strengthening enforcement, and their 2025 Annual Report (published in April 2026) highlights ongoing work on “Consent or Pay” models and dark pattern prevention.
7 Live Checks for OneTrust Cookie Consent in 2026
These are the checks to run on a live deployment. They assume you have access to the OneTrust admin console, your website’s source code, and browser developer tools.
1. Verify the Default Consent State
Open your site in a private browsing window with no prior consent history. What appears? A banner with clear “Accept” and “Reject” options of equal prominence, or a banner with “Accept All” in bold and a small “Manage Preferences” link?
The EDPB has repeatedly stated that rejecting cookies must be as easy as accepting them. The French CNIL fined several major sites in 2023 and 2024 for exactly this design failure. In OneTrust, navigate to the banner template and confirm that the “Reject” button has the same size, color contrast, and position as the “Accept” button.
If your default state is “accept all” and the user must click to reject, you have a finding to log before anything else.
2. Map Every Cookie Category to a Consent Purpose
In the OneTrust Cookie Compliance console, open the “Cookies” tab and export the full cookie list. Cross-reference each cookie against its assigned purpose: Strictly Necessary, Performance, Functional, Targeting/Advertising, or Social Media.
Cookies that fire before consent (analytics tags, advertising pixels, social media trackers) must be blocked at the tag management layer until the user has explicitly opted in. OneTrust’s auto-blocking should handle this if the script is loaded synchronously in the . If your developers deferred the OneTrust script or moved it to a tag manager that does not respect consent signals, cookies will leak.
Run a browser test with the Network tab open. Filter by “cookie” and reload the page without consenting. You should see no cookies set beyond the strictly necessary ones (session ID, CSRF token, cart contents).
3. Confirm Google Consent Mode v2 Signals Are Sent
Open Chrome DevTools, go to the Console, and after consenting (or rejecting), check the dataLayer or the gtag consent command. The four Consent Mode v2 signals should be present:
ad_storage: “granted” or “denied” based on user choiceanalytics_storage: “granted” or “denied” based on user choicead_user_data: “granted” or “denied” based on user choicead_personalization: “granted” or “denied” based on user choice
If any of these signals are missing or set to a default value that does not reflect the user’s actual choice, your Consent Mode v2 implementation is incomplete. Google Ads will still fire, but the data it collects will not be usable for behavioral advertising in the EEA and UK without a valid consent signal.
4. Test Geolocation-Based Consent Models
OneTrust supports different consent models based on the visitor’s location. A user in California should see a CCPA-compliant “Do Not Sell or Share” opt-out, while a user in Germany should see a GDPR-compliant opt-in banner with granular categories.
Use a VPN or a geolocation testing tool to simulate visits from different regions. Confirm that:
- EU/UK visitors see an opt-in banner with no pre-checked boxes.
- California visitors see a clear “Do Not Sell or Share My Personal Information” link.
- Virginia, Colorado, Connecticut, and other state-law visitors see the appropriate opt-out mechanism.
If your deployment shows the same banner to every visitor regardless of location, you are either over-complying (showing opt-in to California visitors when opt-out would suffice) or under-complying (showing opt-out to EU visitors when opt-in is required).
5. Audit the Consent Receipt Log
OneTrust stores consent receipts that document when a user gave or withdrew consent, what they consented to, and the version of the cookie policy they acknowledged. This log is your first line of defense in a regulatory inquiry.
Export a sample of receipts and check for:
- Timestamp accuracy (is the timestamp in UTC? Is it consistent across the UI and the API?)
- Purpose-level granularity (does the receipt record consent per category, or only a binary “accepted all / rejected all”?)
- Withdrawal events (when a user withdraws consent, is that event logged with the same detail as the original consent event?)
A consent receipt that only records “user clicked Accept on 2026-06-15” without capturing the specific purposes consented to is not adequate documentation under GDPR Article 7(1).
6. Verify the Preference Center Is Accessible After Initial Consent
Users must be able to withdraw consent as easily as they gave it. The most common implementation pattern is a persistent “Cookie Preferences” link in the website footer.
Click that link. Does it open a preference center where you can change your choices? Can you save those changes? Does the change take effect immediately, or do you need to clear your browser cache and revisit the site?
If the preference center is buried three clicks deep, or if changes do not propagate to active sessions, your deployment does not meet the “as easy to withdraw as to give” standard.
7. Check the Scanner for Accuracy
OneTrust’s cookie scanner crawls your site to identify cookies, tags, and trackers. It is not perfect. New tracking technologies are introduced frequently, and third-party scripts can load additional cookies dynamically.
Compare the scanner output against a manual audit. Open your site, browse through key pages, and check the Application tab in Chrome DevTools for all cookies set. Are there cookies in the browser that do not appear in OneTrust’s cookie list? Are there cookies in OneTrust’s list that no longer appear on the site?
An out-of-date cookie list is a compliance gap. If a user consents to “Performance” cookies and your site also sets an unlisted advertising cookie, the user has not actually consented to that tracking.
The OneTrust Pricing Reality in 2026
Pricing is not a technical check, but it is a practical one. OneTrust retired its self-serve “Pro” tier in 2026, and the new minimum annual commitment is approximately $10,000. Historical data suggests implementation costs can add another 20-40% on top of the subscription fee, and some customers have reported renewal increases of up to 500% due to the shift from per-domain pricing to average daily visitor metering.
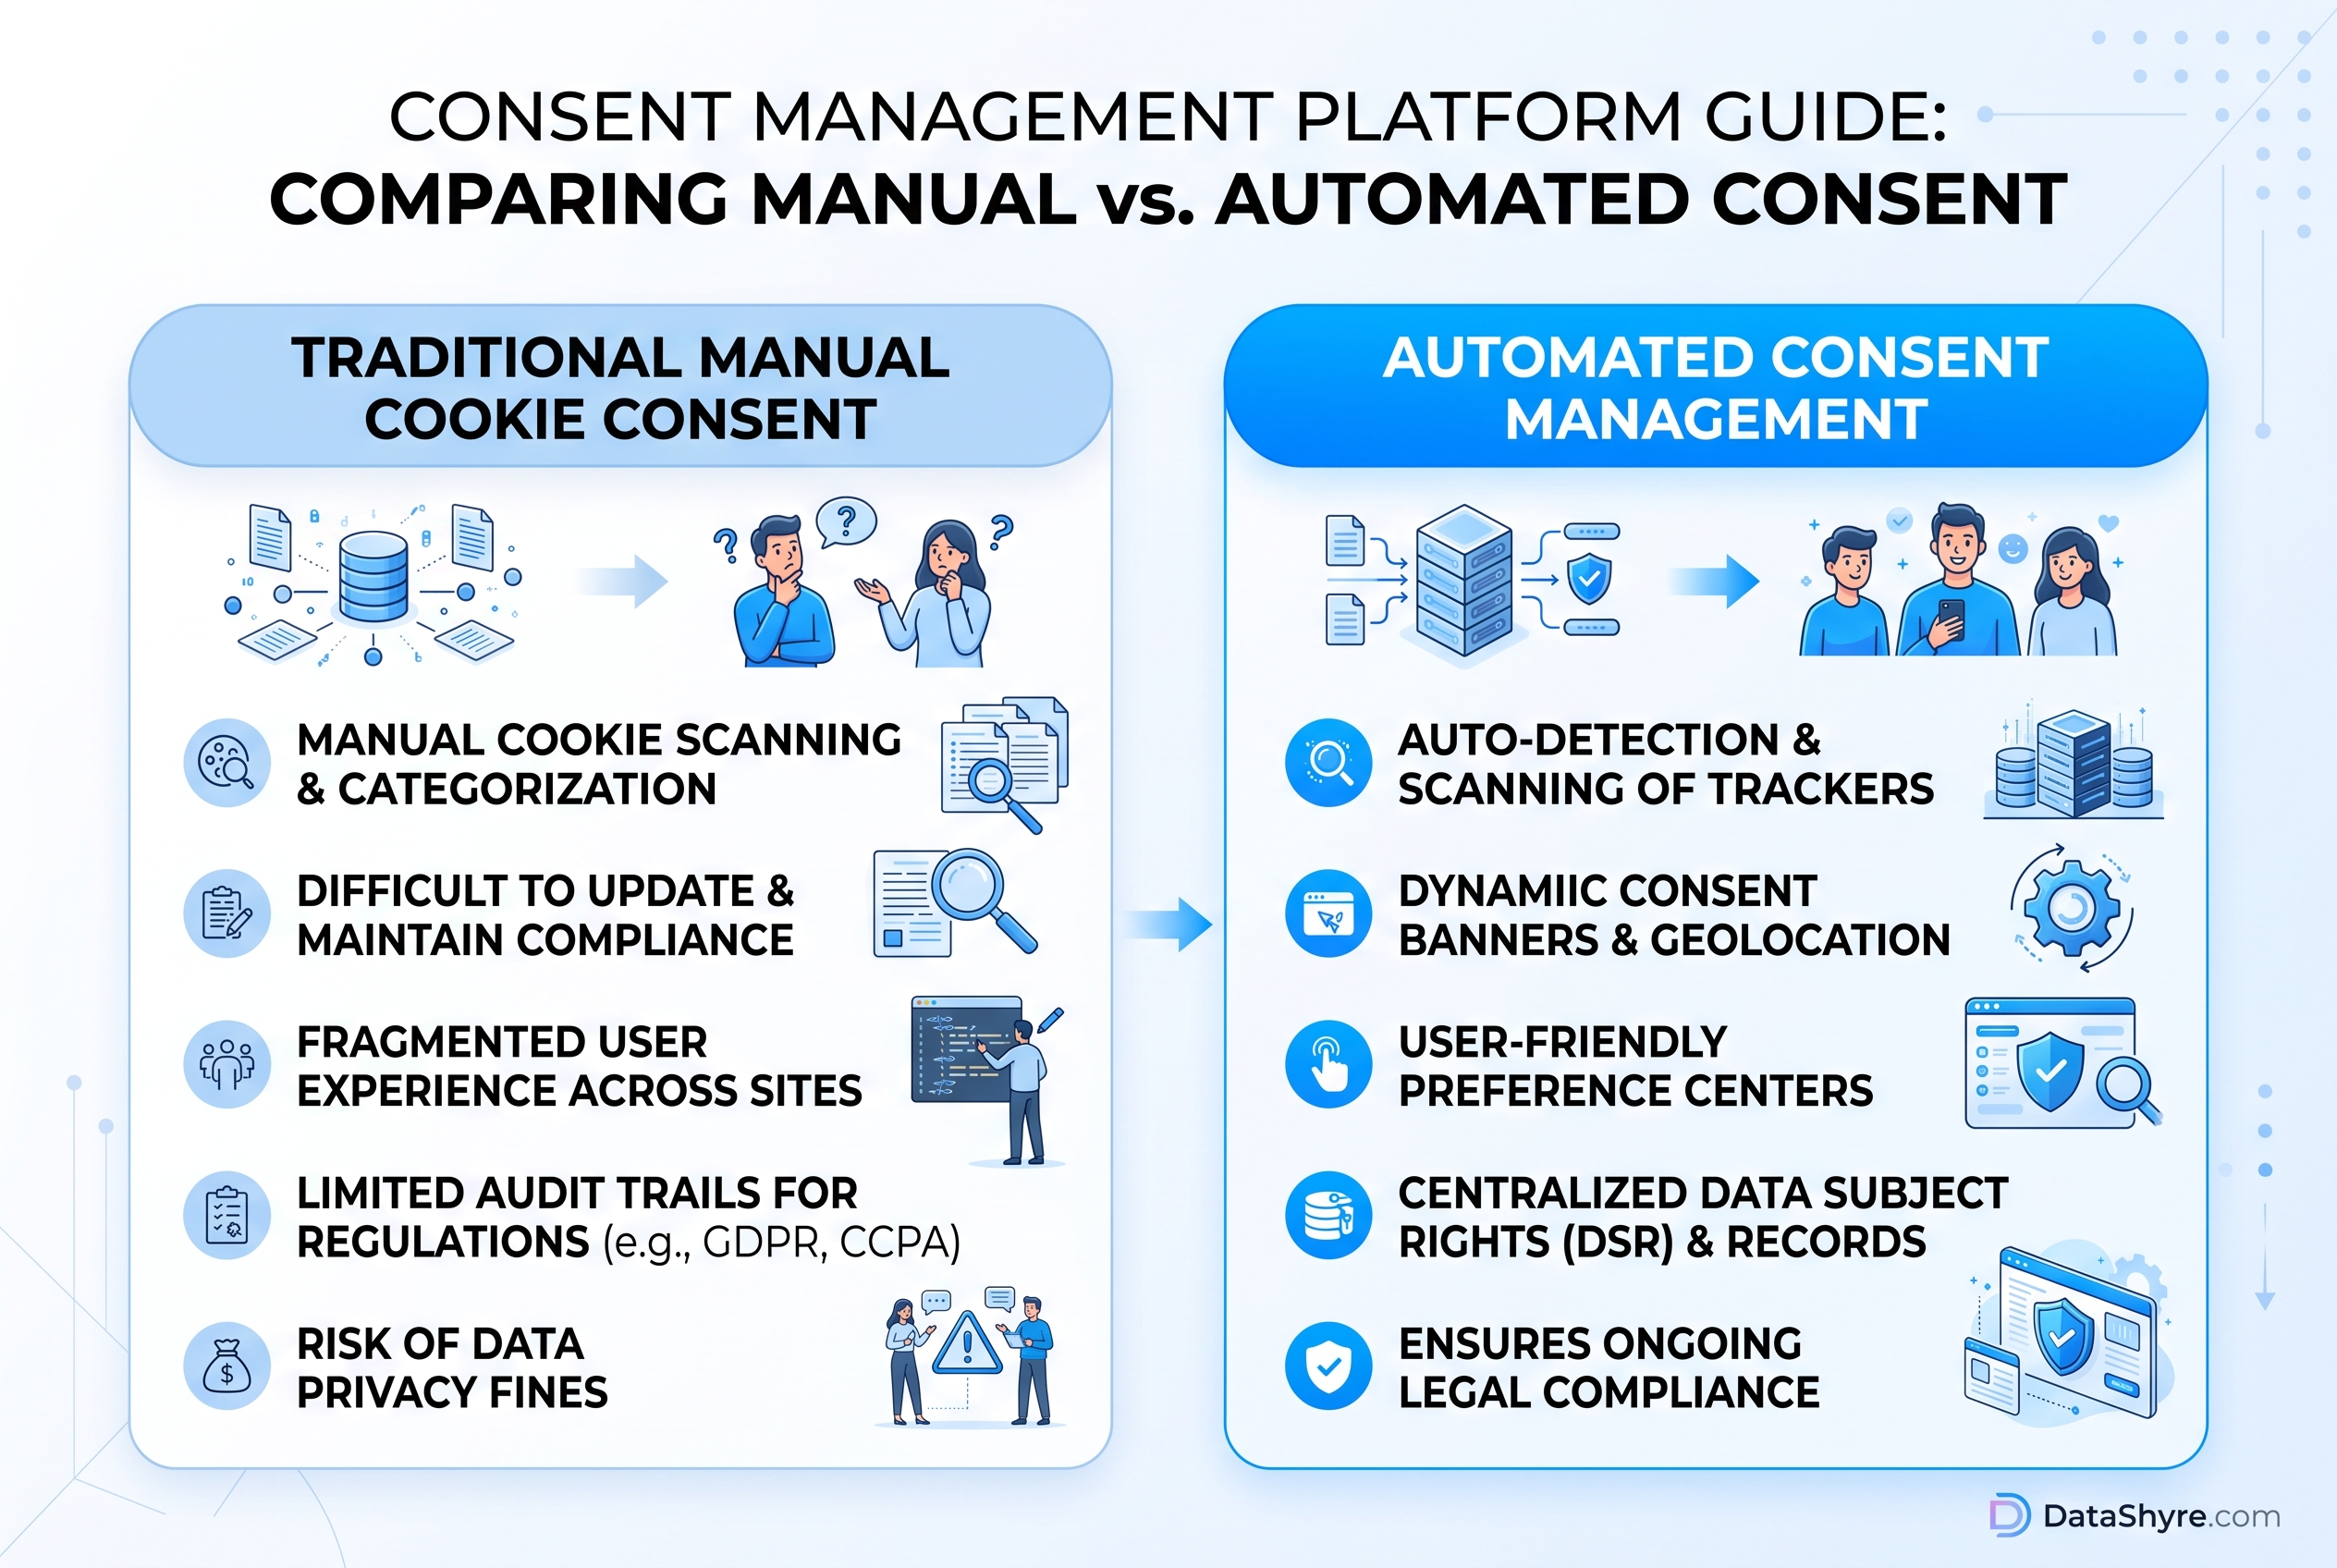
This matters because compliance teams often default to OneTrust without evaluating alternatives. For organizations with straightforward needs (a single domain, basic geolocation rules, standard Google Consent Mode v2 integration), open-source CMPs or lower-cost alternatives may deliver equivalent compliance outcomes at a fraction of the cost.
The point is not to avoid OneTrust. The point is to verify that the value you are paying for matches the value you are receiving. The seven checks above are your verification tool.
When OneTrust Is the Right Choice
OneTrust makes sense when:
- You operate across multiple domains and need cross-domain consent synchronization.
- You have complex data flows involving multiple marketing technologies, vendors, and jurisdictions.
- You need to demonstrate compliance to a regulator and want a platform with established audit trails and documentation.
- You have the budget for the $10,000+ annual commitment and the implementation overhead.
For smaller organizations or those with simpler needs, evaluating alternatives like Cookiebot, Usercentrics, or open-source CMPs is worth the time.
What to Do After You Run the Checks
If you find issues (and most deployments will have at least one), prioritize them:
- Critical: Default consent state favoring “Accept All,” missing Consent Mode v2 signals, or cookies firing before consent.
- High: Inaccurate cookie scanner results, missing geolocation-based consent models, or inadequate consent receipt logging.
- Medium: Preference center accessibility issues, minor UX problems with banner prominence, or outdated cookie policy links.
Document each finding with a screenshot, a timestamp, and a remediation plan. If you are under a regulatory inquiry or anticipate one, this documentation is invaluable.
Conclusion
OneTrust cookie consent in 2026 is a capable platform, but “capable” is not the same as “correctly configured.” Google’s June 2026 update made Consent Mode v2 signals the sole control for advertising data, and the EDPB’s continued focus on dark patterns and equal-prominence requirements means that even a well-intentioned deployment can fail if it is not actively verified.
The seven checks in this guide are not exhaustive. They are the baseline. If your OneTrust deployment passes all seven, you have a defensible position. If it fails any, you have a clear to-do list with measurable outcomes.
Compliance is not a one-time project. It is a continuous verification process, and the tools are only as good as the checks you run against them.
—
Published: September 2, 2026
Related Articles:
- Cookie Consent Google Tag Manager in 2026: 7 Live Checks – Integration patterns and runtime verification
- Consent Management Platform Best Practices in 2026 – Platform selection and deployment guidance
- Google Consent Mode in 2026: 7 Live Checks – Consent Mode v2 implementation and verification