Best GDPR Software in 2026: 7 Buyer Checks Before You Choose
DataShyre StaffJun 22, 2026
55 min read
Best GDPR Software in 2026: 7 Buyer Checks Before You Choose
If you are searching for the best GDPR software on August 3, 2026, the first useful move is to stop treating it as one product category.
Some teams need a consent management platform that can collect a fair choice and keep non-essential tracking from firing too early. Some need policy and notice tooling that stays current as services and legal text change. Others already have the visible banner, but need consent and preference signals enforced across websites, apps, and downstream systems.
That is the practical frame for this keyword in 2026. The best GDPR software is not the product with the loudest feature grid. It is the one that closes your riskiest compliance gap with the least operational drift.
If you want the adjacent implementation context first, start with our guides to consent management platform, cookie consent banner, and Google Tag Manager cookie consent. This article is narrower. It is the buyer framework I would use before spending money on GDPR tooling this week.
Why the keyword still matters in 2026
The official baseline still points in the same direction.
On April 29, 2026, the UK ICO published final storage-and-access guidance covering cookies, tracking pixels, device fingerprinting, and similar technologies. The European Commission still says valid consent must be freely given, specific, informed, and clear, and that withdrawal should be as easy as giving consent. On July 14, 2026, the European Data Protection Board required the Belgian DPA to handle the merits of a cookie-banner complaint involving broadcaster VRT instead of treating the case as a procedural dead end. France’s CNIL has been equally direct on banner design, saying that rejecting cookies should be just as easy as accepting them.
That means software cannot be judged only by the first layer a visitor sees. The real test is whether the tool can turn user choice into live technical behavior, keep records another team can understand later, and handle region-specific logic without becoming brittle.
The market pressure is real too. Google’s current publisher requirements still say publishers serving personalized ads in the EEA, the UK, or Switzerland need a Google-certified CMP integrated with the IAB Transparency and Consent Framework. In California, the Department of Justice still says a valid Global Privacy Control signal must be honored as a request to stop sale or sharing, while the CPPA’s regulations page shows both the CCPA and CCPA Regulations as effective on January 1, 2026.
For buyers, that makes the search for the best GDPR software less about picking a fashionable brand and more about buying the right control layer.
Why automation is now table stakes for GDPR compliance
Automation has become central to GDPR compliance—not just because it’s convenient, but because trying to manage everything manually is a recipe for falling behind.
In 2026, the privacy landscape isn’t just GDPR and cookies anymore. The EU AI Act’s new “high-risk” requirements kicked in on August 2, and NIS2 amped up security and documentation expectations across Europe. These run side-by-side with GDPR and push compliance teams to treat privacy as part of a broader, continuous risk posture—not something you dust off once a year for an audit.
The telling stat? Cisco’s 2026 Data Privacy Benchmark Study reports that 90% of organizations now say their privacy programs have expanded due to AI alone.
What does this look like in practice?
Always-on compliance, not point-in-time: Regulators (and their software) now expect controls to be effective every day, not just at the time of annual reviews. Audit trails, evidence, and control checks all need to keep pace.
Overlapping laws, shared controls: It’s rare to only care about GDPR anymore; teams that also touch SOC 2, ISO 27001, HIPAA, or other frameworks need a way to map controls once and reuse evidence instead of duplicating work.
Automation as the ground floor: Buyers are demanding tools that automate evidence collection, regulatory updates, and workflow tracking—because most privacy teams can’t scale headcount just to handle new paperwork.
Live inventory and workflows: Managing your Record of Processing Activities (ROPA), running impact assessments (like DPIA, LIA, TRA), or exporting compliance records means pulling from up-to-date, actionable data—not static spreadsheets living in a forgotten folder.
In short: as regulatory complexity grows, software has to do the heavy lifting. Your real compliance posture depends on how well your tools connect obligations to actual controls—continuously and with as little manual intervention as possible.
How GDPR Software Tackles Data Mapping, ROPA, and Data Discovery
If you’re vetting “best GDPR software,” one of the first places the rubber meets the road is how it helps you map data flows and keep your Records of Processing Activities (ROPA) in order. Manual spreadsheets just don’t cut it anymore—not with data sprawling across SaaS platforms, internal tools, and third-party vendors.
A solid GDPR compliance tool should:
Automate Data Mapping: It should surface where personal data moves in and out of your business—whether that’s between your main app, marketing stack, cloud storage, or an integration you forgot existed. The best tools tap into your systems (via APIs or scanning) to uncover data trails you didn’t even remember setting up.
Simplify ROPA Creation: With Article 30 of the GDPR at the center, most platforms now offer built-in templates, workflows, and policy-building wizards so you’re not starting from scratch. These guides help you capture processing purposes, legal bases, recipient lists, and retention periods per system or activity—all without trawling through technical documentation every quarter.
Handle Controller vs. Processor Duties: No tool can rewrite your DPA, but the better ones distinguish between the records you need to keep as a data controller versus those you owe as a processor. Some can even flag missing details or highlight when your records go stale.
Empower Cross-Functional Teams: Effective platforms don’t silo compliance in legal or security. They offer permissioned access to product, marketing, and engineering teams—so each group can tag and update data flows they actually own.
For anyone who’s ever spent a Sunday night hunting for a four-year-old spreadsheet when the audit clock is ticking, this is where software proves its weight in fines avoided.
The net result? Instead of racing to update static documentation every time your tech stack shifts, you have a living map and compliance backbone—one that’s credible when regulators, partners, or your own board come calling.
Watch for continuous compliance—not just day-one launch
The reality is that GDPR compliance is never truly “done.” Supervisory authorities across the EU and UK now expect organizations to maintain provable, ongoing control, not just a well-documented initial setup. And with record fines from regulators like CNIL and the ICO topping billions of euros, this isn’t just a checkbox for a launch week anymore.
Continuous compliance monitoring is simply the evolving practice of baking privacy discipline into everyday operations. Instead of treating your records and controls as a set-and-forget exercise, you’re actively watching for drift, validating that controls are still working, and detecting issues before they become reportable incidents.
This kind of monitoring isn’t just about ticking off audit boxes—it’s about catching when a tag slips past runtime enforcement, or when an integration suddenly ignores consent choices after an update. When a consent preference quietly stops propagating to your adtech or analytics stack, the market now expects you to spot and fix it proactively, not just explain it after an investigation.
In short, the shift is toward solutions and habits that:
Continuously map your regulatory obligations to actual, running controls.
Trigger alerts when behaviors fall out of line.
Provide evidence—not just logs—showing when and how issues were caught and addressed.
That ongoing vigilance is no longer optional; it’s woven into the definition of defensible GDPR compliance.
7. Insist on continuous monitoring to catch what slips through
Even the best setup can drift out of compliance over time.
Continuous monitoring features are your early warning system—they flag when tags fire unexpectedly, new scripts sneak in, or privacy controls quietly loosen. Live monitoring means privacy teams aren’t just reviewing stale audit logs after the fact; they can see misfires and suspicious changes as they happen.
Look for platforms that let you:
Connect directly to your real environments (not just staged demos);
Surface control failures and privacy risks in real time;
Track if consent signals remain intact across the stack, even after site changes or vendor updates;
Maintain up-to-date, defensible records that auditors can trust.
With active monitoring in place, you’re not just relying on hope and quarterly checkups—you’ll spot issues fast, keep evidence fresh, and explain changes whenever someone (regulator, customer, or exec) asks.
Automating data subject rights: How software closes the compliance gap
Responding to data subject requests—access, deletion, portability—can quickly overwhelm teams, especially once the regulatory clock starts ticking. The best GDPR software now bakes automation right into these processes, reducing the margin for manual error and helping teams hit those critical deadlines.
What does this actually look like?
Request intake and tracking
Many platforms provide secure web forms or user portals where individuals can submit requests. Submissions are automatically logged, timestamped, and routed to the right person or team—no lost emails, no sticky notes.
Deadline management and alerts
Good tools automatically track regulatory timeframes (often 30 days for GDPR), prioritizing requests and sending proactive reminders as deadlines approach. That means less firefighting to avoid missed responses.
Automated workflows for fulfillment
Some solutions integrate with data stores, so deletion and data export tasks can be triggered directly—no tedious copying or searching through scattered systems. The software can fetch, consolidate, and securely deliver data packages (for access or portability requests) or orchestrate deletions across cloud platforms, databases, and SaaS tools.
End-to-end audit trails
Each step—submission, internal review, completion—is logged automatically. If you face a regulatory inquiry, you’ll have dated records showing your response at every stage.
In short, well-implemented GDPR tools let you spend less time chasing down requests and more time building trust—while knowing, if anyone asks, you have the receipts.
8. Understand the real cost, not just the sticker price
The price on the product page is only the start.
Licensing fees are the obvious line item, but the real cost of running GDPR tools over time is shaped by everything else:
setup and initial implementation (who has to do the work, and how long it takes);
ongoing configuration as your organization changes—adding new teams, regions, or compliance requirements;
the level of internal support or external consultants you’ll need to keep things running smoothly;
whether the software can scale with growing data or more complex governance needs, without forcing you to rebuild later.
Legacy vendors like OneTrust and TrustArc are notorious for appearing cost-effective upfront, then ballooning in complexity and maintenance as operations expand. Beware “simple” pricing models that gloss over integration or customization. The best GDPR software is candid about exactly what’s included and what grows in cost as you do.
Automated evidence collection makes audits winnable
Manual evidence collection for GDPR is a painkiller project—messy, slow, and usually incomplete. Automated evidence collection pulls from across your stack, reducing hours lost to chasing screenshots, dated spreadsheets, or “who audited what and when?” Slack threads.
Here’s why that matters:
It drastically cuts manual overhead, so your team spends more time fixing real problems instead of bookkeeping.
It reduces human error—less missed evidence or mismatched records when regulators want specifics tied back to GDPR articles or policy commitments.
Integrations with tag managers, analytics, consent banners, and cloud providers help evidence flow in from the systems that actually process and enforce privacy controls.
It means you’re ready to demonstrate compliance with what was shown, chosen, or changed—not “almost” or “should have,” but the audit-ready, timestamped reality.
All told, automated evidence makes the “paper trail” less mythical and more useful, ringing true for Google Analytics events, Salesforce data change logs, or anything else that could make or break your defense if the auditors come knocking.
Support for DPIA and Privacy Impact Assessments
When it comes to safeguarding against high-risk processing, GDPR doesn’t leave much wiggle room—Data Protection Impact Assessments (DPIAs) are mandatory. For businesses, the challenge is less about knowing that they need DPIAs, and more about handling them efficiently and consistently, without losing weeks to manual reviews or reinventing the wheel every time a new system comes online.
So, what should “best GDPR software” actually help you do here?
Built-in DPIA templates and guided workflows: The best platforms will streamline impact assessments by providing up-to-date, regulator-ready templates and step-by-step workflows. This takes the guesswork out and reduces room for inconsistency.
Automated DPIA triggers: Look for tools that flag when an assessment is required based on your data sets, processing activities, or changes in your tech stack—saving you from compliance blind spots.
Progress tracking and reminders: Automated tracking of assessment status, reviewer assignments, and periodic review reminders help close the loop and ensure nothing slips through the cracks.
Documentation and update management: A good solution will keep a searchable history of completed DPIAs and prompt you when legal or business changes require updates, building a living record for regulators and internal audits alike.
Ultimately, the right software here shrinks the overhead of privacy impact assessments, standardizes the process across teams, and makes sure nothing gets missed—especially when risk rises fast or your operations get more complex.
Cloud and SaaS integrations: critical for real-world compliance
GDPR compliance is rarely limited to a single website or internal database. In reality, personal data often flows across a patchwork of cloud providers and SaaS tools—from Google Cloud and AWS to Salesforce, Slack, and hundreds of specialized platforms.
Why does this matter? If your software can’t see or control where personal data travels among these systems, there’s a real risk of falling out of compliance. Regulators expect organizations to know, track, and manage every point where data is processed—not just at the banner or on your marketing site, but all the way through the SaaS apps and cloud environments where that consent is supposed to follow.
A robust GDPR platform should offer:
Direct integrations with the major cloud infrastructure providers (think AWS, Azure, Google Cloud)
Native connections to popular SaaS applications like HubSpot, Zendesk, or Office 365
The ability to automatically discover and map personal data flows across all these systems
Tools to audit, control, and report on processing activity—so that “honoring consent” doesn’t stop at your homepage
In practice, this means buyers should ask where a tool’s integration coverage begins and ends. Does the platform only play nicely on the website, or can it enforce preferences inside your cloud stack and business-critical SaaS systems, too? In a world where one team’s workflow can spin up a new app overnight, staying ahead depends on these integrations being deep, broad, and easy to keep current.
What Are the Top Compliance Privacy Software Options?
If you’re filtering the field down to the key players in compliance privacy software, you’ll quickly see a handful of established names surface again and again. Each of these vendors approaches the privacy problem with a slightly different mix of specialization and flexibility. The best fit for your team depends less on which brand has the shiniest interface, and more on which one shortens your compliance checklist without straining your existing processes.
Here’s where the most recognized platforms tend to show up:
Comprehensive compliance suites: These cover everything from GDPR to CCPA and frameworks beyond, aiming to be the “single pane of glass” for privacy programs. They often include policy management, workflow automation, data mapping, and strong audit trails.
Consent and preference management specialists: These focus on user-facing consent banners, preference centers, and signal enforcement—providing deep integration with web, app, and backend systems to capture and honor choices.
Data rights request handlers: Some solutions major on automating and tracking data subject requests, making it easier to give users access to, rectification of, or deletion of their data on deadline and with an audit trail.
Vendor and third-party risk platforms: These foreground third-party due diligence and vendor assessment, often tying privacy and security obligations together in one system.
When you compare leading platforms side by side, ask where each shines (and where it stretches). Does one reliably update its legal templates as laws change? Is another better at plugging into your tag manager or analytics flow with minimal fuss? Does support for international jurisdictions or rapidly evolving frameworks affect the timeline for rollout?
In the end, the best compliance privacy software is the one that matches your organization’s complexity today and can scale with what comes next.
How long does it typically take to achieve GDPR compliance using software solutions?
This is the question everyone wants answered, but—as is often the case—the honest answer is, “it depends.” The speed at which you can land on full GDPR compliance using software hinges on a handful of practical realities:
Your existing complexity. Are you shepherding one flagship website, or juggling 12 markets, a mobile app, and a warehouse of legacy data?
Your current privacy posture. If your team already has good data mapping and access controls in place, you’re halfway there. If your data inventory is woven together with duct tape and wishes, expect more time.
How much you automate. Modern privacy platforms can help you leapfrog the process by handling everything from evidence collection to real-time auditing. Automation trims away the slowest steps—painfully manual reviews and after-the-fact proof gathering.
For a very lean team with working templates and a single site, plugging in a robust consent and compliance tool can take days to a few weeks, especially if you’re aiming for baseline requirements. For enterprises with sprawling footprints, expect the journey to stretch into months—sometimes longer, if you’re coordinating across legal, IT, product, and marketing.
Practical tip: The fastest path isn’t about cutting corners, but about minimizing “compliance drift.” The right software keeps you alert to changes long after launch, automating checks and mapping data as your stack evolves.
So, while there’s no magic “one-week solution,” the right tools do turn the marathon into a brisk jog—especially compared to the manual processes of the past.
Pros and cons of automation-first privacy tools
When looking at privacy management tools built around automation and integration, the strengths and tradeoffs often fall into clear patterns.
Where they shine
Automating complex workflows: These platforms excel at streamlining data subject request handling (DSARs), helping teams intake, triage, and fulfill requests efficiently—even across tangled webs of internal and external systems.
Integration horsepower: Their pre-built connections to major SaaS apps and cloud platforms make it possible to find, manage, and erase personal data in a way that manually operated tools simply can’t match.
Real-time data visibility: Powerful automation platforms frequently offer live data mapping, which supports up-to-date records of processing activities and smoother Records of Processing Activities (ROPA) compliance.
Where caution is warranted
Integration dependency: Their value is closely linked to how well they connect to your existing tech stack. If your core tools aren’t covered, the automation advantage can quickly fade.
Narrow GRC focus: Many automation-heavy solutions prioritize privacy operations over broad governance, risk, and compliance (GRC), which might leave gaps for teams with complex or overlapping regulatory needs.
Maturity and scale: Fast-moving automation players can be less “battle-tested” than older, broader enterprise suites. That might mean fewer features out-of-the-box or a steeper learning curve when plugging into sprawling data ecosystems.
What do real users say about GDPR software?
Teams who have adopted GDPR compliance tools often report a subtle but significant shift: less scrambling, more confidence. Instead of playing whack-a-mole with each new regulation or customer request, they find themselves with clearer documentation and repeatable processes they didn’t have before.
A few themes show up again and again in user feedback:
Peace of mind for EU/UK engagement: Organizations mention feeling much more comfortable expanding into European markets, knowing their compliance posture is up to date.
Structured workflows: Users highlight that well-designed platforms help codify internal procedures, making policy updates less painful and easier to audit.
Audit-ready records: Teams appreciate software that keeps logs understandable—not just for legal review, but so any department can answer “what happened when?” without detective work.
Ongoing compliance health: Rather than a one-and-done setup, the most valued tools surface drift early (think OneTrust, TrustArc, or Usercentrics), giving teams a heads-up when a new vendor or marketing tweak might have unintended consequences.
Above all, the feedback is less about ticking boxes, and more about practical confidence—tools that do the invisible heavy lifting, so compliance doesn’t routinely fall through the cracks.
Data-centric privacy compliance platforms: strengths and gaps
The last “bucket” is the data intelligence layer—platforms that approach GDPR by mapping and classifying the personal data itself, often with the help of machine learning.
These tools shine when the core problem is not banner click rates or notice text, but sheer data sprawl: you might not even know where sensitive data lives or how to list it in your ROPA (Record of Processing Activities). Data-centric platforms—think of names like BigID—excel at crawling sprawling file shares, cloud storage, hybrid environments, and databases to build detailed inventories of both structured and unstructured data.
Strengths of this approach:
Deep discovery and classification: Automated scanning across on-prem, cloud, and big data lets you uncover personal data you didn’t even know you had (including in emails, chat files, or obscure databases).
Regulatory groundwork: If your GDPR headaches start with mapping and documenting data for audits, these tools can jumpstart DSAR (Data Subject Access Request) fulfillment, data minimization, and risk scoring.
Operational integrations: Data intelligence is rarely a standalone department. These platforms often play nicely with downstream privacy, security, and governance tools—helping operationalize your data insights in the wild.
But this approach isn’t a universal fix:
Implementation complexity: Connecting to dozens (or hundreds) of systems can get tricky—setup isn’t plug-and-play.
Narrower focus: Data-centric tools excel at discovery and analysis, but you’ll likely need to connect them with consent platforms, notice layers, or enforcement tools to paint the full compliance picture.
Enterprise-grade price: The robust feature set makes sense for giants in finance, healthcare, or other regulated sectors. For smaller organizations, the cost and scale may be overkill.
Bottom line: data-centric privacy platforms offer unmatched visibility into sprawling data landscapes and can automate the hard parts of privacy documentation and risk analysis. But for most organizations, they’re one layer in the GDPR stack—not a catch-all solution.
Who needs automated DSAR fulfillment and wide SaaS integrations?
Automated DSAR fulfillment and robust SaaS integrations become crucial the moment your organization juggles high customer volumes or complex tech stacks.
This is especially true for:
Fast-growing SaaS or marketplace companies scaling quickly across regions.
Consumer-facing businesses collecting personal data from large audiences, like e-commerce, mobile apps, and financial services.
Teams using a patchwork of cloud platforms—think Salesforce, Zendesk, HubSpot, or Workday—that must pull data from multiple sources to handle access or deletion requests under GDPR, CCPA, or similar laws.
Legal and compliance teams tasked with quickly finding, exporting, or erasing customer records everywhere they live—across dozens of apps, not just the main database.
In short: If your risk is multiplied by volume, velocity, or complexity, automated DSAR workflows and deep integration libraries save you from manual processes, missed deadlines, and compliance headaches.
Who needs comprehensive privacy management platforms?
Comprehensive privacy management platforms are best suited for organizations that juggle global data operations, multiple websites or apps, and constantly shifting regulatory demands. Think: enterprises with in-house privacy and legal teams who face audits, handle data across borders, and need more than just a banner on the homepage.
These platforms shine when you have:
Dozens (or hundreds) of data flows to track and document.
Strict internal policies, external audits, or both—like those faced by finance, health, and global media companies.
Ongoing obligations to demonstrate compliance to regulators like the CNIL, ICO, or EDPB.
Complex environments where privacy choices ripple across web, mobile, backend, and third-party integrations.
If you’re wrestling with multi-team workflows or global compliance questions, these platforms turn privacy headaches into something less existential.
Automated data intelligence for mapping and managing personal data
Automated data intelligence tools fill a gap that manual reviews and consent banners miss—especially in large, complex data environments. The primary pain point in these organizations is often not just policy or notice, but simply knowing what personal data exists across sprawling systems, databases, and storage layers.
Modern solutions like BigID bring value here by using AI and machine learning to:
Discover and continuously monitor both structured and unstructured data sources
Classify personal data by type, risk, and location
Build comprehensive catalogs that map where sensitive information lives across the organization
This matters directly for GDPR, CCPA, and similar regulations. Discovery and classification are the first steps toward maintaining an accurate ROPA (Record of Processing Activities), enabling data minimization, and fulfilling data subject access requests (DSARs) at scale.
For organizations juggling dozens of systems and vast troves of data, automated intelligence tools help turn regulatory requirements into sustainable, enforceable practices—making it possible to respond to audits or user requests quickly, and with confidence.
Pros and cons of privacy-first compliance software with managed services
So, what actually happens if you opt for a privacy-first compliance platform that bundles in managed services? Here’s what buyers usually weigh:
What works well:
Professional support on tap: Access to a team of privacy experts can be a lifeline if your company doesn’t have deep in-house compliance know-how. This means someone else sweats the shifting rules around consent banners and legal records, while your team focuses elsewhere.
Credibility and track record: Established providers often bring recognizable certifications (think ISO 27701 or TrustArc’s long privacy pedigree). That helps satisfy stakeholders who want proof you’re not winging it.
Native consent and preference tools: These platforms tend to bake in all the must-haves—a proper cookie banner, consent dashboards, preference centers—which keeps you aligned with GDPR and similar regimes without hunting for a separate toolkit.
Where you might hesitate:
Higher price tag: Managed services aren’t cheap. While the guidance is valuable, it’s usually reflected in the pricing, which might be a hurdle for lean budgets.
Narrower technical coverage: Many privacy-focused platforms zero in on consent, policy, and documentation—not the full sweep of technical security compliance (for example, automated evidence collection for frameworks like SOC 2 or ISO 27001).
Not always heavy on automation: Workflow tools are often included, but the depth of automation (like hands-off monitoring or deep integration across all systems) typically lags behind platforms that specialize in security compliance.
For teams whose main headaches are around consent, consent records, and up-to-date privacy docs—especially with little in-house expertise—a privacy-first platform with expert support is often the smoothest path. But if you’re looking for all-in-one automation or need to solve for broader security standards beyond privacy, it may not check every box.
Breach notification: workflows and compliance in practice
Managing data breaches is non-negotiable under the GDPR, which gives organizations just 72 hours to notify supervisory authorities. The best GDPR software tackles this with clear, structured workflows designed for speed and accountability—not just box-checking.
Here’s what you should expect from a solid breach notification module:
Automated detection and alerts: The solution actively monitors for potential breaches, triggering instant alerts when suspicious activity is detected.
Deadline tracking: Built-in timers and reminders ensure teams stay ahead of the 72-hour requirement, reducing the risk of missing critical windows.
Structured response checklists: Step-by-step guidance helps teams gather details, assess impact, and determine who needs to be notified (both regulators and, in certain cases, affected individuals).
Documentation and audit trails: Every action—assessment, communication, decision—is logged and time-stamped, creating evidence for both internal reviews and regulator audits later.
Templates and compliance guidance: Pre-built notification templates and references to legal requirements help ensure responses are both thorough and on-point, minimizing the risk of non-compliance due to errors or omissions.
This workflow is common among major providers—OneTrust, TrustArc, and Securiti.ai all highlight structured breach response processes as a core feature. With data breaches making headlines and penalties rising, efficient breach notification is no longer a “nice to have”—it’s a must-have component in any GDPR solution.
Expanding regulatory pressure: AI, security, and documentation
GDPR does not sit alone in its influence over your compliance stack—particularly in 2026. For most organizations, the map of obligations is growing, not shrinking.
New laws like the EU AI Act, effective August 2, 2026, layer their requirements directly on top of GDPR where artificial intelligence systems touch personal data. This means any high-risk AI deployment demands clear documentation, audit trails, and risk assessments, building on the same records and controls you manage for data privacy. At the same time, NIS2 directives are now in force across all EU member states, pushing for higher standards on security and incident reporting, especially where personal data is involved.
The effect: many privacy and security teams are merging their playbooks. Recent industry surveys show that around 90% of companies have deepened their privacy programs as these overlapping rules take hold. Instead of treating GDPR as an isolated checkbox, buyers now look for platforms and workflows robust enough to support broader enterprise risk, from AI governance to cyber resilience—because auditors are asking for all of it, and they are asking in the same cycle.
Identity and access management for accountability
Another core piece of the GDPR puzzle is identity and access management. At its heart, GDPR demands that only authorized people have access to personal data, and that every access attempt leaves an auditable trail.
Robust identity and access management (IAM) tools help deliver on both fronts by:
Restricting sensitive data only to those who need it, whether that’s through integration with major identity providers like Okta, Azure AD, or Google Workspace.
Logging who accesses what, when, and from where—building a documented record to demonstrate due diligence if questions ever arise.
Automating periodic access reviews, so permissions don’t quietly grow stale over time or following team changes.
In practice, this isn’t just a checkbox exercise. When DPAs audit for compliance, gaps in access logs or unclear permissioning are among the fastest ways to raise red flags. A comprehensive IAM setup means you can not only protect user data, but also show, step by step, how every access point was tracked and controlled—turning GDPR’s accountability principle into a repeatable process.
Bridging compliance frameworks: Making evidence work smarter, not harder
For organizations facing overlapping requirements—think GDPR, SOC 2, ISO 27001, or HIPAA—compliance can all too easily become a game of redundant paperwork and duplicate audits. But it doesn’t need to be. Cross-framework evidence mapping is the practice of aligning your controls and documentation so that a single piece of evidence can satisfy multiple standards at once.
Here’s what matters:
Efficiency under pressure: Why collect the same user access report—or validate encryption controls—twice or three times? By mapping where GDPR requirements align with those in ISO 27001 or SOC 2, you can use the same audit evidence, reducing repetitive work.
Automated gap analysis: Many modern compliance platforms now offer tools that show not only which controls “overlap,” but also highlight where your documentation or processes fall short for one standard but pass muster for another. This helps teams prioritize action where it actually counts.
Technical integration: Streamlining compliance is easier when your evidence lives in integrated, cross-compatible systems—think automated control testing, audit trails, and real-time status tracking that work across privacy, security, and risk management objectives.
There’s a tradeoff, of course. If your only need is rapid cookie banner deployment or focused consent management, this kind of cross-framework approach can feel like overkill. But for organizations juggling privacy, trust, and information security initiatives—all under scrutiny from legal, IT, and external auditors—a mapped, multi-framework strategy shifts compliance from a cost center to an operational advantage.
Does GDPR require an external audit or formal certification?
Not in the way some security standards do. GDPR compliance is fundamentally self-assessed—there’s no official GDPR certification scheme, nor a requirement for an external audit like you’d see with SOC 2 or ISO 27001. Instead, organizations are expected to implement the right measures internally and be ready to demonstrate compliance if a supervisory authority comes knocking.
This means the real responsibility is on you to make sure you have accurate records, robust controls, and clear documentation that can stand up to scrutiny—whether it’s a formal inquiry from a data protection authority or a due diligence request from a customer. While the GDPR mentions the concept of approved certification mechanisms, as of mid-2026, a unified, widely recognized certification process for GDPR still does not exist across the EU.
In short: you’re not chasing a stamp of approval, but you do need to be audit-ready. That’s why well-organized logs, steady monitoring, and transparent consent management are as much about practical survival as they are about legal compliance.
Who benefits most from privacy compliance platforms with managed services?
These platforms shine for organizations that need more than just off-the-shelf software. If your team is lean, stretched across multiple responsibilities, or lacks in-house privacy expertise, managed services and regulatory advice can bridge those gaps quickly.
They’re particularly useful when:
Your business is scaling fast but cannot yet justify a dedicated privacy team.
You operate across several regions with differing privacy requirements—think GDPR in Europe, CCPA in California, and perhaps LGPD in Brazil.
Legal updates, compliance deadlines, and regulator expectations (like those from the CNIL or European Data Protection Board) seem to change faster than your internal policies can keep up.
You need ongoing support to translate high-level regulations into practical steps for your websites, apps, or data workflows.
In short, managed privacy solutions matter most for growing companies who want to stay ahead of compliance without hiring a squad of lawyers or privacy specialists, and who see value in combining technical controls with clear, adaptive policy guidance.
Top alternatives for compliance automation as your business grows
For teams feeling boxed in by their current compliance platform, it helps to look beyond the usual feature lists and focus on fit for your business as it scales.
So if you’re finding your platform struggles to keep up—or just isn’t as nimble as your roadmap—you’re not alone. The market has matured quickly, and a handful of alternatives offer strong compliance automation without the ceiling that comes from outgrowing your first tool.
Here are several notable options that growing businesses often consider when making the jump:
Drata: Known for continuous security monitoring and streamlined workflows, it’s suited for organizations adding new frameworks and looking to integrate compliance into their development processes.
Secureframe: Focuses on automating evidence collection, vendor risk management, and audit preparation across various standards, making it popular with rapidly growing tech firms.
A-LIGN: Offers a blend of automation with white-glove auditor support, useful for companies ready to graduate from self-service checklists to more robust, guided compliance.
LogicGate: Provides a flexible governance, risk, and compliance (GRC) platform that can adapt as workflows get more sophisticated and risk landscapes evolve.
AuditBoard: Strong in risk management and audit management, it can be a logical step for businesses looking for centralized oversight and greater transparency across risk and compliance initiatives.
Each of these platforms addresses unique pain points that emerge as businesses expand—whether you need tighter integration, more automation, or simply better support for new compliance requirements. That way, your compliance workflows can scale at the same pace as your business, not the other way around.
Automating GDPR compliance with other frameworks
For teams juggling multiple standards—GDPR, SOC 2, ISO 27001—the idea of streamlined compliance isn’t fantasy. Cross-framework automation platforms now let you map evidence and controls across different regimes. That means you can collect relevant documentation or logs once and apply them wherever they fit: privacy, security, or both.
This isn’t just about saving time (though you will). It’s about reducing duplicative effort during audits, clarifying responsibilities internally, and making sure nothing slips through the cracks as requirements overlap. The net result is a compliance workflow that keeps pace with both European data rights and broader information security frameworks—no separate fire drills for every acronym.
Training and awareness tracking for GDPR compliance
Even the tightest software can’t protect your organization if employees aren’t trained on privacy basics. Since GDPR requires that training isn’t just conducted, but also well-documented, the “best GDPR software” should go beyond banners and policies—providing built-in support for training and awareness.
Here’s what to look for:
Integrated training modules: Many platforms include privacy and security modules built right in, or they integrate smoothly with established corporate learning tools like SAP SuccessFactors, Cornerstone, or even LMS plug-ins.
Automatic tracking and reminders: Good solutions will help you monitor who’s completed required modules, send automated reminders for overdue training, and generate audit-friendly records without manual hunting and pecking.
Customization and region-specific topics: Look for tools that let you tailor training content for different roles, locations, or legal regimes, ensuring your sales team in Paris and your developers in Berlin both get what matters most to them.
Done right, compliance software won’t just throw a training checklist over the wall. It should help you build muscle for ongoing education—with traceable proof, not just good intentions.
Top Alternatives to Major Compliance Platforms
When choosing compliance software, it’s not just about the headline brand—it’s about the frameworks your business needs to meet today and where you want to grow tomorrow.
Here are a few proven compliance automation platforms, each with strengths for different team sizes and regulatory needs:
VComply: Known for intuitive controls, this platform supports a wide range of international standards beyond core GDPR and CCPA, and is often favored by smaller legal and operations teams seeking quick onboarding.
Drata: A popular fit for fast-growing companies that want automation-first compliance monitoring, with connectors for cloud-based environments and streamlined audit preparation.
Secureframe: Useful if your priority is scaling across ISO, SOC, HIPAA, and beyond—all within a single dashboard.
TrustArc: Favored by privacy professionals for its mature suite of global compliance features, particularly for enterprises operating across multiple jurisdictions.
LogicGate: Ideal for organizations that want to build highly customizable workflows around risk, compliance, and vendor management.
Choosing among these alternatives is less about a single “top” pick and more about mapping your business’s real compliance bottlenecks to the platform that best fits—not only for today’s needs, but those a year from now.
What are the leading compliance management software solutions for 2026?
A few names come up again and again in 2026 buyer checklists. The landscape is crowded, but a handful of platforms have established themselves as reliable control layers for compliance management, security questionnaires, risk monitoring, privacy workflows, and third-party oversight.
The most common use cases:
Compliance management and policy workflows: These tools centralize policy updates, track changes against regulatory shifts, and provide audit trails your legal and operations teams can actually use.
Audit and assessment automation: Automated evidence collection, audit readiness checks, and digital workflow steps tailored to SOC 2, ISO 27001, GDPR, and other frameworks.
Privacy and preference management: Solutions supporting granular consent, user preference centers, and downstream integration with marketing, sales, and data teams.
Risk and vendor management: Unified dashboards to flag third-party risks, automate due diligence, and keep the business ready for a surprise questionnaire from a regulator—or your board.
Security questionnaire response automation: Platforms designed to route, complete, and store responses for security reviews from customers, prospects, or partners.
Widely adopted solutions in 2026 include platforms like OneTrust, Osano, DataGrail, TrustArc, AuditBoard, Hyperproof, Loopio, Conveyor, and Secureframe. These tools are chosen for their degree of automation, robust integration options, and ability to adapt as your risk or compliance surface changes (especially for fast-moving organizations scaling globally).
What matters most in this ecosystem is not grabbing the product with the most line items on the comparison table, but understanding which platform best fits your mix of regulatory exposure, operational requirements, and internal resource constraints.
If you’re weighing your options, focus on clear answers to three questions:
Where does your compliance process break today?
Which new regulatory surfaces is your business exposed to in 2026?
What level of automation and integration will your teams actually use and maintain?
That’s the context most buyers need before sorting through specific platforms advertised as the “best compliance management software” this year.
Reporting and audit capabilities for access reviews
A credible access review system should make the review process fully visible—not just for auditors, but for internal teams who need to demonstrate accountability.
Look for solutions that provide:
A complete timeline of access review activity, including what was reviewed, by whom, and when decisions were made.
Intuitive dashboards where auditors can easily revisit previous reviews, confirm outcomes, and inspect the rationale behind each decision.
Exportable reports suitable for compliance checks—think CSV, PDF, or formats compatible with tools like OneTrust or Drata.
Ongoing visibility into both reviews in progress and those completed, with the ability to drill down into specific user, group, or resource histories.
Robust software won’t merely collect logs; it will organize this evidence in a way that supports both internal oversight and external audit requests, making ad hoc spot checks or formal evidence collection far less painful.
6. Don’t overlook third-party and vendor compliance
Even if your own consent workflows are airtight, third-party vendors can introduce real GDPR risk.
Managing vendor compliance isn’t one-and-done. A robust approach involves:
Cataloging all data processors and sub-processors (not just the obvious ones).
Tracking Data Processing Agreements (DPAs), including renewal dates and scope.
Regularly revisiting vendor GDPR policies and certifications—especially for tools that touch personal data.
Setting up systematic reviews, either through annual assessments or integrated platforms that flag expired or missing DPAs.
Monitoring for changes—like new features or acquisitions—that could alter a vendor’s risk profile.
It’s easy to assume high-profile brands are always compliant, but even companies like Salesforce or Meta can change terms or add features quickly. For extra confidence, some organizations use tools like OneTrust or TrustArc to manage vendor compliance workflows across their stack.
Ultimately, vendor risk management requires both diligence and documentation. If you can’t answer when a vendor was last reviewed or produce signed DPAs on request, there’s a gap in your compliance story.
Aggregating account access: integration and consolidation options
If your environment includes a mix of SaaS tools, HR systems, and legacy infrastructure, aggregating account access data effectively often comes down to the right combination of integrations and import choices.
Today’s top platforms come with a library of pre-built connectors to streamline syncing. For example, it is increasingly common to see integrations for communication systems like Zoom or Intercom and HR data sources such as Personio, BambooHR, or Workday. These integrations typically pull account and HRIS data automatically, making it straightforward to centralize who has access to what.
For systems that do not have a ready-made integration, most solutions now support manual uploads—letting you bring in access files or logs directly from those harder-to-reach tools. Flexible import options matter here, especially when you’re operating with a few niche providers in the mix.
Finally, after connecting or uploading, you should be able to browse a unified view of all systems in scope and select which ones to include for reviews or audits—no need for multiple spreadsheets or toggling between dashboards.
By focusing on integration depth and practical import support, you gain a single vantage point on access controls, regardless of the underlying systems.
7. Track and verify changes to user access
Effective compliance systems must do more than just log access changes—they should make verification and follow-up easy.
Look for a system that helps your team:
Quickly spot accounts with recent permission changes, so nothing slips through the cracks.
Collect and display remediation evidence automatically for every integrated environment—think Okta, Google Workspace, or Azure.
Offer a straightforward way to attach and organize manual proof for systems that aren’t yet integrated, so no access decision goes undocumented.
The key is transparency. The best platforms make it obvious who changed what, when, and how that change was resolved—giving you an audit trail you can actually use.
8. Insist on real-world vendor risk handling
Vendor risk isn’t just a checkbox—it’s where compliance tangles usually start.
When comparing your options, drill into how each tool helps you track and manage the third parties in your stack. Look for features that make it easy to:
Maintain a live register of all data processors and sub-processors, not just the ones you remember at audit time.
Store and update Data Processing Agreements (DPAs), with version histories and renewal reminders, so contracts don’t go stale.
Monitor ongoing vendor compliance against regulation changes—especially for big services like AWS, Salesforce, or niche SaaS tools that quietly process personal data.
Flag when a vendor drops the ball, like failing a security assessment or not updating to meet new GDPR/CCPA requirements.
A strong vendor risk workflow should make it painfully obvious if something is out of date or if a weak link puts your whole privacy program at risk. If the system treats your vendors as “set and forget,” keep looking.
The real question behind “best GRC software” for your team
When it comes to finding the best Governance, Risk, and Compliance (GRC) platform in 2026, it’s less about glossy feature lists and more about matching each tool’s strengths to your actual workflow.
For startups and lean teams, the right fit often means automation that slashes manual checks without overwhelming configuration screens.
Security-focused organizations usually need deep integrations with existing threat management or identity systems and robust audit-ready reporting.
Businesses scaling into multiple regions or verticals will look for GRC solutions able to orchestrate policies and map controls across diverse legal and operational requirements.
Some tools now bring AI-powered mapping of risks and controls, integrations that connect policies directly into HR, finance, and IT systems, and dashboards intended to keep executive teams aligned without needing a consultant for every process change.
In the end, the “best” GRC software is the one that can flex to your team’s structure—whether that means rapid onboarding for a fresh startup, granular control for technical teams, or scalable automation for enterprises bridging compliance frameworks from SOX to ISO 27001.
Comparing top compliance audit software platforms for 2026
With privacy demands rising and regulatory deadlines looming, more businesses are searching for audit platforms that don’t just tick the boxes, but actually reduce audit headaches and reveal real gaps. But what makes one audit tool stand out from another? The best compliance audit software for 2026 is less about flash—more about substance and fit.
Here’s how the leading audit platforms tend to weigh up:
What sets a platform apart:
Comprehensive coverage: The strongest tools offer audits against SOC 2, ISO 27001, GDPR, HIPAA, and other major frameworks, all under one roof. This can be especially vital as requirements stack up across regions.
Automated controls testing: Instead of relying on yet another spreadsheet, many modern platforms automatically test and monitor controls by connecting to cloud infrastructure, HR, code repositories, and security tools.
Evidence collection: Top software streamlines the nasty business of gathering screenshots, logs, and records, and stores them so auditors (and your own team) can verify things without playing email tag at 2am.
Continuous monitoring: Platforms are moving beyond point-in-time checks and offer ongoing monitoring for risks and control failures, making compliance less reactive and more resilient.
Audit-readiness dashboards: Fine-tuned reports and visualizations help you see, at a glance, where you stand—and what needs attention—before an external auditor ever shows up.
Comparing pros and cons:
Ease of deployment: Some tools are turnkey for cloud-native teams, while others require more onboarding for custom or hybrid environments.
Integration breadth: The difference often comes down to integrations—how well does the tool connect to your existing stack? Look for one that supports your key infrastructure, from AWS and Google Cloud to Slack, Okta, and Jira.
Scalability: Multi-entity, multi-standard support is a must for teams operating across geographies or business lines.
User experience: The best audit software keeps things relatively human. Look for clear workflows and helpful support, not clunky portals or dense jargon.
Pricing: Transparent, modular pricing is becoming more common. Be wary of hidden costs for additional standards, users, or integrations.
In practice, picking the “best” platform comes down to your audit scope, team skill set, and the risk environments you’re facing right now. Instead of chasing the shiniest feature list, focus on the tool that can address your real compliance bottlenecks—and grow with you as mandates evolve.
Remediation workflows for managing access change requests
When access reviews turn up permissions that need to be changed, the right remediation workflow becomes essential—not just to log the issue, but to make sure it’s truly resolved.
A robust system should let reviewers assign tasks directly to the appropriate system owners. This creates clear accountability: the person responsible knows precisely which access needs to be removed or modified.
To stay organized (and to actually get things done), integration with a task tracker—like Jira or ServiceNow—can help. This way, each access change request can spin up a proper ticket, offering a transparent view into its status throughout remediation. You get:
Centralized tracking of who is handling each change
Automatic updates as requests move from open to resolved
A historical audit trail for compliance checks later
With workflows like this, it’s possible to close the loop on every review—no more guessing whether a risky permission was actually revoked, because you have transparency from assignment all the way through completion.
How user access reviews work in compliance platforms
Access review features in compliance platforms are designed around control and simplicity, letting buyers focus on actual oversight rather than endless admin.
Here’s how this usually plays out:
Assign a reviewer: Most systems let you select who should review access for each tool or dataset, along with setting a clear due date to keep things moving.
Automated nudges: Expect notifications and reminders to nudge reviewers before deadlines, preventing the classic “lost in inbox” problem.
Risk detection: Accounts flagged as high-risk—like when an employee leaves the company or switches departments—are automatically highlighted for review.
Streamlined interface: Reviewers get a single dashboard to see who has access, revoke or approve accounts, and add context or notes as decisions are made.
Progress tracking: You’ll find clear indicators showing which reviews are complete, which accounts need action, and what’s still pending.
Bulk actions: The better platforms let you quickly filter, sort, and adjust user access by role or title, sparing you from tedious one-at-a-time changes.
With these core capabilities, compliance software handles the nuts and bolts of access reviews, ensuring that records remain both actionable and auditable—whether for internal checks or eventual regulator scrutiny.
4. Platforms that automate data subject rights and live data mapping
Modern privacy programs rarely stop at the front door. Once you offer users ways to exercise their rights—be it access, deletion, or portability—the real challenge is tracking their data across a wild web of SaaS vendors and homegrown tools. That’s where specialized automation platforms enter the picture.
These tools distinguish themselves by:
Live mapping of personal data across connected systems, using no-code integrations to surface where information actually sits.
Automated fulfillment workflows for data subject requests (DSARs) like access or erasure, reducing manual work even at volume.
Orchestration of consent and preferences across internal systems and third-party platforms, ensuring consistent enforcement downstream.
Policy-driven deletion and retention, automatically applying rules regardless of whether the data lives in a CRM, analytics database, or support app.
Centralized privacy request portals for end users, giving people a simple way to track the status of their requests.
Take for instance how a live data inventory doesn’t just make audits easier—it gives privacy teams a continuous, current map of their data flows, which is essential when regulations and internal policies change overnight.
If your reality involves juggling hundreds of SaaS integrations, or making sense of where a user’s data actually lives, this automation category helps you scale privacy rights from a legal checkbox to a smooth operational machine.
Data discovery and inventory for privacy and security: How BigID handles the hard part
For organizations facing sprawling data ecosystems, the real stumbling block often isn’t collecting consent—it’s simply figuring out where personal data lives in the first place, and what’s tucked away in every nook and cranny of the stack.
BigID tackles this by going deep on automated data discovery and classification. Rather than making teams hunt through spreadsheets and legacy systems, it uses machine learning and AI-driven scans to map out structured, unstructured, on-prem, and cloud data sources. The result is a live, granular inventory tied directly to data privacy requirements like Records of Processing Activities (ROPA), data minimization, and Data Subject Access Requests (DSARs).
A few ways their platform stands out:
Unifies automated scanning across databases, cloud storage, and less-mapped systems
Builds real-time, detailed data inventories to serve privacy and governance needs
Applies risk scoring and recommends fix-it workflows for sensitive personal data
Offers an extensible app ecosystem for custom privacy, security, and governance tasks
Enables policy-driven data retention and deletion—helpful for demonstrating compliance or quickly responding to an access request
Plugs into privacy and security tools elsewhere in your stack so that data insights don’t stay siloed
The upshot? When the challenge is simply getting a handle on the data footprint—especially in a fast-changing or heavily federated IT environment—approaches like this turn data inventory from a sticky guesswork exercise into a managed, repeatable process that privacy and security teams can act on.
TrustArc features for privacy compliance and risk management
TrustArc, for example, builds its platform around several key pillars designed for teams that need a robust approach to privacy management.
Risk Management: Tools for mapping, assessing, and documenting privacy risks, including pre-built workflows for data protection impact assessments (DPIAs) and a structured risk register for ongoing tracking.
Individual Rights Requests: Modules to triage and respond efficiently to data subject access requests (DSARs), making it easier to stay on top of regulatory timelines and maintain an audit trail.
Cookie Consent and Compliance: Capabilities to automatically scan websites for cookies and trackers, categorize them, and deploy customizable consent banners that adapt to both legal and user experience needs.
Privacy Program Support: Access to privacy consultants and managed services, helping teams design and mature their privacy programs without building everything from scratch.
Demonstrable Compliance: Integrated frameworks for privacy assessments and certification processes that let organizations show clients, partners, or regulators tangible proof of compliance.
Regulatory Intelligence: Dashboards and alerts that surface updates from global privacy laws, giving teams early warning and actionable guidance as rules evolve.
These features aim to help privacy teams manage risk holistically, automate complex tasks, and document compliance in a way that holds up—even as the regulatory map continues to redraw itself.
Advantages and disadvantages of advanced privacy program management tools
When considering the most advanced privacy management platforms—think the OneTrusts, the TrustArcs, and peers who dominate Gartner’s magic quadrants—buyers find a mix of powerful features and meaningful challenges. Here’s what stands out:
Advantages:
Comprehensive privacy feature set
These tools go far beyond cookie popups. They offer mature modules for just about every privacy function: consent collection, preference management, data inventory, data mapping, reporting, or even automating DPIAs and managing data ethics initiatives. For organizations with intricate privacy needs, that breadth is hard to beat.
Up-to-date regulatory intelligence
With privacy regulations shifting from California to Quebec to Düsseldorf, the best platforms maintain live databases tracking laws, rules, and guidance worldwide. This helps your team stay compliant without relying on endless spreadsheets or late-night legal briefings.
Recognition and trust
Regulators and industry groups know these brands, which can make audits smoother and internal buy-in easier—especially in regulated sectors or global organizations.
Disadvantages:
Implementation and management complexity
The flip side of all those bells and whistles is complexity. Standing up these platforms (and keeping them running) often requires dedicated resources, outside professional services, or both. Smaller teams may find the learning curve steep if they don’t have a privacy ops leader or strong IT support.
Modular pricing can escalate quickly
Most advanced vendors price their software by feature, geography, or use case. Costs can mount fast as your needs grow, with “all-in” deployments sometimes outpacing leaner teams’ budgets.
Less focus on unified security automation
While many leading privacy platforms offer basics like SOC 2 support, their real strength is privacy—not holistic cybersecurity compliance across frameworks like ISO 27001 or PCI DSS. If your priority is integrating privacy with broader security automation, gaps may remain.
So, for organizations handling complex, multi-jurisdictional privacy programs, the feature depth and regulatory coverage can be invaluable. However, that comes bundled with higher complexity, budget pressure, and the need to plan carefully for integration with broader security and compliance priorities.
Turning GDPR Compliance Into a Competitive Edge
Done right, GDPR compliance is more than a checkbox—it’s leverage.
Why? Because in 2026, demonstrating responsible data practices and user-centric transparency still builds trust where it matters. It’s not just regulators watching; partners like Google require certified compliance, and privacy-aware users are quick to vote with their clicks. Companies that can show consent is more than a formality—by making choice clear, records audit-ready, and withdrawals low-friction—stand out against those hoping no one looks under the hood.
Brands like Apple, Mozilla, and Proton have shown that treating privacy not as overhead but as a core value sends a signal. It unlocks doors to new regions and partnerships, reduces late-stage contract friction, and can even speed up vendor onboarding with large organizations. For SaaS providers, GDPR-aligned processes can shorten sales cycles. For publishers and ecommerce, it builds loyalty at a time when third-party data is fading.
In short, the organizations that operationalize compliance—embedding it into product and marketing—don’t just reduce risk. They win trust and keep the market open even as the rules evolve.
The three buckets hidden inside “best GDPR software”
1. Consent platforms for websites, tags, and advertising flows
This is the first bucket many people mean when they search for best GDPR software.
Here the questions are practical:
Can the tool support equal accept and reject paths?
Can it prevent optional technologies from firing before consent where prior consent is required?
Can it pass consent signals into tag managers, analytics tools, and ad systems cleanly?
Can it keep up when marketing, product, and engineering all touch the stack?
On its current product page, OneTrust positions its cookie consent product around scanning for cookies, tags, trackers, pixels, and beacons, plus regional banners and pre-built martech integrations. That makes this bucket useful when your risk lives on public websites and in advertising or analytics workflows.
2. Policy and notice software for lean teams
Some businesses do not need a large privacy operations rollout first. They need disclosures, cookie notices, and legal text that stay maintainable as the site changes.
This bucket matters when the core problem is not only consent collection, but also keeping privacy and cookie documentation current without rewriting it manually every month.
On its current product page, iubenda emphasizes legal updates, a large clause library, and generator-based privacy and cookie policy workflows. For smaller teams, that can be more realistic than buying a large CMP first and hoping the policy layer sorts itself out later.
3. Preference and enforcement platforms for multi-system programs
The third bucket is for organizations whose real problem starts after the banner.
They may already know how to collect consent. What they need is a system that can sync preferences across websites, apps, backend tools, and downstream data uses with a durable record of what happened.
Transcend’s current consent and preference positioning leans into that exact need, describing enforcement across web, mobile, and backend environments. If your environment is complex, the best GDPR software may look less like a banner product and more like a decision layer.
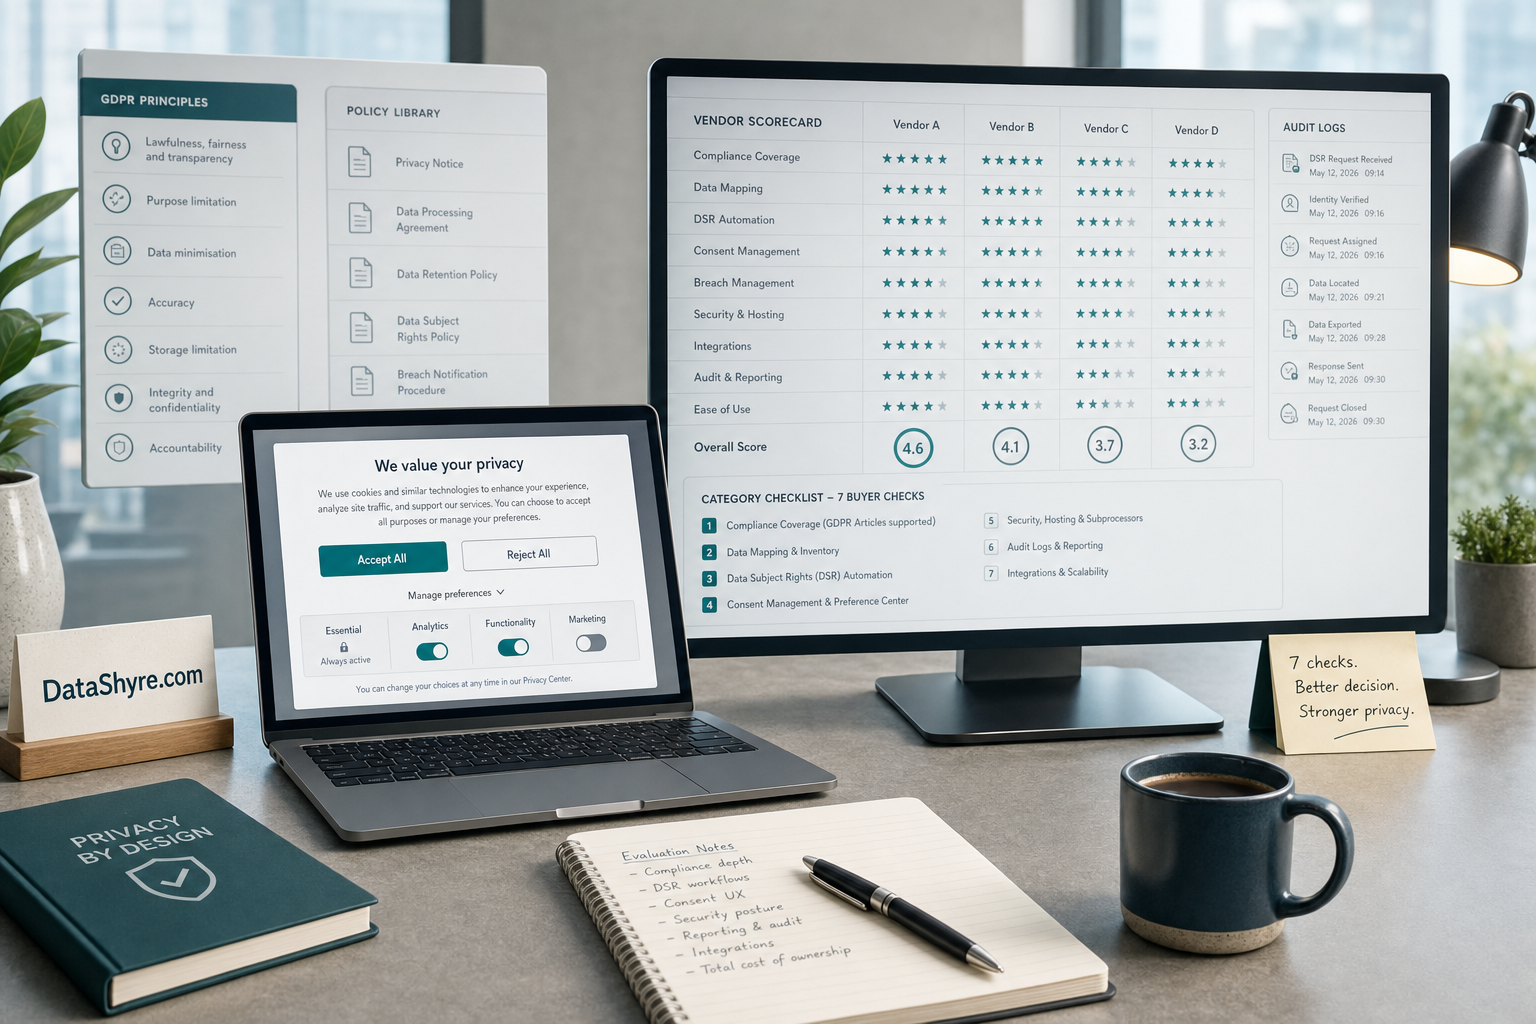
7 buyer checks before you choose
1. Start with the failure you are actually trying to fix
Do not ask which platform is “best” before you ask what is broken.
If non-essential tags fire before consent, start with runtime control. If your policies are outdated or inconsistent, start with the notice layer. If consent exists in one system but not in the others that use the data, start with enforcement and orchestration.
The wrong purchase often happens when a team buys banner software for a systems problem or a policy generator for a signal-routing problem.
2. Test fair choice, not just banner polish
This is still one of the fastest filters.
If Accept all is instant but Reject all is visually buried, the software is already making your compliance harder. CNIL’s current notice is useful here because it says the point plainly: rejecting cookies should be just as easy as accepting them.
For the best GDPR software, choice design is not decoration. It is part of whether the consent you collect is defensible.
3. Verify prior blocking on a real page, not a demo
For EU and UK consent flows, the visual interface is not enough.
Google’s current consent mode guidance still says the default consent state should be set before measurement commands run, and updates should be tracked on the page where they occur before any page transition. That is exactly why polished demos can mislead buyers. A banner can look compliant while tags still fire too early on the real site.
Ask for a live browser walkthrough on pages that actually matter:
homepage templates;
campaign landing pages;
pages with chat, video, forms, or maps;
logged-in or checkout flows if they use optional tools.
4. Separate EU/UK consent needs from California opt-out handling
One workflow rarely covers every region cleanly.
In the EU and UK, the practical question is often whether optional storage-and-access technologies stay off until valid consent exists. In California, the workflow can shift toward sale-or-sharing opt-out handling and browser-level preference signals such as GPC.
That matters because a tool can look strong in an EU-style opt-in demo and still leave a California gap.
5. Follow the signal into the downstream stack
The best GDPR software should not leave consent stranded inside its own dashboard.
For most teams, the signal has to reach:
tag managers;
analytics tools;
advertising systems;
embedded third-party services;
CRM or marketing automations;
internal records that support support, legal, and engineering teams later.
If the handoff is brittle, the visible interface is only a partial solution.
6. Demand usable records, not just logs
Sooner or later, someone asks what a person saw, chose, and changed.
Your team should be able to answer:
What did the user see?
What categories or purposes were enabled?
What did the user choose and when?
Which downstream tools changed behavior after that choice?
Could the user return later and revise or withdraw the decision?
If the software cannot answer those questions clearly, it is thinner than it looks.
7. Check for post-launch drift
A clean implementation at launch is not the finish line.
New tags get added. A plugin changes load order. Marketing introduces another vendor. Engineering moves scripts for performance. The banner still looks correct while the stack underneath it quietly changes.
The best GDPR software is the one that makes that drift easier to detect, test, and explain.
A simple way to shortlist vendors this week
If I were comparing best GDPR software options today, I would do this in order:
Classify each product as primarily CMP, policy tooling, or downstream enforcement.
Test whether refusal is as usable as acceptance.
Inspect what fires before consent on a real page, not a sales walkthrough.
Check whether Google publisher requirements matter to your revenue model.
Check whether the product has a clean answer for California GPC handling where relevant.
Export records and decide whether another team could understand them later.
Re-test the shortlist against how your stack will look after six months of changes.
That short sequence usually tells you more than a long vendor matrix.
Bottom line
The best GDPR software in 2026 is the one that matches the layer where your risk actually lives.
If your problem is website consent and tracking control, evaluate CMP behavior ruthlessly. If your problem is staying current on disclosures, prioritize maintainable policy tooling. If your problem is fragmented consent across systems, buy for enforcement, not just presentation.
The ICO captured the broader goal well on April 29, 2026, when William Malcolm said people need:
“meaningful control over how their data is used.”
>
William Malcolm, ICO
That is still the right buying test. If the product cannot create meaningful control in the live stack, it is not the best GDPR software for your team, no matter how polished the demo feels.