
Do I Need a Cookie Policy on My Website in 2026? 7 Live Checks Before You Publish
If you are asking do i need a cookie policy on my website on November 14, 2026, the practical answer for most real businesses is yes.
Not because a cookie policy magically makes tracking lawful, but because modern websites almost always need a clear public explanation of what storage and access technologies they use, why they use them, what choices users have, and how those choices actually work.
That answer gets even clearer when your site reaches EU or UK visitors. Your Europe still says some cookies require consent before they are set, that users need “clear and comprehensive information” about the cookies and their purpose, and that it must be as easy to withdraw as to accept. The ICO still says “Silence or inactivity doesn’t qualify” as consent and expects refusal to be as easy as acceptance.
If you want the companion reads first, start with our guides to cookie policy, cookie law, and privacy policy for website. This page stays narrower. It answers the yes-or-no part of do i need a cookie policy on my website and shows what teams still miss in the live implementation.
If your banner copy, tag manager, and policy page are drifting apart, DataShyre can help with consent implementation, runtime privacy testing, and policy-to-production cleanup before that gap turns into a complaint.
1. If your site uses non-essential cookies or similar tracking, assume the answer is yes
The fastest way to answer do i need a cookie policy on my website is to stop thinking only about traditional browser cookies.
The real scope is broader:
- cookies;
- pixels and tags;
- SDK-style tracking on embedded tools;
- local storage or similar browser-side identifiers; and
- third-party technologies that profile, measure, personalize, or advertise.
If those technologies are present, a serious website usually needs a dedicated cookie policy or a clearly labeled cookie section that explains what is happening in plain language.
For EU-facing teams, the official baseline is still straightforward: some cookies cannot be set until the user consents, and the user needs purpose-specific information first. For UK-facing teams, the same practical message holds. If the site uses non-essential analytics, advertising, or third-party tracking, the words on the page need to explain the live behavior.
2. A privacy policy alone is often not enough
Some teams hear do i need a cookie policy on my website and answer:
No, we already have a privacy policy.
That is usually too thin.
A general privacy policy often explains broad collection, use, sharing, retention, and rights. A cookie policy should usually do something more operational:
- identify the categories of cookies or similar technologies in use;
- explain what each category does;
- describe whether third parties are involved;
- show what choices the user can make; and
- tell the user how to revisit those choices later.
If your current privacy policy says only we may use cookies to improve your experience, it probably does not answer the real do i need a cookie policy on my website question. It answers a softer question about whether the site mentions cookies at all.
3. Separate necessary technologies from optional ones before you write anything
This is where most weak policies begin to wobble.
Your Europe still distinguishes cookies that are strictly necessary to provide an online service the person explicitly requested from cookies that need consent. The ICO also continues to treat exemptions narrowly and expects consent only where the technology truly falls outside those narrow exceptions.
So before publishing a cookie policy, classify the live technologies into practical buckets like:
- login, session continuity, and cart support;
- security and fraud prevention;
- analytics and measurement;
- advertising and retargeting;
- personalization;
- embedded video, chat, or social tools; and
- A/B testing or optimization.
If your team calls analytics or ad tech necessary just because marketing wants cleaner attribution, the policy is already drifting away from the runtime truth.
4. For California-facing sites, a cookie banner is not the whole answer
This is an easy place to over-simplify.
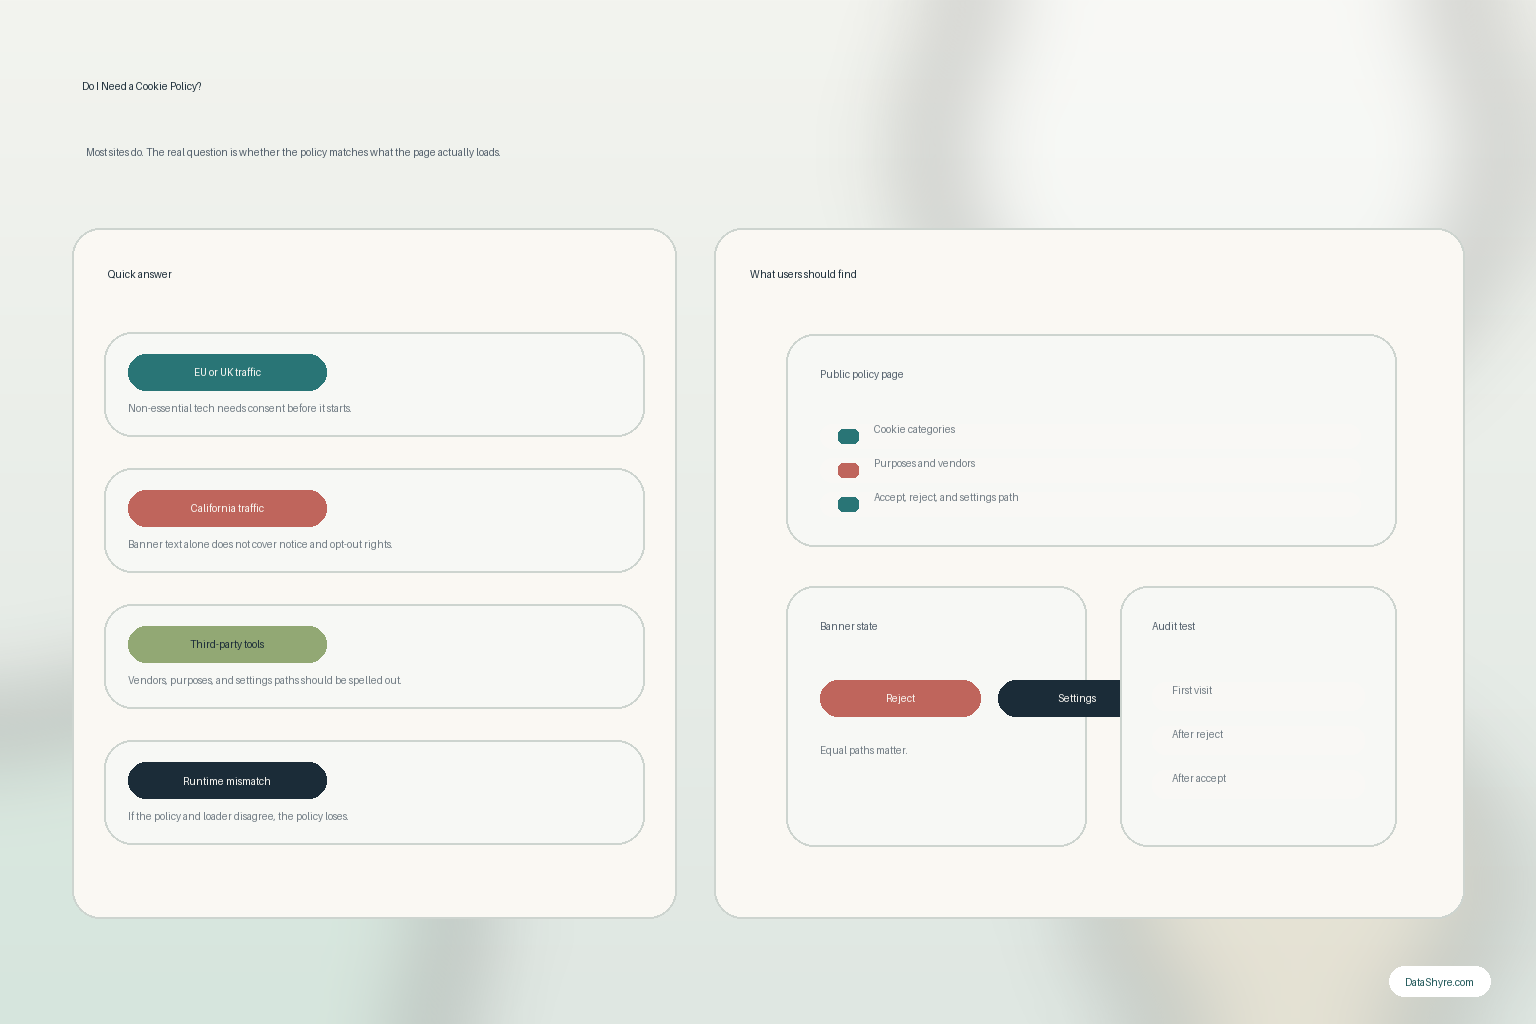
California does not map perfectly to the EU or UK cookie-consent model. The California Attorney General still explains that businesses need a notice at collection, that the notice must be available at or before collection, and that it must link to the privacy policy for fuller detail. The current CPPA regulations also say a cookie banner or cookie controls are “not by itself an acceptable method” for submitting requests to opt out of sale or sharing.
That means the answer to do i need a cookie policy on my website can still be yes even when the bigger California problem is actually:
- missing notice-at-collection language;
- weak privacy-policy disclosures;
- no valid opt-out flow for sale or sharing;
- poor handling of opt-out preference signals; or
- a banner that talks about cookies but never addresses the actual California right.
So the safer view is this: a cookie policy helps explain the technologies in use, but it does not replace the broader California disclosures and opt-out mechanics when those rights apply.
5. A real cookie policy should describe behavior users can actually observe
The strongest answer to do i need a cookie policy on my website is not legal theater. It is operational alignment.
At a minimum, your cookie policy should usually explain:
- which categories of technologies the site uses;
- the purposes for those categories;
- whether any third parties receive data;
- whether consent is required for some categories;
- how users accept, reject, or customize choices;
- how users reopen those settings later; and
- where fuller privacy disclosures live.
For mature programs, it should also stay synchronized with:
- the consent banner;
- the preference center;
- the vendor list;
- the tag manager or loader logic; and
- any regional branching for EU, UK, California, or global privacy controls.
If the policy names three categories but the CMP exposes five, or the policy says rejection stops marketing tags while the page still loads them on first paint, the policy is not doing its job.
6. Test the runtime, not just the copy
The biggest mistake behind do i need a cookie policy on my website is assuming this is mainly a writing task.
It is not.
It is a runtime testing task with writing attached.
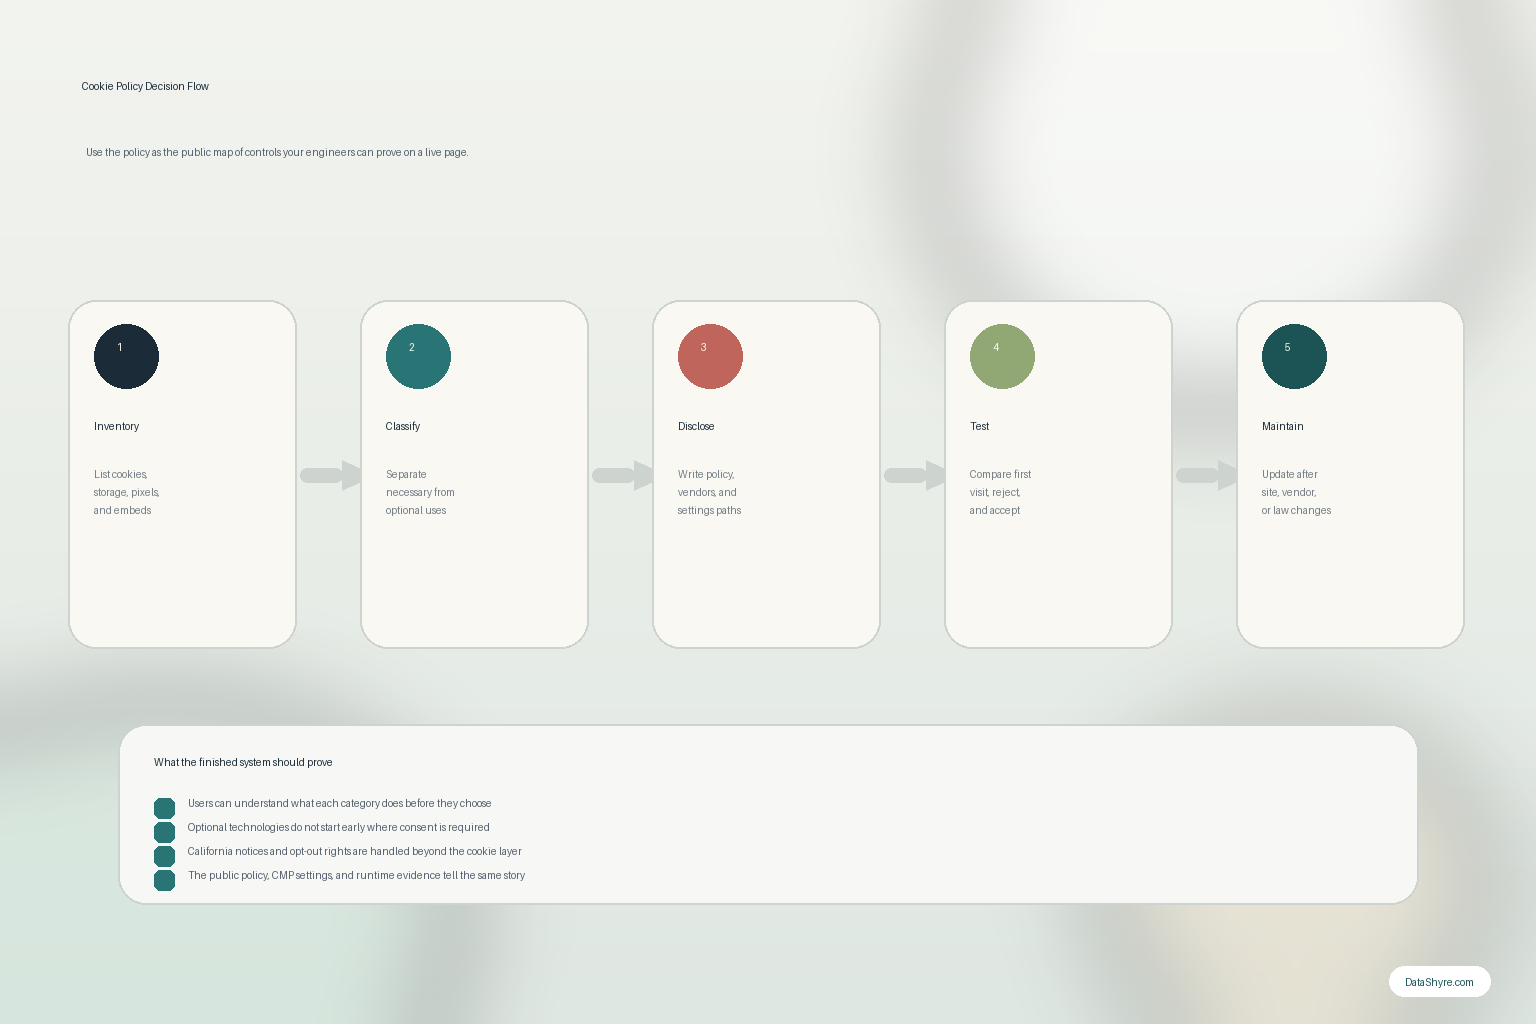
Before you trust your own cookie policy, test:
- what loads on a clean first visit;
- what changes after reject;
- what changes after accept;
- whether the preference center can be reopened later;
- whether mobile and desktop behave the same way;
- whether region-specific logic is firing as intended; and
- whether embedded tools quietly set identifiers before the user acts.
The ICO still warns that inactivity is not consent. That matters because many teams still publish a banner and policy while optional technologies fire before any positive action. In that setup, the policy may be accurate only on paper.
7. If you use a CMP vendor, do not outsource the accountability
A vendor can help, but it cannot absorb the operational responsibility for you.
If your answer to do i need a cookie policy on my website becomes our CMP handles that, slow down.
You still need to confirm:
- the categories are configured correctly;
- the banner offers a real reject path where required;
- scripts and tags wait for the right signal;
- policy text matches the configured purposes and vendors; and
- later edits do not break the original setup.
Whether you use Cookiebot, OneTrust, or a custom implementation, the safest move is to treat the tool as one layer of the control system, not the compliance system by itself. If your team wants help connecting a vendor setup to real runtime evidence and cleaner policy language, DataShyre can help with the implementation review.
A practical answer for this week
If I were answering do i need a cookie policy on my website for a live business this week, I would use this rule:
- if the site uses only narrowly necessary technologies, still document them clearly in a privacy or cookie section;
- if the site uses analytics, advertising, personalization, embeds, or third-party tracking, publish a real cookie policy and test the runtime against it;
- if the site reaches EU or UK visitors, make sure optional technologies wait for valid consent where required;
- if the site reaches California consumers and sells or shares personal information, make sure the broader notice and opt-out requirements are handled too; and
- if the site cannot explain what the page loads before and after user choice, fix that before polishing the wording.
That is the practical answer. For most modern sites, yes is the right starting point. The harder part is making the policy true.
FAQ
Is a cookie policy the same as a privacy policy?
No. They can overlap, but a cookie policy is usually more specific about browser-side technologies, categories, purposes, consent behavior, and settings paths.
Do all websites need prior cookie consent?
No. The stricter prior-consent rules mainly matter for non-essential cookies and similar technologies in places like the EU and UK. Narrowly necessary technologies are treated differently.
Can a cookie banner replace my cookie policy?
No. A banner is a control surface. A cookie policy explains what the technologies do, what choices people have, and how those choices work over time.
If I have California traffic, is the cookie banner enough?
Usually not. California rules can require notice at collection, privacy-policy disclosures, and opt-out mechanisms for sale or sharing that go beyond a simple cookie control panel.