

User Consent Preference Management in 2026: 7 Checks to Keep Choice, Opt-Out, and Proof Aligned
If you are reviewing user consent preference management in late 2026, the wrong goal is a prettier preference center.
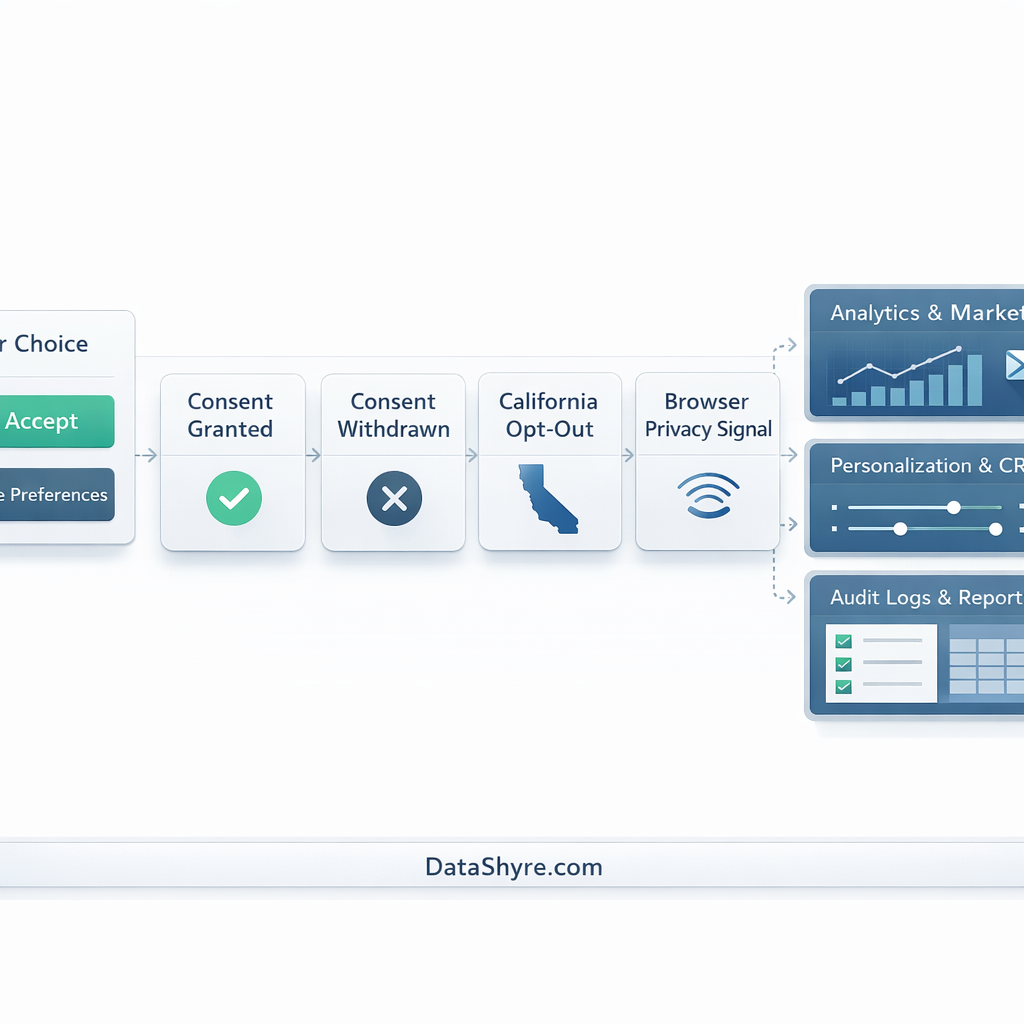
The better goal is a control layer that can tell the difference between consent, a later withdrawal, a California opt-out, a browser-level privacy signal, and a channel preference change, then prove what happened after each one.
That is still the practical direction in current official guidance. The European Commission says valid consent must be “clear and given via an affirmative act” and that withdrawal should be “as easy to use as giving consent.” The UK’s ICO says “Silence or inactivity doesn’t qualify” when consent is required for storage and access technologies. California’s Department of Justice describes Global Privacy Control as a “stop selling or sharing my data switch.”
If you want the closest companion reads first, start with our guides to user consent, user consent management, and GDPR consent requirements. This article stays narrower. It is the seven-check review I would use this week before trusting user consent preference management on a live site or app.
1. Start by separating consent from every other kind of privacy choice
This is the structural check most teams skip.
The European Commission still presents consent as only one lawful basis among several, not the universal answer for every data use. That means a working user consent preference management model cannot flatten every action into one generic yes-or-no field.
At minimum, the system should distinguish between:
- a consent event for a specific purpose;
- a refusal of that same consent request;
- a later withdrawal;
- a California opt-out request;
- a browser or device-level signal such as GPC;
- a channel preference change that is not the same thing as consent.
If those states are stored as one undifferentiated preference, the interface may look tidy while the records become much harder to defend.
2. Make the request specific enough to mean something
Preference management fails quickly when one control covers too much.
The European Commission still says consent must be given for a specific purpose and requested in clear, plain language. The ICO’s current consent guidance also says requests need to be prominent, concise, understandable, and separate from general terms.
So before approving user consent preference management, check whether the interface actually splits:
- analytics from advertising;
- email marketing from SMS;
- first-party messages from partner promotions;
- account settings from optional data uses.
If the user cannot tell what one toggle changes, the system is collecting friction, not meaningful choice.
3. Treat website tracking as its own operational branch
This is where preference design meets runtime behavior.
The ICO finalized its storage-and-access-technologies guidance on April 29, 2026, and that guidance expressly reaches cookies, tracking pixels, fingerprinting, scripts, and similar technologies. It also says that where consent is required, people who do not interact with the consent mechanism cannot be treated as though they agreed.
That means user consent preference management for websites should answer operational questions, not just wording questions:
- what stays blocked before any action;
- what loads only after a valid opt-in;
- what falls inside an exception;
- what changes again when the user withdraws later.
This is why a polished preference center can still fail if the live page behavior ignores the stored state.
4. Keep California opt-outs and GPC out of the wrong bucket
This is one of the easiest places to blur distinct legal models.
California’s Department of Justice still says covered businesses must honor a valid GPC signal as a request to stop the sale or sharing of personal information. The CPPA’s current FAQ page continues to frame California around major privacy rights, including the right to opt out of sale or sharing and the right to limit the use of sensitive personal information.
So for user consent preference management, do not pretend that a California opt-out is always the same action as an EU or UK consent refusal.
In practice, the system should be able to show:
- when a user explicitly opted out through the site;
- when a browser signal triggered the change;
- what sale-or-sharing pathways were affected;
- whether later consent was ever collected for a narrower use.
That separation becomes especially important when one global preference center serves more than one region.
5. Make withdrawal and later changes as strong as the first choice
Teams still over-test the initial opt-in and under-test everything after it.
The European Commission says withdrawal should be as easy as giving consent. The ICO’s consent guidance adds that, where consent is the lawful basis, the withdrawal path should be an easily accessible one-step process where possible and ideally use the same method as the original choice.
So a serious user consent preference management review should test:
- whether the user can reopen the settings without hunting for them;
- whether a revoked permission updates downstream tools quickly enough to matter;
- whether the record clearly shows the old state, the new state, and when the change happened;
- whether the interface stops asking the user to repeat the same answer too aggressively.
If acceptance works instantly but withdrawal gets lost in the stack, the preference system is only half-built.
6. Follow the choice into downstream systems, not just the UI
The visible control is only the front edge of the problem.
Strong user consent preference management has to survive handoffs into tag managers, CRM workflows, mobile SDKs, ad platforms, suppression lists, and support-facing audit views. The CPPA’s regulations page also shows that California’s current CCPA regulations are effective as of January 1, 2026, which is a useful reminder that rights handling and system behavior have to match the current operational rule set, not last year’s assumptions.
The live test is practical:
- if analytics consent is denied, do optional analytics tools stay off;
- if marketing permission is withdrawn, do automations and audiences stop using it;
- if GPC is detected, do sale-or-sharing paths respond correctly for covered flows;
- can support or compliance staff explain which systems were updated and when.
This is usually where the weak spots show up: not in the copy, but in the propagation layer.
7. Keep proof another team can still understand later
The best preference center is still weak if nobody can reconstruct what happened.
The ICO’s guidance on recording and managing consent says organizations should keep records of who consented, when, how, and what they were told. For California programs, the ability to explain rights handling is just as important because teams may need to show how an opt-out request or browser signal changed the treatment of data.
For durable user consent preference management, I would usually want the record to keep:
- the exact notice or interface version shown;
- the purpose, channel, or region-specific control involved;
- the timestamp and source of the action;
- whether the action was a consent, withdrawal, opt-out, or browser signal;
- the downstream systems expected to react;
- any later override, refresh, or status change.
That is what turns a preference center from a UI component into something operations, legal, and engineering can all trust.
A practical review order for this week
If I were auditing user consent preference management today, I would do it in this order:
- separate consent, opt-out, withdrawal, and preference events in the data model;
- split requests by real purpose, channel, and region;
- test website tracking behavior before any click where prior consent is required;
- verify California opt-out and GPC handling on their own branch;
- test the later change and withdrawal paths on live systems;
- confirm downstream tools actually react;
- verify that the proof record still makes sense after a normal release cycle.
That sequence usually tells you more than debating toggle labels in a design file.
FAQ
Is a preference center the same thing as consent management?
No. A preference center is the interface. Consent management is the wider system that determines when consent is needed, how it is collected, how it changes behavior, and how it is proven later.
Should GPC be stored as consent?
Usually no. It is better treated as a separate browser-level opt-out signal so the system can explain what triggered the change and what legal model it maps to.
What is the fastest failure check?
Open a fresh session, refuse the optional uses that require refusal or opt out where the regional model calls for it, then confirm whether the live technologies and downstream systems actually change.
Bottom line
In 2026, the strongest user consent preference management setup is not the one with the most elegant dashboard.
It is the one that keeps consent, opt-outs, browser signals, withdrawals, and preference changes distinct enough to mean something, routes them into the right regional logic, and leaves behind proof another team can still verify later.
If your current model can do that, the preference layer is probably carrying its weight. If it cannot, the fix likely starts in the state model before it starts in the banner or settings UI.
Sources
- https://commission.europa.eu/law/law-topic/data-protection/information-business-and-organisations/legal-grounds-processing-data_en
- https://ico.org.uk/for-organisations/uk-gdpr-guidance-and-resources/lawful-basis/consent/how-should-we-obtain-record-and-manage-consent/
- https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/
- https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/how-do-we-manage-consent-in-practice/
- https://cy.ico.org.uk/about-the-ico/media-centre/news-and-blogs/2026/04/final-storage-and-access-technologies-guidance-published/
- https://oag.ca.gov/privacy/ccpa/gpc
- https://cppa.ca.gov/faq
- https://www.cppa.ca.gov/regulations/
—
Published: October 24, 2026. Updated using current official regulator and government materials available at publication time.