

Consent Management System in 2026: 7 Checks Before You Trust It
If you are reviewing a consent management system in 2026, the useful question is not whether the banner looks finished.
The useful question is whether the system can turn a real user choice into real technical behavior across tags, embeds, analytics, ad tech, privacy requests, and audit records. Plenty of teams still buy a banner and assume they bought enforcement. Those are not the same thing.
If you want the closest companion reads first, start with our guides to consent management platform, consent management process, and cookie consent requirements. This page is narrower. It is the seven-check review I would use this week before trusting a consent management system on a live property.
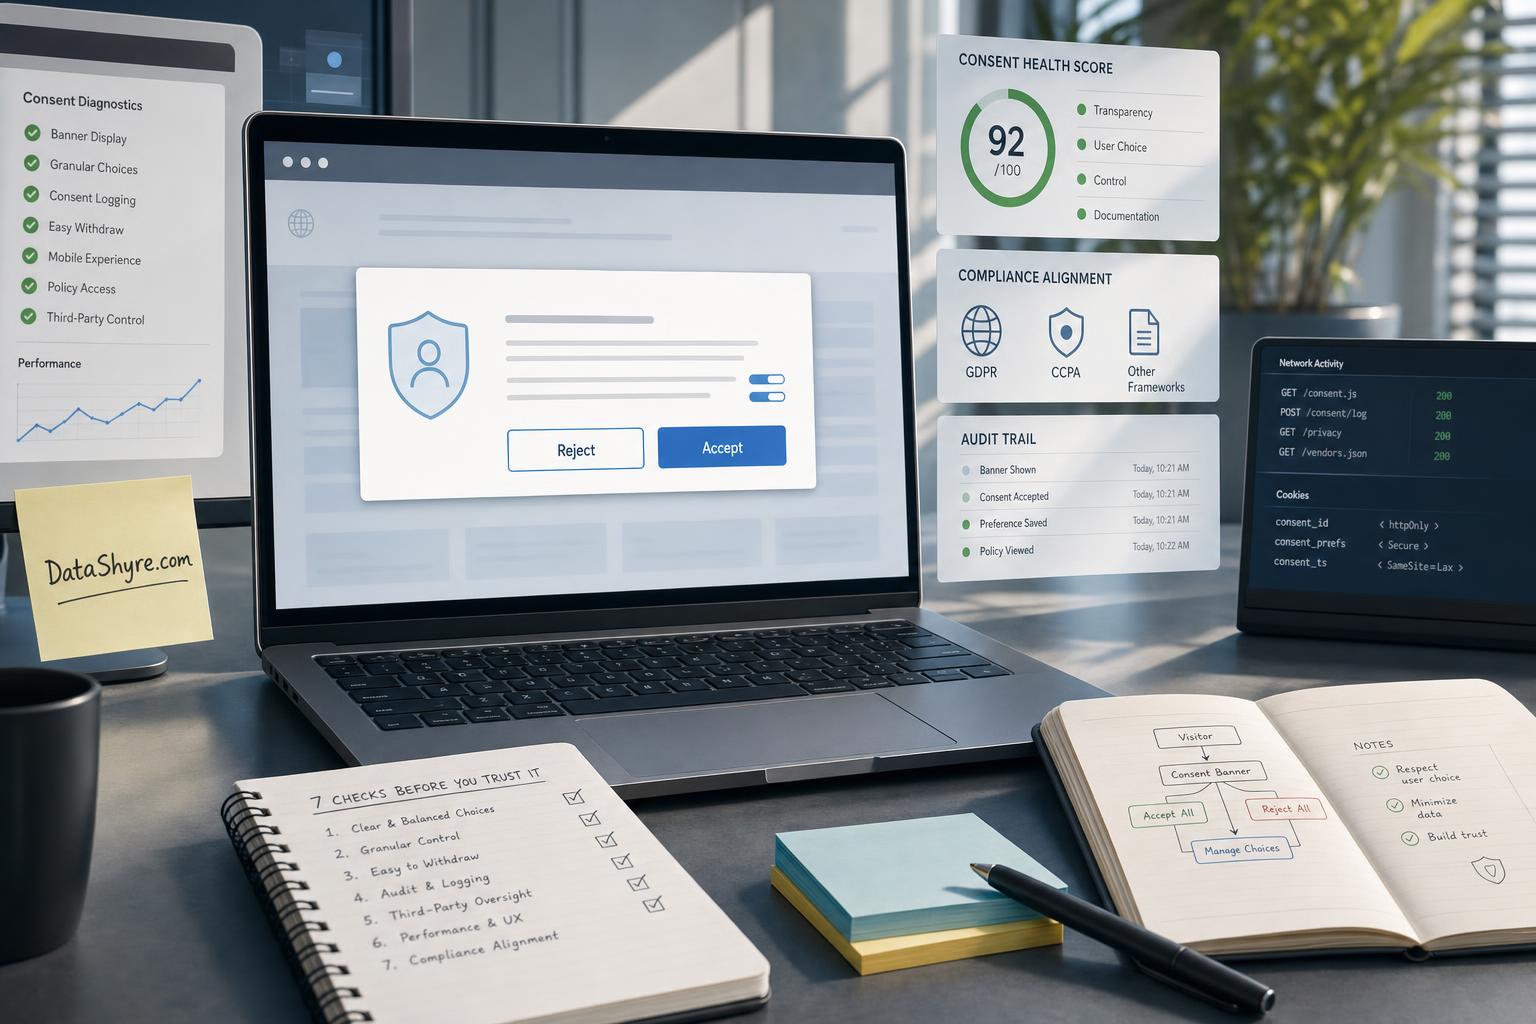
What a consent management system actually has to do
A consent management system should connect four layers that too many teams treat separately:
- the user-facing banner or preference center;
- the policy and purpose model behind that interface;
- the runtime controls that decide what can load or fire; and
- the records that explain what happened later.
That definition matters because a banner alone is not the system. A real consent management system has to make the user choice operational.
1. Start with collection points, not the front end
The first mistake with a consent management system is treating consent like a design problem instead of a data-flow problem.
The European Commission’s current consent guidance still says valid consent has to be freely given, informed, specific, and based on a clear affirmative act. The Commission also says the request should use “clear and plain language.” In the UK, the ICO’s final storage-and-access-technologies guidance, published on April 29, 2026, makes the practical scope wider than classic cookies. It covers scripts, pixels, fingerprinting, and similar storage or access technologies.
So the first review question is simple: can your team name every script, SDK, tag, pixel, embed, and plugin the system is supposed to govern? If not, the banner is already ahead of the actual controls.
2. Check whether the regional logic matches the rule set
Weak consent management system setups often flatten every market into one generic flow.
That is risky because the legal trigger is not identical everywhere. For EU and UK traffic, the operational question often starts with whether non-essential technologies stay off until valid consent exists. In California, the focus may shift toward opt-out rights, sale or sharing logic, and browser signals such as Global Privacy Control. The California Department of Justice still describes GPC as a “stop selling or sharing my data switch.”
A serious consent management system should therefore help you verify that:
- region logic can branch by applicable rule set;
- optional technologies stay off where prior consent is required;
- California opt-out and GPC paths work where they apply; and
- the live behavior matches what the privacy notice says.
One interface can span several regions. One legal theory should not.
3. Map purposes and categories to actual technologies
The middle layer is where a consent management system either becomes useful or becomes decorative.
Categories like analytics, marketing, preferences, and necessary do not enforce themselves. Someone still has to decide which tools belong in each bucket, which purposes they support, and what should happen when the user says yes, no, or changes their mind later.
This is still a live compliance issue. The European Commission’s materials continue to tie consent to specific purposes, and the ICO’s 2026 guidance asks practical questions about whether the same storage or access technology is being used for multiple purposes. If the category labels look neat but the vendor map is muddy, the consent management system is giving false confidence.
Practical test: export the vendor or script inventory and check whether every item has a category, a purpose, a region rule, and a blocked-versus-allowed state your team can explain quickly.
4. Treat runtime enforcement as the real product
This is where many consent management system implementations fail even when the admin interface looks polished.
Google’s current consent mode guidance still says default consent states should be set before any commands that send measurement data. That makes the runtime sequence non-negotiable. Denied defaults have to land before optional analytics or advertising activity begins, not after.
That means the review should cover at least these live states:
- a first visit with no stored choice;
- explicit reject;
- explicit accept;
- later withdrawal or preference change; and
- another page load or route change after each choice.
If the interface says Reject all while the network trace still shows optional requests firing first, the consent management system is not trustworthy yet.
5. Check publisher and Google interoperability separately
Some teams assume a consent management system works just because it can talk to Google tags. That is not enough.
If the site depends on Google advertising products for EEA, UK, or Switzerland traffic, Google’s current publisher guidance still requires a Google-certified CMP integrated with the IAB Transparency and Consent Framework when serving personalized ads in those regions. That is a separate operational check from basic tag blocking.
So if Google monetization is in scope, verify:
- consent mode defaults are set early enough;
- updates propagate after the user acts;
- the publisher stack uses the required CMP path where Google requires it; and
- your ad, analytics, and consent configurations are not drifting in different directions.
A consent management system that passes a tag test can still fail a publisher requirement.
6. Make refusal and withdrawal genuinely easy
This is one of the fastest ways to tell whether a consent management system is real or just cosmetic.
The European Commission still says withdrawing consent should be “as easy to use as giving consent.” CNIL’s current dark-pattern guidance stays aligned with that approach, and the California Privacy Protection Agency has framed the broader design principle cleanly: “Dark patterns aren’t about intent, they’re about effect.”
In practice, test whether:
Reject allis visible when prior consent is the rule;- refusal on mobile is as usable as refusal on desktop;
- users can reopen preferences after the banner closes; and
- the technical state actually changes after withdrawal or opt-out.
If acceptance is immediate but refusal requires extra hunting, the consent management system is creating risk by design.
7. Keep records that reconstruct what actually happened
Consent without proof gets fragile quickly.
A durable consent management system should usually let you reconstruct:
- which interface version was shown;
- which purposes or categories were offered;
- what the user chose and when;
- what technical state that choice produced; and
- whether a later withdrawal, opt-out, or rule change occurred.
That evidence matters because logs and runtime behavior can drift apart. A database value that says rejected is weak proof if the browser trace or vendor console shows optional measurement still running.
A short live review sequence
If I were pressure-testing a consent management system this week, I would work in this order:
- inventory every technology the system claims to control;
- test the region branches separately;
- inspect the purpose map and category assignments;
- verify first-load runtime behavior before any choice;
- test refusal, acceptance, and later withdrawal;
- verify Google and publisher-specific requirements if relevant; and
- compare saved records with what the browser actually did.
That review order usually exposes more truth than another round of banner-copy edits.
Bottom line
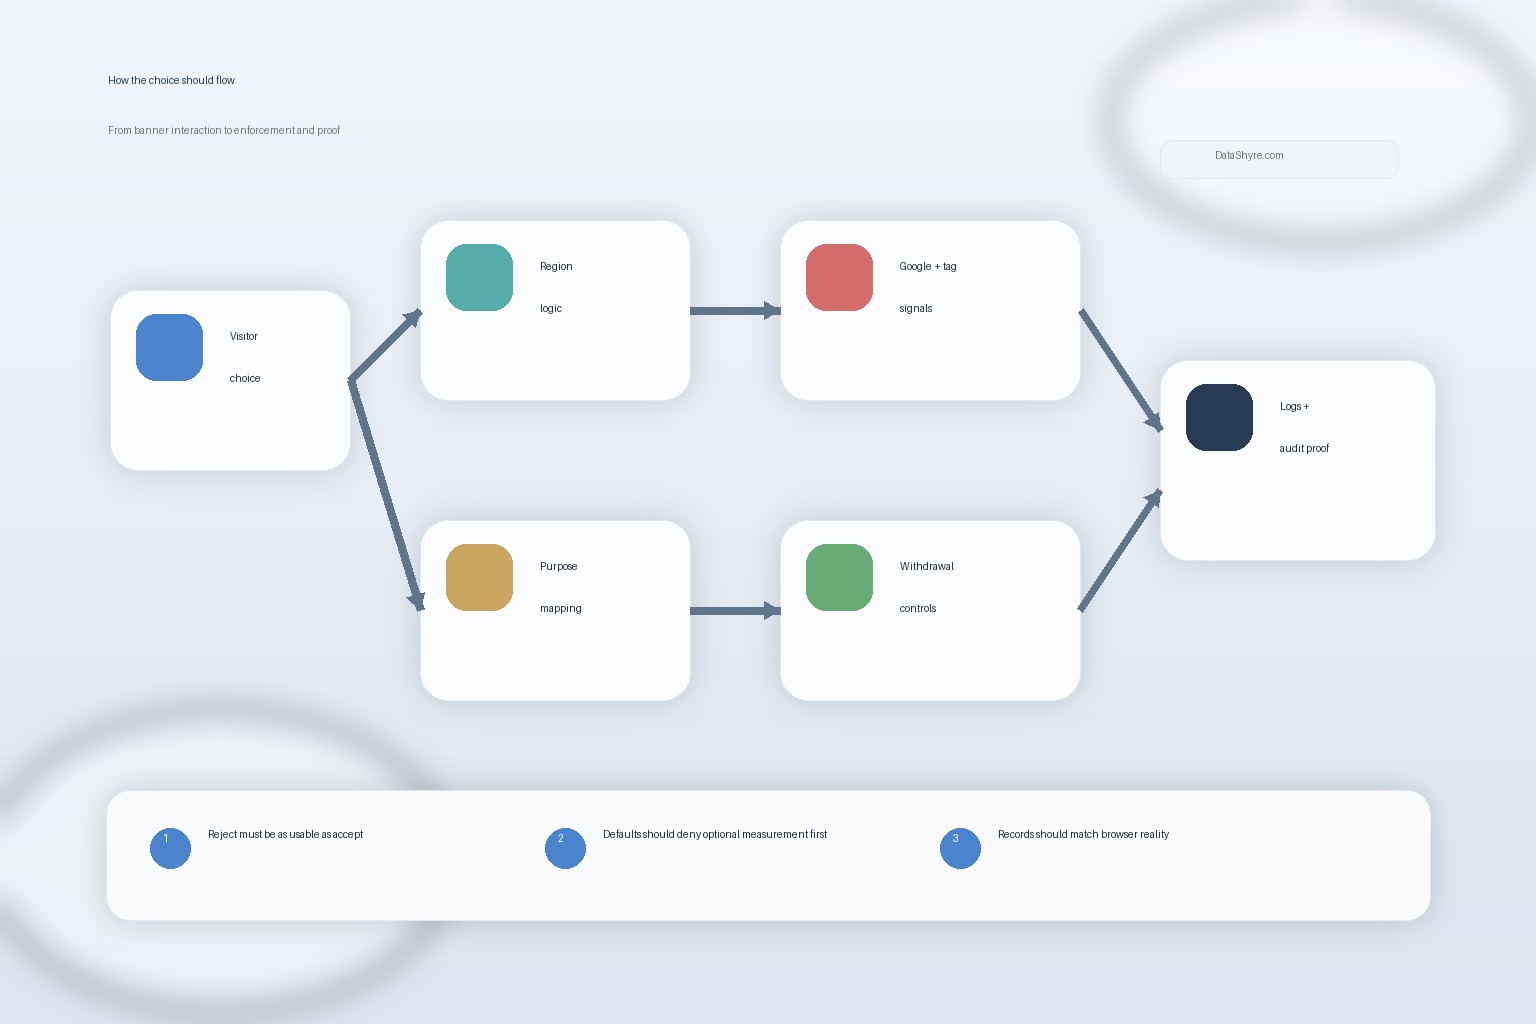
The cleanest way to think about a consent management system in 2026 is this: the product is not the banner. The product is the chain from user choice to technical enforcement to audit proof.
If the system can separate regions honestly, map purposes clearly, block optional activity until the right choice exists, keep withdrawal easy, and leave evidence that still matches live behavior after the next release, it is doing real work. If not, the interface may be finished while the consent management system is not.
Sources
- European Commission, Legal grounds for processing data: https://commission.europa.eu/law/law-topic/data-protection/information-business-and-organisations/legal-grounds-processing-data_en
- European Commission, Information for individuals: https://commission.europa.eu/law/law-topic/data-protection/information-individuals_en
- UK ICO, Final storage and access technologies guidance published: https://ico.org.uk/about-the-ico/media-centre/news-and-blogs/2026/04/final-storage-and-access-technologies-guidance-published/
- UK ICO, Guidance on the use of storage and access technologies: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/
- California Department of Justice, CCPA overview: https://oag.ca.gov/privacy/ccpa
- California Privacy Protection Agency, Enforcement Advisory on Dark Patterns: https://cppa.ca.gov/announcements/2024/20240904.html
- Google for Developers, Set up consent mode on websites: https://developers.google.com/tag-platform/security/guides/consent
- Google AdSense Help, consent management requirements for serving ads in the EEA, the UK, and Switzerland: https://support.google.com/adsense/answer/13554020
- CNIL, Dark Patterns in Cookie Banners: https://www.cnil.fr/en/dark-patterns-cookie-banners-cnil-issues-formal-notice-website-publishers
—
Published: October 18, 2026. Updated using current official European Commission, ICO, California DOJ, CPPA, CNIL, and Google materials available at publication time.