

Google Tag Manager GDPR Cookie Consent in 2026: 7 Live Checks Before EU Tags Fire
If you are searching google tag manager gdpr cookie consent on October 17, 2026, the useful question is not whether the banner looks polished.
The useful question is whether Google Tag Manager actually keeps non-essential analytics, advertising, personalization, and partner tags from firing until valid consent exists, and whether your team can still prove that after the next container publish.
That is still the real issue in the current official material. Google’s consent guide still says “Before a user grants consent” you set the default consent state, and that consent updates should be tracked on the page where they occur before any page transition. Tag Manager help still says the Consent Initialization trigger fires “before all other tags.” The European Commission still says withdrawing consent must be “as easy to use as giving consent.” The ICO’s current guidance says a good consent mechanism makes it “as easy to refuse consent as it is to accept.”
If you want the surrounding context first, start with our guides to Google Tag Manager cookie consent, consent mode, and GA4 consent mode. This article is narrower. It is the seven-check GTM review I would run this week before trusting an EU-facing consent implementation.
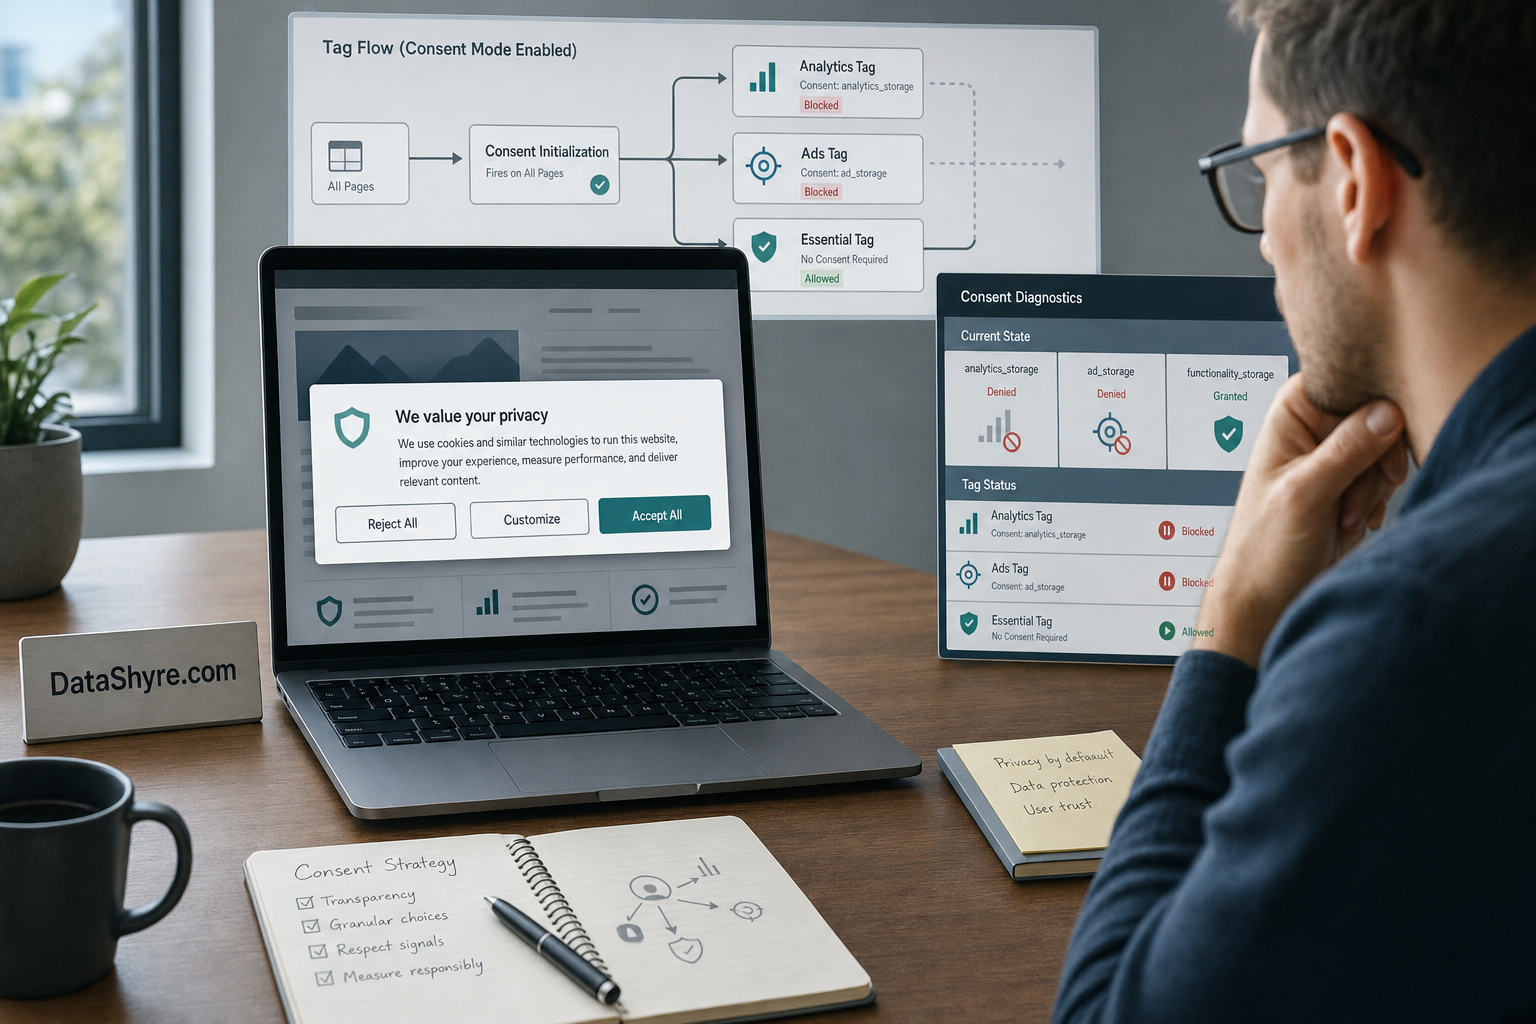
1. Put the consent-writing logic on Consent Initialization
Google Tag Manager’s help documentation still says the Consent Initialization – All Pages trigger is designed to ensure consent settings are honored before any other triggers fire, and that it will run “before all other tags” including Initialization triggers.
That is where the consent-writing logic belongs.
For google tag manager gdpr cookie consent, a weak pattern still looks the same:
- the container loads;
- one or more analytics, ads, or custom tags begin evaluating;
- the CMP or default-consent logic catches up afterward.
That is a race, not a control.
2. Set denied defaults before any optional measurement depends on them
Google’s current consent guide is direct here. “Before a user grants consent” you set the default consent state, and for gtag.js you do it before commands that send measurement data.
This is the live checkpoint that exposes the difference between a clean implementation and a decorative one. If denied defaults arrive late, the setup may still look fine in screenshots because later pageviews behave correctly. The problem is that the first load already escaped the rule.
For a serious google tag manager gdpr cookie consent review, test at least these states in a clean browser:
- first visit with no stored choice;
- explicit reject;
- explicit accept;
- granular selection; and
- later withdrawal followed by a fresh page load.
3. Update consent on the same page where the user acts
Google’s developer documentation still warns that consent updates should be tracked on the page where they occur, before any page transition.
That line matters because many weak GTM builds still behave as if the update can wait until the next navigation. For GDPR-facing flows, that is risky. If a person rejects optional categories, the site should not leave a timing gap where the old state still governs tag behavior.
The safer order is simple:
- defaults are denied where consent is required;
- the user acts in the banner or preference center;
- GTM updates consent immediately; and
- later triggers and later pages inherit the stored choice.
That sequence is much easier to test and defend later.
4. Test reject as seriously as accept
This is where many teams fool themselves.
They click Accept all, see GA4 or Ads wake up, and conclude the job is finished. The more revealing test is the first visit where the user rejects optional categories, then later reopens settings and changes the choice.
The official language is still unusually aligned here. The European Commission says withdrawal must be as easy as giving consent. The ICO says good practice means the mechanism makes it “as easy to refuse consent as it is to accept.” And CNIL’s current formal notices on dark patterns say “Rejecting cookies should be just as easy as accepting them.”
That is not only a design principle. It is a GTM test case.
If rejection is easy in the interface but optional tags still fire, the runtime never delivered the outcome the banner promised.
5. Review Google tags, custom HTML, and third-party vendors separately
One of the quiet failure modes in google tag manager gdpr cookie consent is assuming every tag follows the same rules automatically.
Google tags can use built-in consent checks and GTM consent settings. Custom HTML cannot be trusted that easily. Third-party pixels and embeds may need their own blocking, their own trigger logic, or CMP-level script control.
A useful live review splits the stack into three branches:
- Google tags using built-in consent behavior;
- Custom HTML or template code that may bypass timing or consent APIs; and
- non-Google vendors that still need separate blocking and release testing.
This matters even more after Google’s June 15, 2026 Analytics data-controls update. Google’s current help says that for linked properties, Consent Mode settings within Google Ads become the single control for Google Ads data flowing from Analytics, while Google Signals in Analytics narrows to signed-in-user association for behavioral reporting. If the consent chain is wrong, you are not only creating a compliance problem. You are also changing what reaches Ads.
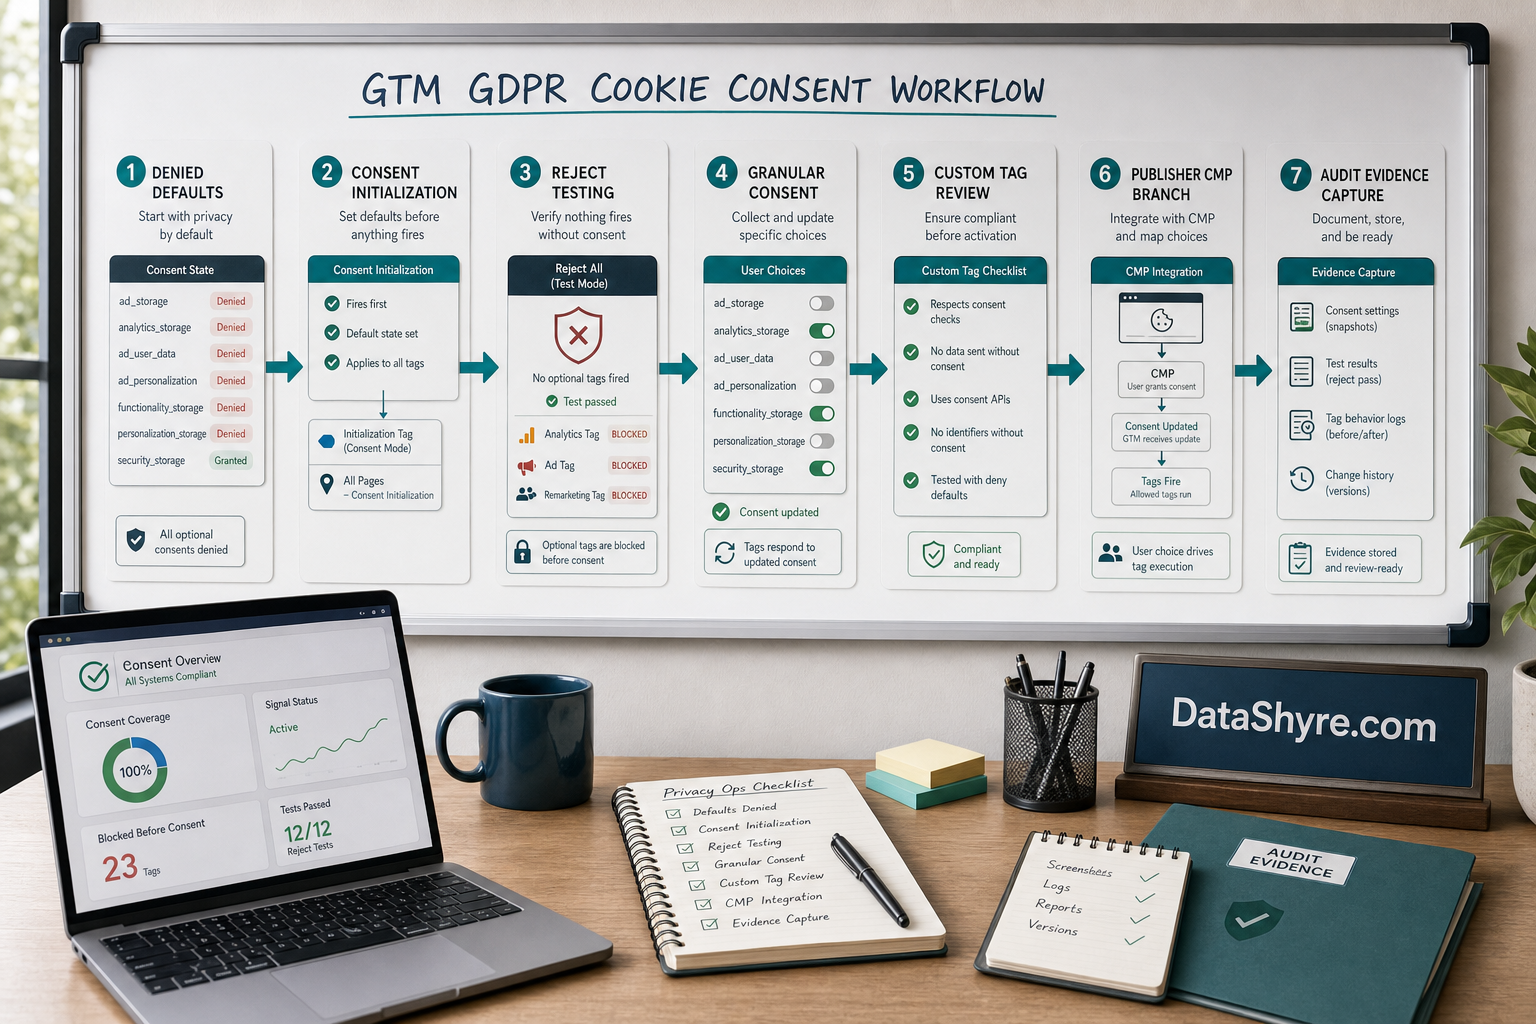
6. Keep publisher-ad requirements separate from the baseline GDPR check
If you serve publisher ads, there is an extra branch that should not be confused with general GDPR consent hygiene.
Google’s current publisher help still says AdSense, Ad Manager, and AdMob partners serving personalized ads in the EEA and UK must use a Google-certified CMP integrated with the IAB Transparency and Consent Framework as of January 16, 2024, and that the same requirement applies in Switzerland as of July 31, 2024. The same page also says Google does not check CMPs for full compliance with applicable privacy laws.
That distinction matters.
A stack can satisfy Google’s publisher requirement and still be weak on first-layer fairness, denied defaults, or later withdrawal. The reverse can also happen.
So for google tag manager gdpr cookie consent, ask two separate questions when ads matter:
- does the site meet the prior-consent and fairness rules that apply to optional tracking in the relevant EU-facing flow; and
- does the publisher branch also satisfy Google’s certified-CMP and TCF requirement where it applies.
7. Save proof and retest after every change
The last check is operational.
The ICO’s 2026 storage-and-access guidance makes clear that the review surface is broader than classic cookies. That is exactly why google tag manager gdpr cookie consent should be treated as release work, not as a one-time banner project.
A defensible evidence pack should let your team reconstruct:
- what default consent state loaded first;
- what changed after reject, accept, or granular choice;
- which tags were blocked before consent;
- which tags changed behavior after consent;
- what the user-facing banner or preference center looked like; and
- what changed after the latest GTM, CMP, or vendor release.
Without that proof, the implementation becomes harder to defend the moment the container changes.
A short go-live audit sequence
Before you trust a google tag manager gdpr cookie consent setup in production, run this sequence:
- open the site in a clean browser session;
- confirm the earliest consent event sets denied defaults before optional tags evaluate;
- verify the consent-writing logic runs on Consent Initialization;
- click
Reject alland confirm optional tags remain blocked; - reopen settings, grant one optional category, and confirm only the expected behavior changes;
- inspect custom HTML and third-party paths separately; and
- save enough evidence that engineering, legal, or support can reconstruct the result later.
That short audit usually reveals more than another round of banner-copy revisions.
Bottom line
Google tag manager gdpr cookie consent in 2026 is not mainly a banner-copy task. It is an execution-order and proof task.
If defaults land first, updates happen immediately, rejection is technically equal to acceptance, custom and third-party tags stay inside the same control model, and the evidence is easy to reproduce later, the setup is in much better shape. If any of those pieces are vague, the banner may look compliant while the live site tells a different story.
Sources
- Google for Developers: Set up consent mode on websites
- Google Tag Manager Help: Tag Manager consent mode support
- Google Analytics Help: Updates to Google Analytics Data Controls
- Google AdSense Help: Google consent management requirements for serving ads in the EEA, the UK, and Switzerland (for publishers)
- European Commission: Legal grounds for processing data
- ICO: How do we manage consent in practice?
- ICO: Cookies and similar technologies
- CNIL: Dark Patterns in Cookie Banners: CNIL issues formal notice to website publishers
—
Published: October 17, 2026. Updated using current official Google, European Commission, ICO, and CNIL materials available at publication time.