

Cookie Consent WordPress in 2026: Plugin, Tag, and Theme Checks Before You Publish
If you are searching cookie consent wordpress in 2026, the real question is not which banner looks best. It is whether your WordPress site can keep optional tracking off until it should run, pass user choices into tags and plugins correctly, and stay trustworthy after the next theme change, cache tweak, or marketing install.
That is why this topic matters now. The UK ICO’s final storage-and-access technologies guidance, published on April 29, 2026, makes clear that the rules extend beyond classic cookies to pixels, scripts, device fingerprinting, and similar technologies. WordPress’s own developer guidance pushes in the same direction: privacy should be built into the default behavior, not added as a cosmetic layer after launch.
If you want the surrounding context first, start with our guides to WordPress cookie consent, cookie consent Google Tag Manager, and website privacy checker. This article stays focused on the live-site review I would use before trusting cookie consent wordpress on a production build.
What cookie consent wordpress has to control
The hard part about cookie consent wordpress is that consent rarely lives in one place.
The banner may come from one plugin, but the real behavior may be triggered by:
- theme code;
- tag manager containers;
- analytics and ad scripts;
- embeds from video, maps, chat, or forms;
- plugin telemetry or third-party API calls;
- caching or optimization tools that change load order; and
- later preference changes that need to take effect immediately.
That is why a banner review alone is not enough. You need a runtime review.
1. Start with an inventory, not a settings screen
WordPress’s Privacy section in the Plugin Handbook says “Privacy should be the default setting.” The same guidance asks plugin authors to think through whether a plugin loads third-party JavaScript, tracking pixels, iframes, cookies, or local storage, and whether it shares personal data with outside services.
That turns cookie consent wordpress into an inventory problem before it becomes a UX problem.
The useful first question is not “Which CMP plugin did we buy?” It is “Which plugins, scripts, embeds, and external services can store or access data before the visitor makes a choice?”
If your team cannot answer that quickly, the banner is not the main risk. Unknown behavior is.
2. Treat plugin behavior before consent as a first-class risk
This is one of the most practical WordPress-specific checks.
WordPress’s Detailed Plugin Guidelines say plugins may not contact external servers without “explicit and authorized consent.” That matters because many real WordPress sites depend on plugins that initialize remote assets, analytics helpers, chat services, font or CDN resources, marketing widgets, or embedded content earlier than site owners expect.
For cookie consent wordpress, that means you should inspect what each plugin does before the visitor interacts with the banner.
If a plugin vendor says the product is privacy-friendly, verify it in the browser. Look for network requests, storage writes, injected scripts, and iframe loads on first render. Do not assume the settings page tells the full story.
3. Make refusal genuinely as easy as acceptance
This is still one of the fastest ways to spot a weak setup.
The European Commission’s consent guidance still says withdrawing consent should be as easy as giving it. CNIL’s cookie-banner enforcement materials continue to stress that rejection should not be obscured by design. And in the ICO’s April 29, 2026 announcement, William Malcolm said people should have “meaningful control over how their data is used.”
In practice, cookie consent wordpress usually fails here when:
Reject allis hidden behind an extra click;- the refusal path is low-contrast or vague on mobile;
- the banner lets users accept immediately but makes later changes awkward; or
- category toggles start from permissive defaults where prior consent should come first.
The banner can be attractive and still be unfair.
4. Check Google timing, not just Google marketing copy
Many WordPress consent installs break at the timing layer.
Google’s current consent-mode setup guide says default consent states should be set before any measurement data is sent, and consent updates should be tracked on the same page where the visitor acts, before a page transition. On WordPress, those expectations can drift when GTM loads earlier than expected, a theme injects scripts directly, or a performance plugin changes execution order.
That makes cookie consent wordpress a timing problem as much as a policy problem.
Test whether:
- consent defaults are set early enough;
- tags actually stay blocked when they should;
- updates propagate after accept or reject;
- later page views keep the same state; and
- embeds or plugins bypass the CMP logic.
If the tag platform sees permission earlier than the user gave it, the setup is not ready.
5. Separate EU and UK prior-consent logic from California opt-out logic
Global WordPress sites often flatten everything into one banner flow. That is where the legal logic usually gets sloppy.
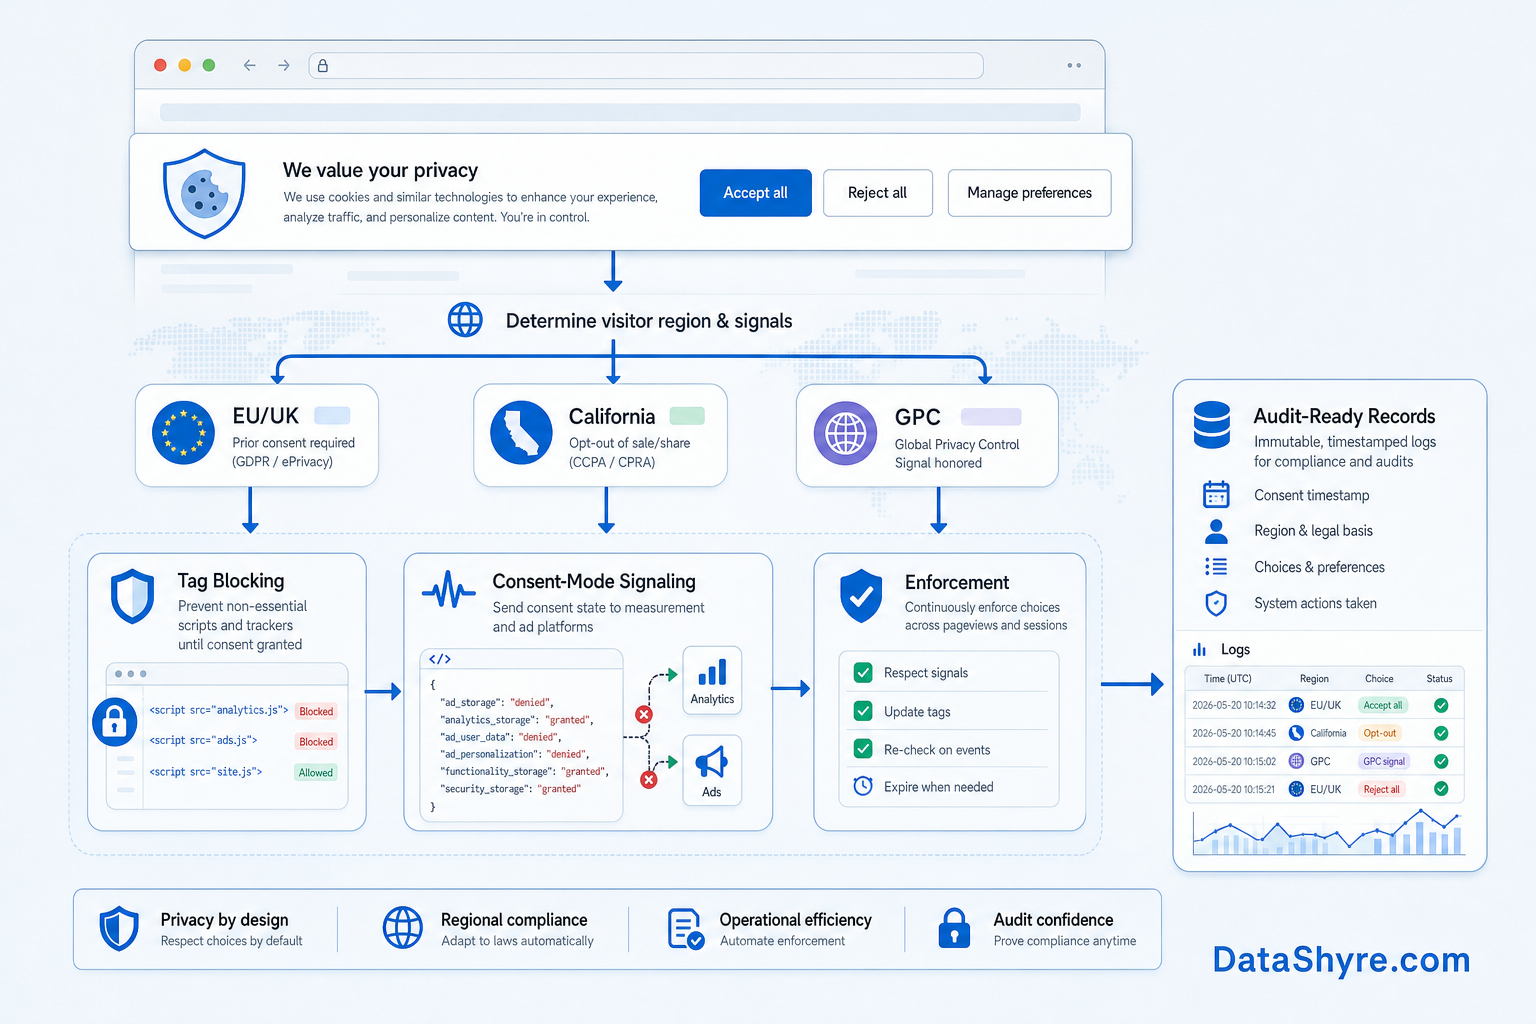
For EU and UK traffic, the practical review often centers on whether optional technologies stay off until valid consent exists. For California, the workflow can shift toward opt-out rights and whether sale or sharing stops when a valid request or signal arrives.
The California DOJ’s current CCPA materials say consumers may opt out of the sale or sharing of personal information, including through Global Privacy Control. The same DOJ guidance describes GPC as a “stop selling or sharing my data switch.”
So a serious cookie consent wordpress review tests both branches on purpose:
- prior-consent behavior for optional technologies where it applies; and
- opt-out and GPC handling where California rules are the relevant branch.
One front-end pattern does not automatically solve both.
6. Re-test after plugin, theme, and cache changes
This is the step that keeps an apparently good setup from quietly drifting.
WordPress sites change constantly. A new plugin is added. A theme update moves scripts. A cache or optimization tool rewrites execution order. Marketing drops a new embed into a page builder. The banner may look identical while the tracking behavior underneath it changes.
That is why cookie consent wordpress should be handled as a repeatable release check tied to:
- plugin additions or updates;
- theme or page-builder changes;
- caching and optimization changes;
- new embeds, forms, or chat widgets;
- analytics or advertising changes; and
- recurring QA on desktop and mobile.
A short review sequence before you publish
If I were reviewing cookie consent wordpress today, I would use this order:
- List every plugin, script, embed, and service that can store or access data.
- Inspect first-page load on the homepage and at least one template with third-party embeds.
- Verify that refusal is as visible and easy as acceptance.
- Confirm Google consent states are set early and updated correctly after the user’s action.
- Test whether plugins, remote assets, and embeds actually obey the chosen state.
- Run a California branch with GPC enabled if sale or sharing could be relevant.
- Repeat the same checks after any plugin, theme, or cache change.
That sequence will tell you more than a plugin feature comparison page.
Bottom line
The right way to think about cookie consent wordpress in 2026 is not as a banner choice. It is as a control problem.
If your WordPress stack can inventory what needs governance, keep refusal genuinely usable, hold optional tools back until the right moment, respect California opt-out signals where relevant, and survive ordinary site changes without breaking consent behavior, you are in much better shape. If it cannot do those things, the interface may be finished while the consent system is not.
Sources
- WordPress Plugin Handbook, Privacy: https://developer.wordpress.org/plugins/privacy/
- WordPress Plugin Handbook, Suggesting text for the site privacy policy: https://developer.wordpress.org/plugins/privacy/suggesting-text-for-the-site-privacy-policy/
- WordPress Detailed Plugin Guidelines: https://developer.wordpress.org/plugins/wordpress-org/detailed-plugin-guidelines/
- UK ICO, final storage and access technologies guidance announcement: https://ico.org.uk/about-the-ico/media-centre/news-and-blogs/2026/04/final-storage-and-access-technologies-guidance-published/
- UK ICO guidance on the use of storage and access technologies: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/
- European Commission legal grounds for processing data: https://commission.europa.eu/law/law-topic/data-protection/information-business-and-organisations/legal-grounds-processing-data_en
- California DOJ, CCPA overview: https://oag.ca.gov/privacy/ccpa
- California DOJ, Global Privacy Control: https://oag.ca.gov/privacy/ccpa/gpc
- Google for Developers, consent mode setup guidance: https://developers.google.com/tag-platform/security/guides/consent
- CNIL, dark patterns in cookie banners formal notice: https://cnil.fr/en/dark-patterns-cookie-banners-cnil-issues-formal-notice-website-publishers
—
Updated on October 8, 2026 using current official WordPress developer, regulator, government, and platform materials available at publication time.