

Consent Manager in 2026: 7 Runtime Checks Before You Trust One
If you are evaluating a consent manager on September 25, 2026, the useful question is not whether the banner looks polished in a demo.
It is whether the live system creates a fair choice, blocks optional technologies until it should not, sends the right signals to Google and non-Google tools, handles California opt-out flows properly, and leaves behind records your team can still use after the next release.
That is the standard current guidance points toward. Google says consent mode “doesn’t provide a consent banner or widget.” The ICO says consent mechanisms must “function as intended” and let users withdraw consent with the same ease they gave it. CNIL still uses one of the clearest interface tests available: “rejecting cookies should be just as easy as accepting them.” And California’s Department of Justice still describes Global Privacy Control as a “stop selling or sharing my data switch.”
If you want nearby context first, start with our guides to consent management platform, GTM consent mode, and cookie consent banner examples. This article is narrower. It is the seven-check runtime review I would use before trusting a consent manager this week.
What a consent manager has to prove now
A real consent manager is not just a first-layer banner.
It is the operating layer between user choice and everything else your stack does with that choice.
In practice, that means it has to coordinate:
- a first layer that offers a real choice;
- purpose-level controls;
- prior blocking where consent is required;
- runtime signals into tags, analytics, advertising tools, and embeds;
- regional differences, especially between EU or UK consent flows and California opt-out flows;
- records that explain what happened later.
If the product mainly changes colors, wording, and layouts, it is handling the easiest part of the problem.
1. Check whether the first layer offers a fair refusal path
This is still the fastest way to eliminate weak options.
The ICO’s live storage-and-access guidance says consent requests generally need granular options and that any consent mechanism must respect the choices made through it. CNIL’s December 12, 2024 formal-notice announcement remains useful because it is so direct: “rejecting cookies should be just as easy as accepting them.”
So the first review is not abstract. Compare Accept all and Reject all on desktop and mobile. If refusal is pushed into another layer, visually downgraded, or made slower than acceptance, the consent manager is creating risk before you even inspect technical behavior.
2. Check prior blocking on a clean session
This is where many consent manager demos still fail.
The ICO says that if no exception applies, you must obtain prior consent for storage and access technologies in scope. On the platform side, Google’s current consent-mode setup guidance still says to set a default consent state before user interaction and to update the state on the page where the interaction happens.
So on a clean visit, test three things:
- whether analytics or advertising tags act before any user choice;
- whether embeds, chat tools, or A/B testing scripts set identifiers too early;
- whether the tag layer really receives the denied-by-default state you intended.
If optional technologies are already active before the user acts, the consent manager is mostly a decorative interface.
3. Check whether the signal reaches the real stack in time
A consent manager only matters if other systems hear it in time.
Google’s current help materials are useful here because they make two points that teams still blur together:
- consent mode can work in basic or advanced mode;
- Google tags already contain built-in consent checks for several core products.
That means your review should not stop at the banner. Trace what happens in:
- Google Tag Manager;
- Google Analytics and Google Ads tags;
- non-Google analytics, chat, video, and personalization tools;
- later updates after a user changes preferences.
If your consent manager depends on late callbacks, duplicated trigger logic, or undocumented custom workarounds, it can look healthy in the admin UI and still behave inconsistently on the page.
4. Separate EU or UK consent logic from California opt-out logic
This is one of the most expensive category mistakes.
For much of the EU and UK, the question is whether optional storage and access stay off until valid consent exists. For California, the practical question often becomes whether sale-or-sharing opt-out rights and browser preference signals are recognized and applied correctly.
California’s DOJ still says GPC is a “stop selling or sharing my data switch” and that covered businesses must honor it as a valid request to stop the sale or sharing of personal information. Then on February 27, 2026, the California Privacy Protection Agency Board issued its Ford decision requiring a $375,703 fine and practice changes, emphasizing that unnecessary friction in the opt-out process violates the CCPA.
That makes this a product review issue, not only a legal issue. A serious consent manager should support both prior-consent logic and low-friction California opt-out handling without flattening them into one vague global banner flow.
5. Treat Google advertising and publishing requirements as a separate branch
Not every buyer needs the same Google checks, but many do.
Google’s current publisher guidance says partners using AdSense, Ad Manager, or AdMob must use a Google-certified CMP integrated with the IAB Transparency and Consent Framework when serving personalized ads in the EEA and UK as of January 16, 2024, and in Switzerland as of July 31, 2024. The same page also says Google does not check CMPs for full compliance with the TCF or applicable privacy laws.
That distinction matters. A consent manager can satisfy a Google publisher-program requirement and still be weak in first-layer fairness, records, or runtime enforcement. The reverse can also happen.
So I would split this review into two questions:
- does the product satisfy the specific Google monetization requirement where it applies;
- does it also satisfy your broader privacy and operational requirements.
Those are related checks, not the same check.
6. Check whether withdrawal and records are actually usable
Collection is only half of the job.
The ICO says users must be able to withdraw consent with the same ease they gave it. It also says you need to be able to demonstrate consent and keep records of user preferences appropriately.
For a buyer, that means a consent manager should be able to explain:
- what the person saw;
- which purposes or third parties were disclosed;
- what they selected, and when;
- whether the technical behavior changed after that choice;
- what happened when they later withdrew or updated preferences.
If legal, support, engineering, and marketing cannot reconstruct the story later, the evidence layer is too weak.
7. Check how the platform handles drift after launch
This is where stronger consent managers separate themselves from prettier ones.
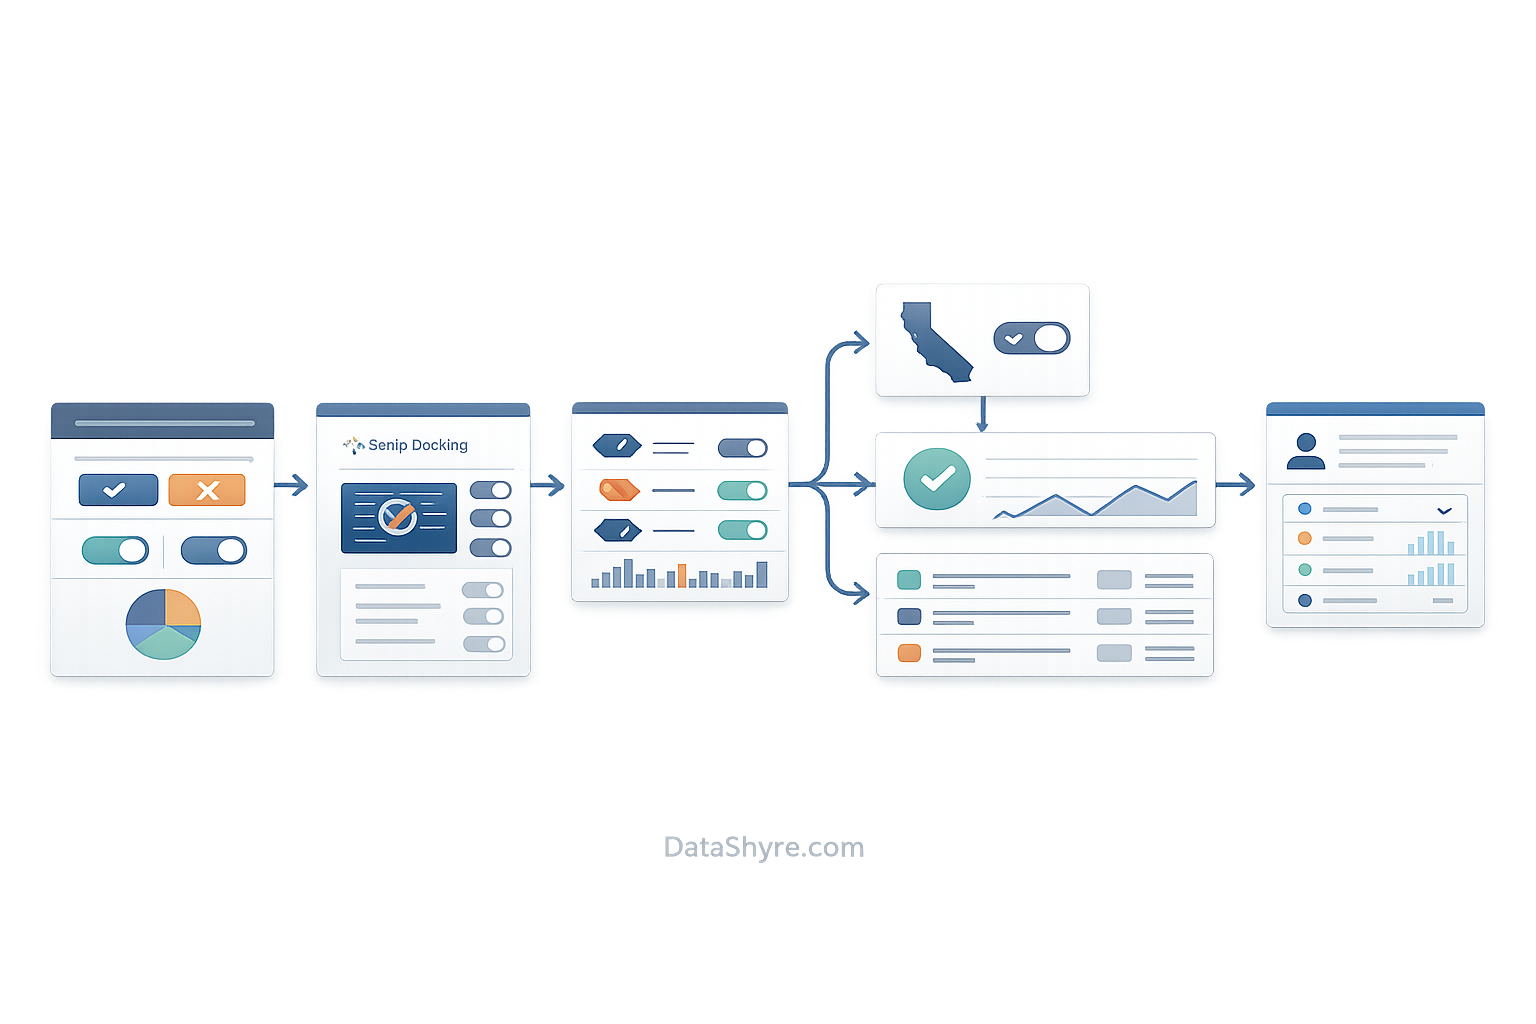
The ICO’s current guidance is explicit that if you introduce new storage or access technologies for a different purpose, you must obtain fresh consent for that new technology or purpose. That means a consent manager should help your team notice when the live site has drifted away from the declared consent model.
In practice, I would want to know whether the platform helps you:
- rescan the site after releases;
- notice new vendors or tags;
- remap purposes when tooling changes;
- prove that a new embed did not silently bypass the current rules.
Without that, you are not really buying a durable control. You are buying a launch-day screenshot.
A short review sequence for this week
If I were reviewing a consent manager today, I would do this in order:
- compare
Reject allfriction withAccept all; - run a clean session and watch what fires before any click;
- test one granular path and one later withdrawal path;
- test the California branch, including GPC handling, if it applies;
- trace the signal into GTM, Google tags, and non-Google tools;
- verify whether Google publisher requirements matter separately;
- export the records and decide whether a non-technical stakeholder could actually use them.
That sequence usually reveals more than another vendor feature matrix.
Bottom line
The right consent manager in 2026 is not the one with the smoothest demo.
It is the one that creates a fair refusal path, keeps optional technologies aligned with the user’s choice, handles California and publisher branches deliberately, and leaves behind proof your team can still trust after the stack changes.
If those pieces are weak, the interface polish will not save the rollout.
Sources
- Google Tag Manager Help: About consent mode
- Google for Developers: Set up consent mode on websites
- ICO: How do we manage consent in practice?
- CNIL: Dark Patterns in Cookie Banners: CNIL issues formal notice to website publishers
- California DOJ: Global Privacy Control (GPC)
- California Privacy Protection Agency: Ford Motor Company board decision
- Google AdSense Help: Google consent management requirements for serving ads in the EEA, the UK, and Switzerland (for publishers)
—
Published: September 25, 2026. Updated using current official regulator, government, and platform materials available at publication time.