

What Is User Consent in 2026? Definition, Requirements, and Practical Tests
Published Keyword: user consent
Executive Summary
User consent in 2026 remains the legal cornerstone of privacy compliance, yet it continues to evolve under mounting regulatory pressure and technological change. GDPR consolidated the “freely, specific, informed, and unambiguous” standard from 2018, and the Digital Omnibus now projects a massive shift in 2026 by removing consent requirements for low-risk data processing. Meanwhile, U.S. states now mandate recognition of universal opt-out signals like Global Privacy Control (GPC) and require opt-in for sensitive data across more than 20 frameworks.
In 2026, successful user consent means building systems that can simultaneously handle both GDPR’s granular opt-in stack and the new consent-light options under the Digital Omnibus, while also respecting GPC in the U.S. and newer opt-in regimes for children, sensitive data, and automated decisions.
This guide provides the latest 2026 regulatory landscape, practical tests for your consent stack, and a roadmap to adapt to the world’s split-user-consent reality.
Why User Consent Matters More Than Ever in 2026
| Driver | Impact on User Consent | |——–|————————| | EU Digital Omnibus (Q3 2026) | Removes consent for low-risk processing (≈60% of cookies) but mandates single-click acceptance/rejection and equal prominence of “Reject All” across the EU. | | GDPR Enforcement Focus | €3.5M CNIL fine (Jan 2026) — leading to stricter scrutiny of consent documentation, granular opt-ins, and withdrawal ease. | | 20+ U.S. State Laws | Most are now opt-out, but still require opt-in for sensitive personal information and for children under 16; all now require GPC recognition. | | Cookie Walls Illegal | GDPR mandates that refusing non-essential cookies cannot block essential service access; many state privacy acts prohibit dark patterns that coerce consent. | | AI Data Collection Expansion | New EU AI regulations (early 2026) and state laws require explicit consent for training data and profiling of minors under 16. | | Privacy-by-Design Pressure | Regulators expect continuous consent hygiene — logging, versioning, and auditability for every consent event. | | Children’s Privacy | CPRA, Colorado, Utah and others now require opt-in consent from a parent/guardian for children under 13 or a verified guardian for children under 16. |
Key takeaway: Consent in 2026 is not just about the banner; it’s an operational system that supports dynamic, granular, and auditable consent records across regional models (opt-in vs. opt-out) and legal triggers (age, data sensitivity, use case).
1. Core User Consent Definitions and Legal Basis
Valid User Consent (2026 Standard)
GDPR Article 4(11) and 7 anchor consent with four bedrock requirements that are increasingly enforced:
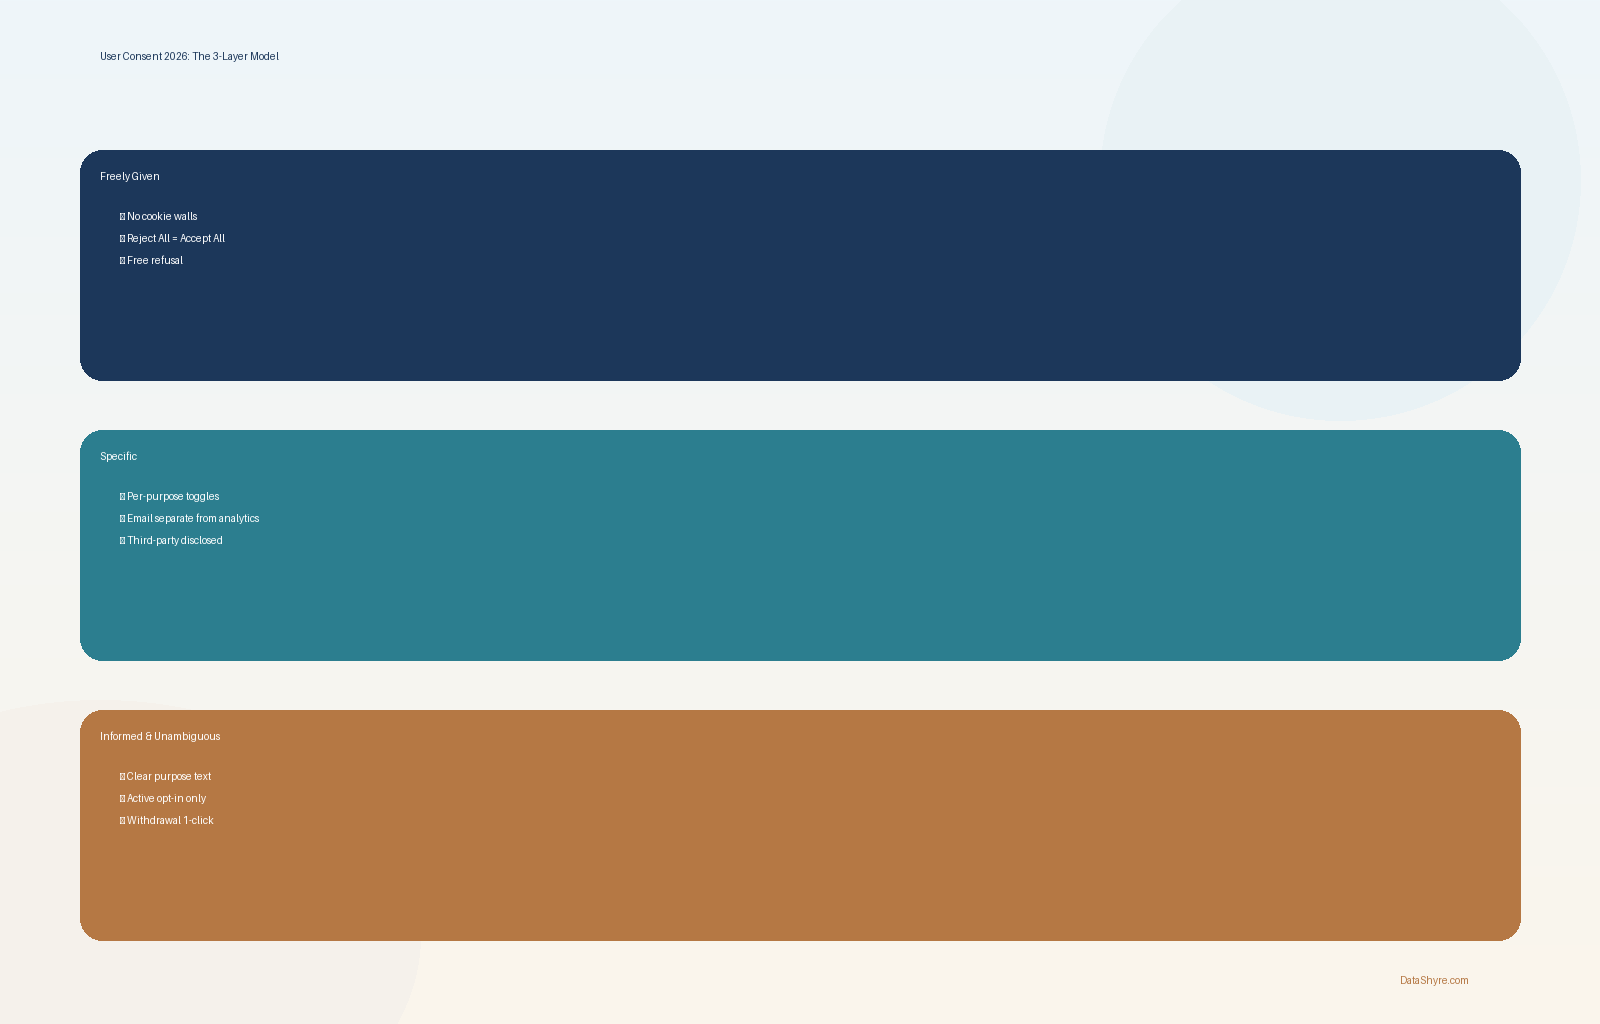
| Requirement | Practical 2026 Test | Common Failure Mode | |————-|———————|——————–| | Freely Given | User can refuse without penalty; banner shows “Reject All” equal to “Accept All”; refusal does not block essential service | Bundle consent with terms; “cookie wall” blocking site access | | Specific | Separate toggles for: Analytics, Marketing, Third-party sharing, Profiling, Automated decisions | Single “I agree to everything” checkbox | | Informed | Link to clear purpose language, data retention, third-party disclosure, withdrawal method | Vague “we use cookies” without purpose list | | Unambiguous | Active checkbox (pre-ticked = invalid), clear label: “Accept necessary and optional cookies” | Default privacy settings are too permissive; pre-checked boxes; inactivity counts |
GDPR Consent Documentation Requirements:
- Timestamp, hashed identifier, consent text version
- Channel-specific consent (email vs. SMS vs. cookies) with toggle records
- IP/geolocation validation (EEA/UK flags)
- TCF 2.3 string + CMP vendor record
- Withdrawal timestamp with audit log
U.S. State Consent Models (as of Jan 2026)
| State | Model | Opt-In Triggers | Universal Opt-Out Required | |——-|——-|—————-|—————————| | California (CCPA/CPRA) | Opt-out | Sensitive data, children under 16 | GPC mandatory | | Colorado, Utah, Oregon | Opt-out | Sensitive data, children under 16 | GPC mandatory | | Virginia, Connecticut | Opt-out | Sensitive data, children under 16 | GPC mandatory | | Illinois (BIPA) | Opt-in | Biometric data | None | | New York (SHIELD) | Hybrid | All personal data of children | None |
Key takeaway: User consent in 2026 must support both opt-in (GDPR, Illinois) and opt-out (California, Colorado) models, plus GPC recognition everywhere.
2. How User Consent Must Work Across the New EU Digital Omnibus
What’s Changing in Q3 2026?
The EU Digital Omnibus proposes to liberalize user consent by classifying low-risk purposes as “non-personal” or “low-risk data processing” that don’t need explicit consent:
| Low-Risk Purpose | Consent Needed in 2026? | User Control Required | |—————–|————————|———————| | Website analytics (traffic data) | No (1–2) | None needed | | Audience measurement (unique visitors) | No (1–2) | None needed | | Electronic communications (sending emails) | No (1–2) | None needed | | Security/fraud prevention | No (1–2) | None needed | | Marketing cookies | Yes | Granular opt-in per channel | | Analytics cookies | Yes (if custom data) | Opt-in for custom tracking | | Profiling/personalization | Yes | Explicit opt-in |
New User Consent UX Requirements (EU-wide)
- Single-Click Acceptance/Rejection: One click on “Accept All” or “Reject All” must apply across all non-essential categories.
- Equal Visual Weight: “Reject All” button must be same size, color contrast, and position as “Accept All”.
- 7-Day Refusal Storage: If user rejects consent, the system must remember their choice for at least 7 calendar days, even if they revisit the site.
- Granular Override: Users must be able to access a “Preference Center” where they can toggle any specific category back on (like marketing for a specific email list).
- No Cookie Walls: Refusing non-essential cookies cannot block access to essential site content or functionality.
- Transparent Withdrawal: A visible link to withdraw consent must appear on every page, close to any active consent item (like marketing toggle).
Implementation tip: New EU-consent-aware CMPs usually use a “default deny” model for non-consented categories, then activate tags only after explicit opt-in.
3. U.S. State Consent Requirements for User Consent
Sensitive Personal Information (SPI) Opt-In Triggers (Most States)
| Data Type | Opt-in Required? | Consent Text Requirement (2026 Standard) | |———–|—————–|——————————————| | Precise geolocation (lat/long) | Yes | Explain that sharing exact location enables location-based offers and remarketing. | | Racial/ethnic origin | Yes | Specify purposes: demographic analysis, compliance reports, and internal diversity initiatives. | | Health/conditions data | Yes | Disclose marketing use, third-party sharing, and right to delete health records. | | Genetic/biometric data | Yes | Include notice about automated decision-making for security and profiling. | | Sexual orientation | Yes | Explain that data informs personalized content and ad targeting. | | Children’s data (<16) | Yes | Parent/guardian consent notice with contact info; include data minimization statement. |
Universal Opt-Out Recognition (GPC)
At least 11 U.S. states now require businesses to honor GPC signals:
| State | GPC Law Effective | Enforcement Mechanism | |——-|——————-|———————-| | California | CCPA/CPRA (2020) | Consumer complaints to CAAG | | Colorado | CPA (2021) | Attorney General enforcement | | Connecticut | CT DPA (2021) | Consumer lawsuits & AG action | | Utah | UTPA (2021) | Attorney General audits | | Oregon | OCPA (2021) | Consumer rights enforcement | | Virginia | VCDPA (2021) | AG enforcement + private right | | Nevada | NVCPA (2020) | AG enforcement | | Maryland | MD DPA (2021) | Consumer lawsuits | | New Jersey | NJ DPA (2021) | AG enforcement | | Washington | CW DPA (2020) | AG enforcement | | Delaware | DE DPA (2021) | AG enforcement |
What GPC Does: When a user sends a GPC signal (browser header Sec-GPC: true), the site must:
- Treat it as a request to opt-out of the sale or sharing of personal data
- Honor that opt-out for 24 months (configurable, but minimum)
- Provide a clear GPC-powered banner that confirms the setting
- Respect the signal even across subdomains and sub-segments
Common failure: Business forgot to read GPC header when processing requests, treating it as a regular visit without the universal opt-out preference.
4. Consent for Children Under 16 (Global 2026 Reality)
EU Children’s Consent (General Data Protection Regulation)
GDPR Art. 8(1) applies for children under 16 (or higher age set by member state): parental or guardian consent required for processing personal data.
What Parent/Guardian Consent Must Include:
- Identity verification (email + government ID, or trusted digital wallet)
- Clear statement of what data will be collected, processed, and stored
- Specific purposes: educational content, safety features, or data minimization for service delivery
- Right to withdraw at any time (including deletion of data)
- Contact info for privacy questions and complaints
U.S. State Children’s Consent (Effective Jan 1, 2026)
| State | Age Threshold | Consent Required From | Implementation Deadline | |——-|—————|———————–|————————| | California | <16 | Parent/guardian | CPRA amendment effective | | Colorado | <16 | Parent/guardian | CPA amendment effective | | Utah | <18 | Parent/guardian | UTPA amendment effective | | Oregon | <13 | Parent/guardian | OCPA amendment effective | | Virginia | <13 | Parent/guardian | VCDPA amendment effective |
What Parent/Guardian Consent Must Include:
- Purpose limitation (only what’s necessary for children’s service)
- Data minimization (no marketing data collection)
- Separate consent for location tracking
- Right to delete all children’s data upon request
- Audit trail of parent/guardian permissions
Failure trend: Non-profits and educational platforms missed parental consent audits and were fined for “selling children’s personal data” without explicit permission.
5. AI-Generated Profiling and User Consent (2026 Focus)
EU AI Act Consent Requirements (effective early 2026)
Article 9(2) High-Risk AI (including recruitment systems, credit scoring, and biometric identification) requires explicit user consent when:
| AI Use Case | Consent Needed? | Content of Consent Text | |————-|—————–|————————| | AI-driven automated decisions | Yes | Explain decision logic, impact, data sources, right to human review. | | AI training on personal data | Yes | Explain that model may learn biases; guarantee anonymized fine-tuning. | | AI-powered profiling for marketing | Yes | Specify categories, frequency, data sources, and user right to opt-out per segment. | | AI-based health diagnosis support | Yes | Disclose medical accuracy level, legal responsibility, and right to data deletion. |
U.S. State AI Consent (Emerging in 2026)
| State | AI Consent Required? | Trigger | |——-|———————-|———| | California | Yes (SB-244) | AI-driven “decisions that have a material legal or financial impact” | | Colorado | Yes (CPA AI addendum) | AI that makes “substantially similar” decisions as human agents | | Connecticut | Yes (HB-5423) | “Automated decision-making technology” used for employment or housing |
Key Requirements for AI Consent in 2026:
- Plain language explaining AI involvement and impact
- Right to opt-out without penalty from AI-driven services
- Data subject access rights: right to see AI decisions, obtain human review, request deletion of training data
- Algorithm transparency: model version, data sources, and training methodology
- Audit rights: quarterly internal audits and external verification for high-risk AI
Critical gap: Most consent tools still don’t track AI-specific consent in their audit logs; audit failures for AI consent are rising in 2026.
6. Practical Tests for Your User Consent Stack (7-Live-Check Framework)
Run these checks monthly against your consent system to avoid regulatory fines and protect user trust.
| # | Check | How to Verify | |—|——-|—————| | 1 | EU Default Deny | Open site from EEA IP in incognito → Does GA/Ads fire without prior consent? Should be blocked/cookieless. | | 2 | GPC Recognition | Use browser extension or curl to set Sec-GPC: true header → Does system honor and remember across requests? | | 3 | Visual Parity of Accept/Reject | Screenshot banner → Compare font size, contrast, and placement of “Accept All” vs. “Reject All”. | | 4 | Granular Overrides Functional | In preference center, toggle “Marketing” off → Verify that ad service stops firing immediately. | | 5 | Withdrawal Accessible | On any page, find “Privacy Choices” → Click and ensure you can revoke per-channel within 3 clicks. | | 6 | Children Consent Audit | Create test child account (<16) → Verify parental consent email sent and consent recorded. | | 7 | AI Consent Documentation | For AI-driven decisions, check audit logs: was explicit consent captured, stored, and revocable? |
Quick 2026 Compliance Self-Assessment
If any check fails → You’re not GDPR-compliant for user consent.
| Area | Pass? | Result | |——|——|——–| | EU default deny + consent-only for marketing? | ❓ | Must be Yes for all EEA/UK traffic. | | GPC signals honored + 24-month memory? | ❓ | Must be Yes for 11+ states. | | Children <16 opt-in or parental consent? | ❓ | Must be Yes for all under-16 accounts. | | Visual parity of accept/reject? | ❓ | Must be Yes (CNIL now enforces). |
2026 enforcement reality: ICO, CNIL, and state AGs are publishing quarterly audit results; failures are now publicly named.
7. Implementation Roadmap for User Consent 2026
| Phase | Actions | Owner | Timeline | |——-|———|——-|———-| | Audit | Map all data flows: identify which sites/apps collect personal data per jurisdiction; build a consent matrix (purpose × region × data type). | Legal/Compliance | Week 1 | | CMP Selection | Choose EU Digital Omnibus–ready consent management platform that includes automatic GPC support, granular overrides, and audit logging. | IT/Privacy Lead | Week 2 | | Consent UX | Redesign banners and preference centers for 2026: single-click acceptance, equal visual weight, no cookie walls, transparent withdrawal. | UX/Design | Week 3 | | Region-Specific Logic | Deploy consent configuration: EU = default deny + consent stack, U.S. = default allow + opt-out + GPC, all = children consent module. | DevOps/Infrastructure | Week 4 | | AI Consent Integration | Add AI-specific consent capture and audit hooks; ensure opt-out from AI decisions is preserved in backend decisions. | Data Science/AI Team | Week 5 | | Testing Pipeline | Build automated tests for the 7 Live Checks + GPC integration; run monthly regression against staging. | QA/Engineering | Week 6 | | Training & Documentation | Train support teams on consent questions; update privacy policy with 2026 consent disclosures. | HR/Operations | Ongoing |
Key Technical Implementation Details
For EU (Default Deny + Consent Stack):
- Use server-side cookies.js or comparable to block analytics and ads until explicit consent
- Store consent choice in first-party cookie with 7-day memory if user returns without consent
- Respect TCF 2.3 vendor list for advertising ecosystem compliance
For U.S. (Opt-Out + GPC):
- Implement server-side GPC header detection
- Map GPC to Do-Not-Sell/Opt-Out state in CRM and analytics
- Ensure data sale APIs are disabled when GPC is set
For Children (Age Verification)::
- Deploy age gate at registration (digital ID provider or parent email verification)
- Record parent/guardian consent in secure database with audit trail
- Enable deletion workflows for children’s data upon parental request
Time crunch: EU Digital Omnibus and new state children’s consent laws are in force by Q3 2026; compliance must be achieved before July 1, 2026.
8. Resources and Internal Links
- Cookie Consent Manager: 2026 GDPR Compliance Guide — Comprehensive CMP selection guide
- What Is a Consent Management Platform (CMP) in 2026? — CMP selection checklist
- Consent Management Platform: GDPR Compliance Guide (2026) — Deep dive on EU CMP requirements
- What Is Cookie Consent in 2026? — Cookie consent UX best practices
- Google Tag Manager Cookie Consent: 7 Live Checks Before You Publish in 2026 — GTM integration testing
- What Is Consent Management in 2026? — System-level consent architecture
- Consent Management Platform: 2026 Market Landscape — CMP evaluation framework
9. Related Images
Conclusion
User consent in 2026 is no longer a checkbox—it’s a dynamic operational system that must simultaneously support:
| Region | Model | Key Legal Triggers | |——–|——-|——————| | EU/UK | Opt-in | Default deny, granular categories, equal visual weight of accept/reject, no cookie walls, 7-day refusal memory | | United States | Opt-out (with GPC) | Sensitive data, children, universal opt-out recognition, AI consent where applicable |
Regulators are watching: CNIL’s €3.5M fine in January 2026 and ICO’s £17.5M PECR cap increase are clear signals that consent failures are no longer just privacy issues—they’re revenue and executive-risk issues.
Bottom line: If your consent stack doesn’t support both the EU Digital Omnibus liberalization (removing consent for low-risk purposes) and stricter consent requirements (children, sensitive data, AI), you’ll face fines, customer churn, and brand damage. The path forward: audit, upgrade CMP, and build a global consent strategy that respects regional models while maintaining operational simplicity.
Next step: Run the 7 Live Checks against your live site this week. If any check fails, fix it before the next coordinated enforcement sweep.
Published: October 9, 2026
Keywords: user consent