
What Is a Cookie Internet Search Really Asking in 2026? Plain-English Meaning, Uses, and 7 Checks
If you are searching what is a cookie internet on November 18, 2026, the first useful answer is this: most people are really asking about an internet cookie, web cookie, or browser cookie.
The phrase is awkward, but the question behind it is real.
People usually want to know:
- what a cookie actually is;
- what a website uses it for;
- whether it is harmless, necessary, or used for tracking; and
- when consent, opt-out, or browser controls are supposed to change the live behavior.
If you want the closest companion reads first, start with our guides to web cookies, browser cookies, and what are cookies on a website. This page stays focused on the search phrase what is a cookie internet and the practical review a privacy, marketing, or website team should run this week.
If your team needs help turning cookie disclosures, consent controls, and live browser behavior into one coherent operating system, DataShyre can help with consent management, data mapping, and implementation support that keeps the live stack aligned with the policy layer.
1. In plain English, an internet cookie is browser memory a website uses later
The best plain-English answer to what is a cookie internet is not complicated.
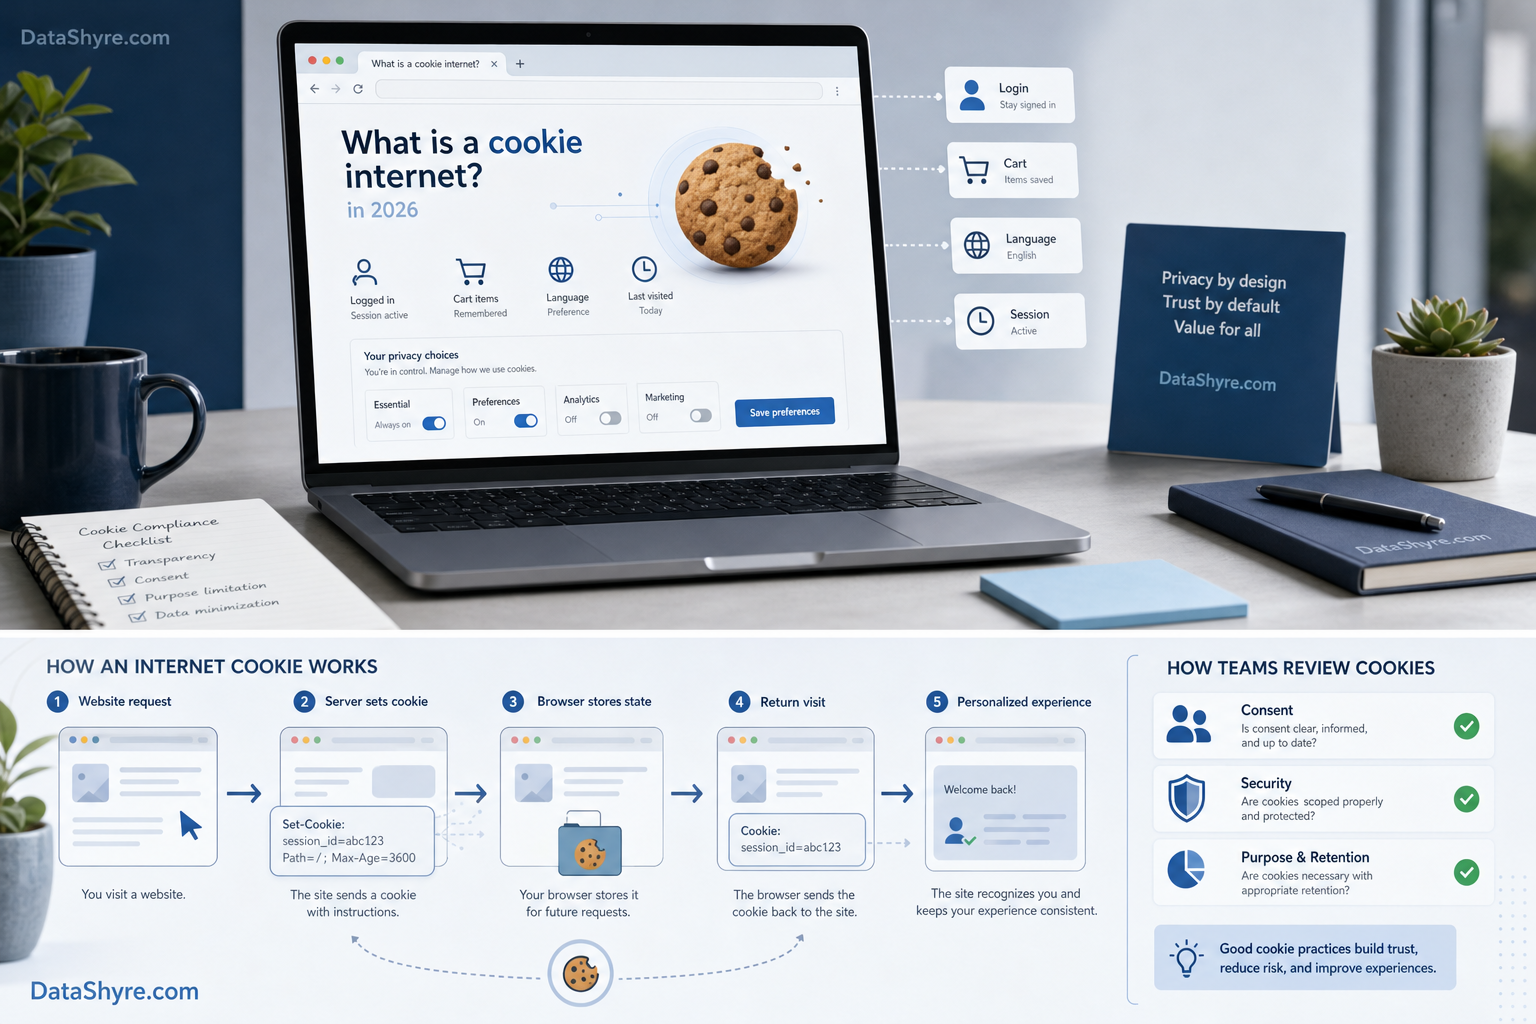
MDN’s current HTTP cookie guide says a cookie is a small piece of data a server sends to a web browser, which the browser may store and send back later with new requests. The UK’s ICO still describes cookies as small text files stored on a user’s device when they access a website or similar service.
That simple mechanism lets a website remember things like:
- that you are signed in;
- what is in a cart;
- which language or region you selected;
- whether you already dismissed a notice; or
- which settings you chose on an earlier visit.
So if someone asks what is a cookie internet, the practical answer is:
it is browser-side memory that helps a website recognize state on a later request.
2. The technical mechanism is simple, but the purpose is what matters
The next step is understanding how the cookie gets there.
MDN’s current HTTP references still show the basic flow clearly:
- the website responds with a
Set-Cookieheader; - the browser stores the cookie under the rules attached to it;
- the browser may send it back later in the
Cookierequest header; and - the website uses that value to keep state between otherwise separate requests.
That is why cookies became so common across the internet in the first place. HTTP is stateless by default, so cookies gave websites a practical way to remember continuity.
But the more useful what is a cookie internet question is not only how does the header work.
It is what business purpose does this remembered value support?
That purpose is what separates a helpful session cookie from a more sensitive analytics or advertising identifier.
3. Not every internet cookie does the same job
This is where the plain-English explanation gets more useful.
Most real cookie reviews split internet cookies into groups such as:
- necessary or security cookies for sign-in, fraud prevention, checkout continuity, or load balancing;
- preference cookies for language, region, or remembered settings;
- analytics cookies for measuring visits and behavior; and
- advertising or profiling cookies for attribution, audience building, personalization, or cross-context recognition.
Your Europe still says that, depending on purpose, some cookies require consent before use, while other cookies may fall under limited exceptions. That is why the purpose map matters first.
So when someone asks what is a cookie internet, I would not stop at small file.
I would also ask:
- what category it belongs to;
- whether the website could function without it;
- whether another company receives the resulting data; and
- whether the person visiting the site would reasonably expect that purpose.
4. Browser changes did not make internet cookies irrelevant
One of the easiest mistakes is assuming that modern browsers already solved the entire cookie problem.
They did not.
Firefox’s current support materials still say cross-site tracking cookies are disabled by default for Firefox users, and Total Cookie Protection keeps cookies in a separate jar for each website. Chrome’s current DevTools documentation still gives teams a direct way to inspect cookies, including third-party-cookie behavior, in the browser.
That matters because the 2026 review is not do cookies exist at all.
It is:
- which cookies still appear under real browser conditions;
- whether they are first-party or tied to another domain;
- whether the site still behaves properly when cross-site cookies are restricted; and
- whether the browser shows a different story than the privacy copy on the page.
So what is a cookie internet in 2026 is partly a browser question, not only a policy question.
5. Consent and opt-out rules depend on where the user is
This is where what is a cookie internet turns from a web-technology definition into a compliance workflow.
EU and UK branch
Your Europe still says that cookies requiring consent cannot be set when the webpage first opens, and that the user must receive clear and comprehensive information about the cookies and their purpose. The ICO’s April 29, 2026 finalized guidance also makes clear that the review should extend beyond classic cookies to broader storage-and-access technologies such as scripts, tags, and similar methods.
That means optional analytics, advertising, or similar tracking-oriented internet cookies often need a valid prior-consent path for EU- or UK-facing experiences unless an exception applies.
California branch
California changes the practical question.
The California Department of Justice still describes Global Privacy Control as a “stop selling or sharing my data switch” available in some browsers or as an extension. For many California-facing reviews, the question is not only do we show a banner.
It is also:
- whether the notice is accurate;
- whether the opt-out path exists where required;
- whether GPC is honored where sale or sharing is in scope; and
- whether downstream ad-tech behavior actually changes after the signal.
That is why a nice-looking privacy popup can still fail a real what is a cookie internet review.
6. Internet cookies are also a security settings problem
Not every cookie issue is a consent issue.
Some are basic security hygiene.
MDN’s current cookie guidance still points teams toward attributes like Secure, HttpOnly, and deliberate SameSite settings. Chrome DevTools still exposes those fields in a way that makes live validation possible.
So if an internet cookie supports sign-in, account continuity, or other sensitive flows, I would check at least:
- whether
Secureis present where it should be; - whether
HttpOnlyis used to keep JavaScript away from sensitive values when appropriate; - whether
SameSitebehavior is deliberate instead of accidental; - whether the scope is broader than it needs to be; and
- whether the lifetime matches the purpose and risk.
Weak cookie security and weak privacy operations often show up together.
7. The fastest useful answer is to test live behavior, not just define the term
The strongest answer to what is a cookie internet is operational.
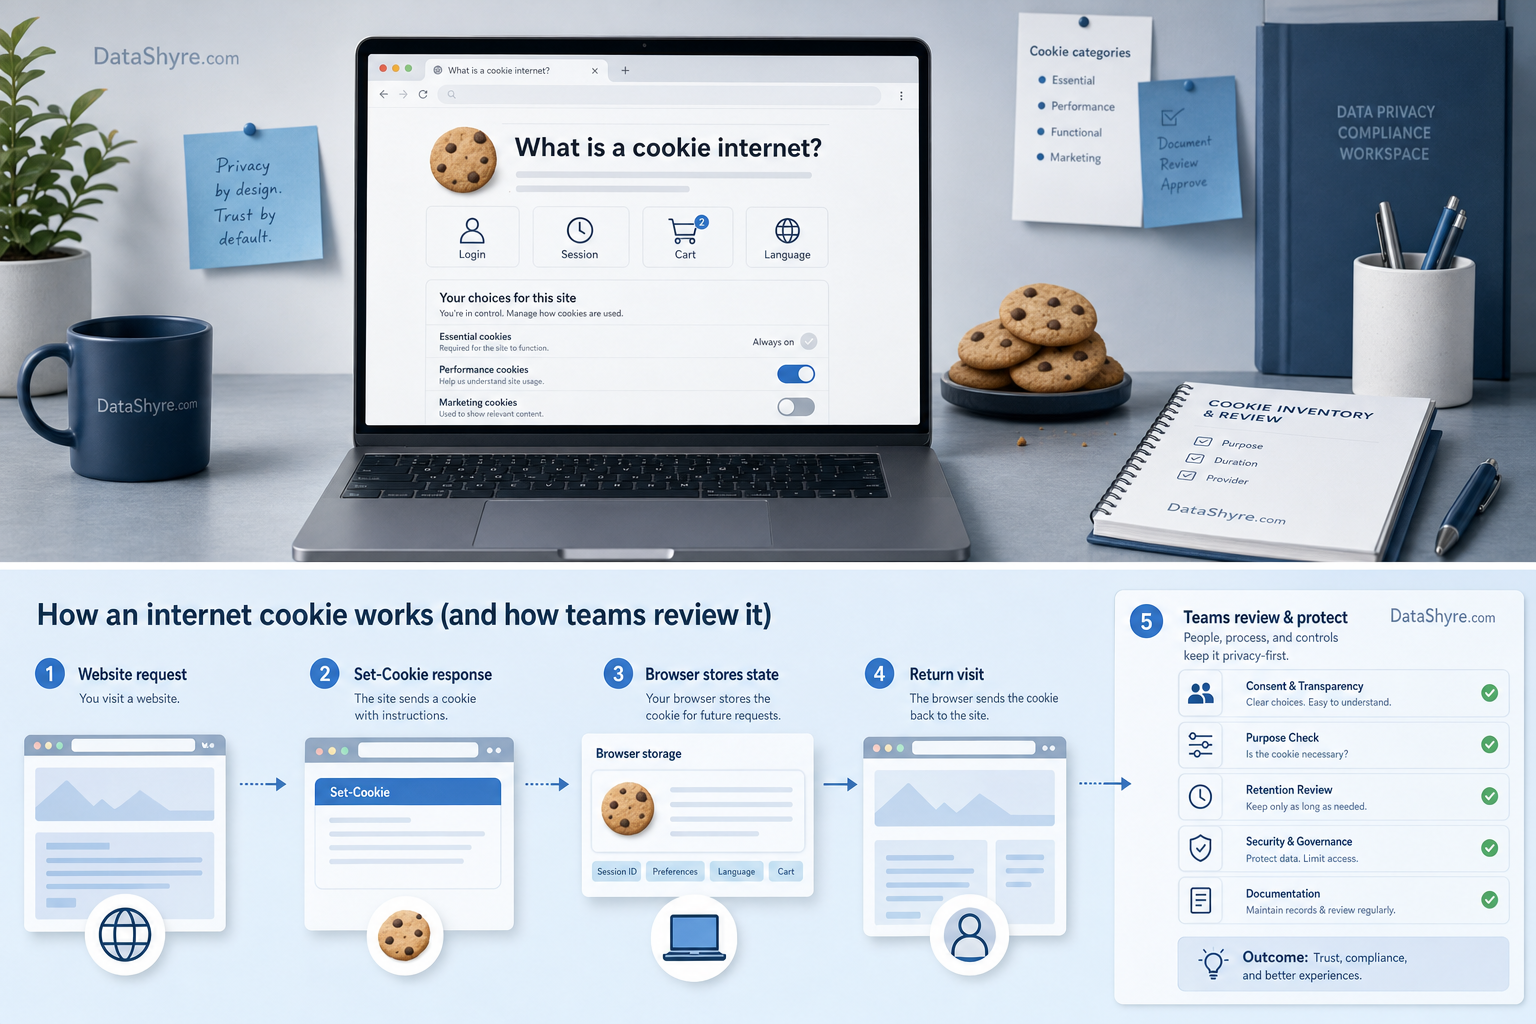
If I were reviewing a live site this week, I would use this order:
- load the page in a clean browser state;
- inspect which cookies and related storage appear before any user choice;
- classify them by necessary, preference, analytics, advertising, or embedded-third-party purpose;
- compare the no-choice, reject, accept, and later-withdrawal states;
- test California opt-out or GPC behavior where relevant;
- inspect security settings on the cookies that support account or session flows; and
- compare the live findings against the cookie notice, privacy policy, and vendor list.
That sequence answers the real search intent much faster than debating wording alone.
FAQ
Is an internet cookie the same thing as a browser cookie?
Usually, yes in everyday usage. When people search what is a cookie internet, they usually mean the browser cookie mechanism websites use to remember state across requests.
Are all internet cookies used for tracking?
No. Some cookies support basic functions such as sessions, security, carts, or preferences. The higher-risk branch is usually optional analytics, advertising, personalization, or cross-context recognition.
Does every internet cookie need consent?
No. Some cookies may qualify for recognized exceptions, while optional analytics or advertising cookies often need a different consent or opt-out analysis depending on the jurisdiction and purpose.
Official sources used
- MDN: Using HTTP cookies
- Chrome DevTools: View, add, edit, and delete cookies
- ICO: Cookies and similar technologies
- ICO: What are storage and access technologies?
- ICO: How do we comply with the PECR rules?
- Your Europe: How to use cookies on your website
- California DOJ: CCPA overview
- California DOJ: Global Privacy Control
- Firefox Help: Third-party cookies and Firefox tracking protection