
What Are Cookies on the Internet in 2026? Plain-English Guide to What They Do and What to Check
If you are searching what are cookies on the internet on October 29, 2026, the shortest honest answer is this: cookies are small pieces of data that websites store in your browser so the site can remember something about your visit later.
That sounds simple because, at the technical level, it is simple.
The harder part is that cookies now sit inside a much wider tracking environment that can also include pixels, fingerprinting, local storage, scripts, and tags. So the practical 2026 question is not only what is a cookie?
It is also:
- what the cookie is doing;
- whether it is necessary for the service or mainly for measurement or advertising;
- whether another company gets access to the data;
- whether consent or opt-out rights apply in that region; and
- whether the live site actually changes behavior after the user makes a choice.
If you want the related explainers first, start with what is cookie consent, cookie consent requirements, and website privacy checker. This page stays narrower. It answers what are cookies on the internet in plain English and then connects that answer to the real privacy checks that matter now.
The plain-English answer
When you visit a website, the site can ask your browser to store a small data value and send it back later.
That is the core cookie mechanism.
The ICO’s public guidance still describes a cookie as a small file of letters and numbers downloaded to a computer when a person visits a website. Its more technical 2026 storage-and-access-technologies guidance explains the same idea in developer terms: cookies are small text files generated by a web server responding to a website request.
That mechanism lets a site remember useful things like:
- that you are logged in;
- which language or privacy setting you picked;
- what is in your shopping cart;
- whether you have already closed a notice; or
- that your browser visited before.
So the cleanest answer to what are cookies on the internet is not good or bad.
It is browser memory that can be used for many different purposes, some low risk and some much more intrusive.
What internet cookies usually do
Most cookie questions become clearer if you start with function instead of label.
In practice, cookies on the internet often support one of these branches:
- session or security cookies that keep a person signed in or help prevent abuse;
- preference cookies that remember settings like language, region, or privacy choices;
- analytics cookies that measure visits, page paths, or product usage; and
- advertising or profiling cookies that help target ads or recognize a person across contexts.
The first two branches are usually the easiest to explain.
The privacy friction usually starts in the last two.
That matters because many people ask what are cookies on the internet when they are really asking something more practical: Which cookies are just helping the site work, and which ones are helping somebody measure or profile me?
That is the useful question.
First-party versus third-party cookies
You will often hear what are cookies on the internet explained through the first-party versus third-party distinction.
That is still helpful, but it is not the whole story.
The ICO’s 2026 guidance says a third party means a domain other than the one the user is visiting. In simple terms:
- a first-party cookie is generally tied to the site you are on; and
- a third-party cookie is tied to another service involved in that page experience.
The FTC’s consumer guidance gives the practical privacy effect. When the site you visit tracks you, that is first-party tracking. When it lets another company track you, that becomes third-party tracking.
That difference matters because third-party tracking can be used across multiple websites or services.
But the ICO makes an equally important point: first-party versus third-party is not the only legal test. What matters most is who is responsible for the storage or access and what purpose it serves.
So when someone asks what are cookies on the internet, I would not stop at Is it first-party?
I would also ask:
- what exact purpose does it serve;
- would the service still work without it;
- does it support cross-site advertising or profiling;
- which vendor receives the resulting data; and
- how long the identifier lasts.
Cookies are no longer the whole tracking story
This is one of the main reasons older explainers on what are cookies on the internet can feel incomplete in late 2026.
The old model treated cookies as the whole online-tracking conversation.
The current regulator model is wider.
The ICO finalized its storage-and-access-technologies guidance on April 29, 2026, and that guidance explicitly covers cookies, tracking pixels, device fingerprinting, scripts, tags, web storage, and related technologies. The FTC’s consumer guidance uses the same broader frame and tells readers that websites and apps may track people with a cookie or pixel or through device fingerprinting.
That means a site can look cleaner if you only inspect a cookie table while still sharing data earlier than users expect through other tools.
So the modern answer to what are cookies on the internet is partly educational and partly cautionary:
cookies still matter, but they are only one part of the tracking stack.
When consent matters and when the rule changes by region
This is where the question becomes legal instead of technical.
There is no single global answer to what are cookies on the internet because the compliance rule changes by jurisdiction and by purpose.
EU and UK: many optional tracking uses still need prior permission
The European Commission’s current GDPR guidance still says valid consent must be given through a clear affirmative act, use “clear and plain language”, and allow withdrawal through a route that is “as easy to use as giving consent.”
For many EU and UK web-tracking situations, that means optional analytics, advertising, personalization, or similar non-essential technologies should not simply start running by default.
That does not mean every cookie always needs opt-in.
It means the important branch is usually whether the storage or access is truly necessary for the service requested by the user, or whether it mainly serves a secondary purpose such as measurement, targeting, or profiling.
California: the practical question often changes from opt-in to opt-out
California is one of the reasons the topic gets confusing.
The California Department of Justice says businesses that sell or share personal information must provide a clear and conspicuous opt-out path, and for businesses collecting information online, one acceptable method is a user-enabled Global Privacy Control. The DOJ still describes GPC as a “stop selling or sharing my data switch.”
So for many California-facing website reviews, the useful question is not Do we have an EU-style accept button?
It is:
- are people given the right notice at collection;
- is the required opt-out path available where sale or sharing is in scope;
- is GPC honored where required; and
- do downstream advertising or sharing behaviors actually change.
That is why copied cookie banners can still fail the real privacy test.
Why enforcement is still moving
The topic is not theoretical.
On October 22, 2026, CNIL fined FNAC DARTY companies 7 million euros over cookie and tracking-device failures tied to a mobile-app tracker used without prior consent for personalized recommendations and training its recommendation algorithm.
That example matters because it reinforces two points:
- cookie and tracker rules still apply beyond classic desktop websites; and
- regulators are still looking at the actual purpose and behavior of the tracker, not only at the wording around it.
So if you are asking what are cookies on the internet from a compliance angle, the answer is still current, operational, and enforced.
What users can do if they want less tracking
There is also a practical consumer side to what are cookies on the internet.
The FTC’s advice points people toward straightforward steps:
- clear cookies and browsing history if you want to reduce memory from prior visits;
- review browser privacy settings;
- use available settings or tools that limit personalized ads or tracking;
- read cookie or privacy choices instead of assuming they all mean the same thing; and
- remember that choices may be browser-specific, device-specific, or site-specific.
That last point is worth stressing.
Rejecting one banner on one browser does not automatically solve tracking everywhere, and deleting cookies does not automatically stop other forms of tracking such as fingerprinting.
How I would review a live site this week
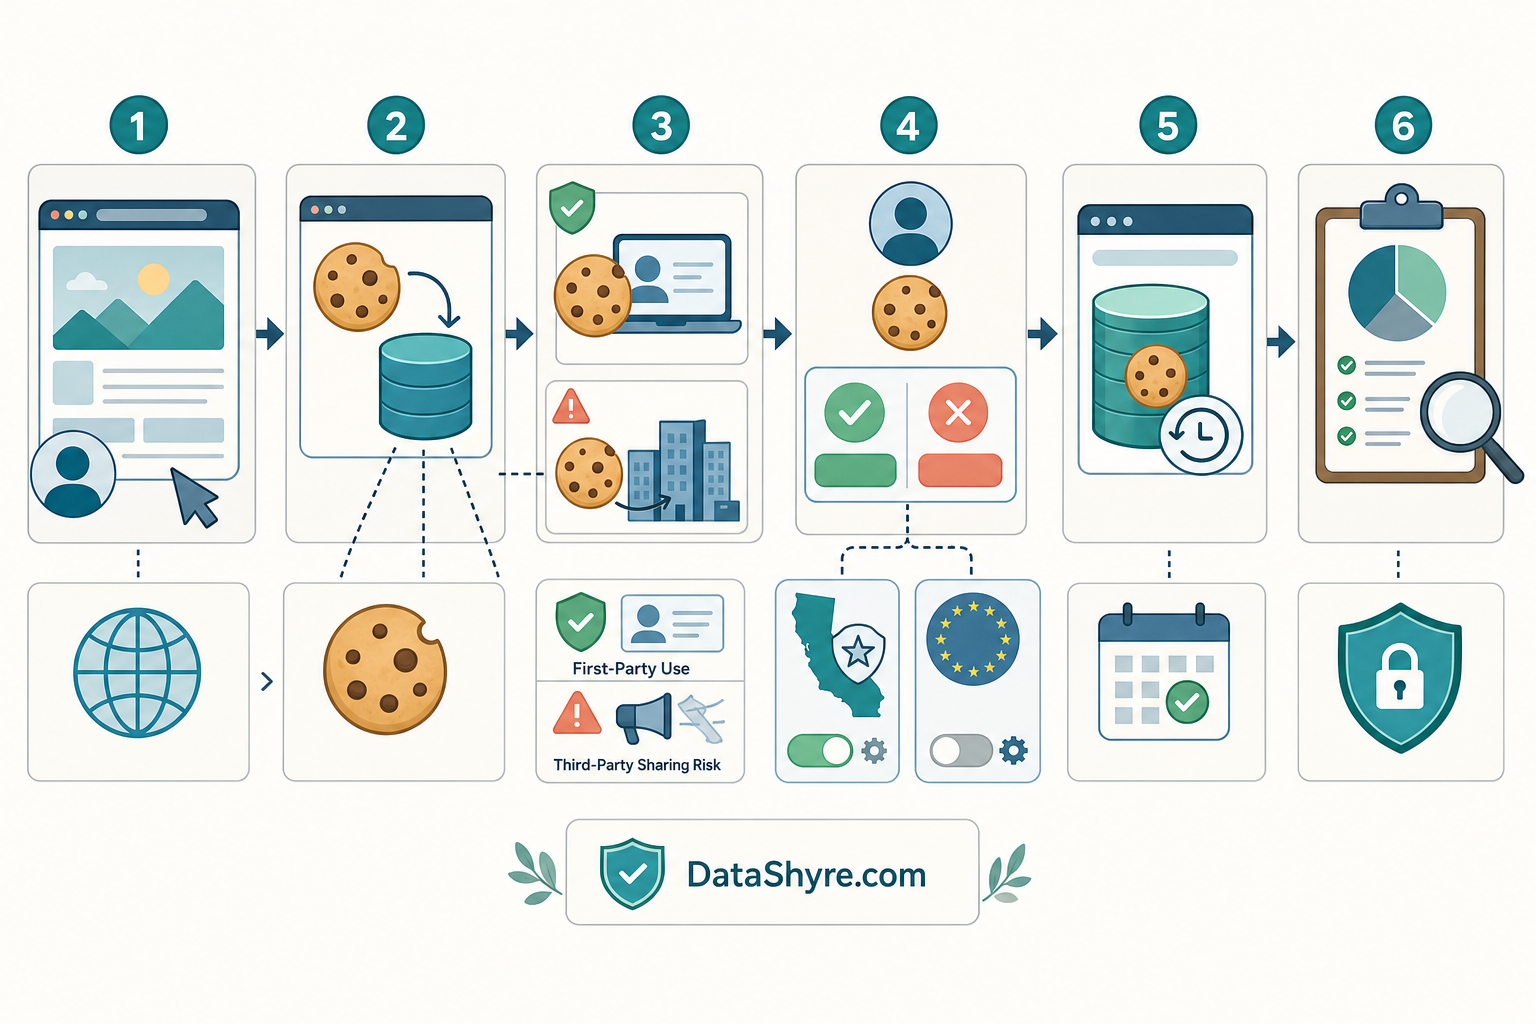
If someone asked me what are cookies on the internet and also wanted the practical audit sequence, I would use this order:
- list which cookies and other storage or access technologies appear before any user action;
- separate necessary, preference, analytics, advertising, and embedded-media uses;
- identify which vendors receive data and which tools create identifiers;
- test what changes after reject, accept, category-level choice, and later withdrawal;
- test California opt-out and GPC handling if sale or sharing may apply;
- compare the live findings against the privacy policy and notice language; and
- save evidence so the result can be retested after the next release.
That sequence usually answers the real version of what are cookies on the internet faster than another abstract debate about banner copy.
FAQ
Are all cookies on the internet bad?
No. Many cookies support ordinary functions people expect, such as logging in, remembering language preferences, saving a cart, or preserving a security session. The higher-risk branch is usually optional analytics, advertising, personalization, or cross-site profiling.
Do third-party cookies create all of the risk?
No. Third-party cookies often raise bigger cross-site tracking concerns, but first-party technologies can still create privacy issues depending on purpose, downstream sharing, and how the data is used.
If I delete cookies, does that stop all tracking?
No. Deleting cookies may remove some stored browser identifiers, but it does not automatically stop tracking pixels, fingerprinting, or other storage-and-access technologies.
Bottom line
So, what are cookies on the internet?
They are small browser data records that help websites remember state across visits or requests. In 2026, though, that simple mechanism belongs to a broader tracking environment that may also include pixels, tags, fingerprinting, and similar technologies.
That is why the useful question is not only what a cookie is.
It is whether the use is necessary, who receives the data, what regional privacy rule applies, and whether the live site actually behaves the way its notice or choice interface claims it will.
If you can answer those questions clearly, you understand much more than the definition.
Sources
- ICO, Cookies: https://ico.org.uk/for-the-public/online/cookies
- ICO, What are storage and access technologies?: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/what-are-storage-and-access-technologies/
- ICO, Final storage and access technologies guidance published: https://ico.org.uk/about-the-ico/media-centre/news-and-blogs/2026/04/final-storage-and-access-technologies-guidance-published/
- FTC Consumer Advice, How Websites and Apps Collect and Use Your Information: https://consumer.ftc.gov/articles/how-websites-and-apps-collect-and-use-your-information
- European Commission, Legal grounds for processing data: https://commission.europa.eu/law/law-topic/data-protection/information-business-and-organisations/legal-grounds-processing-data_en
- California Department of Justice, California Consumer Privacy Act (CCPA): https://oag.ca.gov/privacy/ccpa
- California Department of Justice, Global Privacy Control (GPC): https://oag.ca.gov/privacy/ccpa/gpc
- CNIL, Cookies and mobile application: 7 million euros fine against FNAC DARTY PARTICIPATIONS ET SERVICES and FNAC DIRECT: https://www.cnil.fr/en/sanction-app-cookies-fnac