
What Are Cookies for Websites in 2026? The Real Jobs They Still Do
If you are searching what are cookies for websites on November 13, 2026, the shortest useful answer is this:
websites use cookies to remember something between one page load and the next.
Sometimes that memory is expected and helpful.
Sometimes it is optional, invasive, or both.
That is why the real answer to what are cookies for websites is no longer just a browser definition. It is a purpose question:
- what is the site trying to remember;
- why does it need that memory;
- how long does it keep it;
- whether another company receives the resulting data; and
- whether consent or opt-out controls actually change the live behavior.
If you want the adjacent explainers first, start with what are cookies on a website, browser cookies, and cookie notice. This page stays focused on what are cookies for websites and the practical reasons teams still rely on them.
If your team needs help classifying necessary versus optional cookies, aligning banners with runtime behavior, or mapping website tracking to region-specific rules, DataShyre can help with consent management, implementation review, and cleanup.
1. The main job is browser memory
The first answer to what are cookies for websites is still the simplest one.
Cookies let a website remember a previous interaction when the browser makes another request. The ICO’s 2026 materials still describe cookies as part of a wider group of “storage and access technologies” and explain that they are widely used to make websites work, work more efficiently, and provide information to the website operator.
So when someone asks what are cookies for websites, the most common answers are still things like:
- keeping a user signed in;
- remembering what is in a shopping cart;
- preserving language or region choices;
- storing consent or preference settings;
- supporting security or fraud controls.
Those are not all equally risky, but they are all common reasons websites still use cookies.
2. Websites use cookies for sessions, not just long-term tracking
One reason the phrase what are cookies for websites causes confusion is that people often jump straight to surveillance.
Some cookies do support tracking or profiling.
Others are much more ordinary.
A website may use short-lived session cookies so the browser can move through:
- login flows;
- checkout steps;
- account areas;
- temporary security checks;
- multi-page forms.
Persistent cookies are different because they keep data beyond the current session. That can still be legitimate, but it raises a better audit question:
why does this website need the memory to last that long?
If a team cannot explain the lifetime of a cookie in plain English, it usually has not finished the privacy review.
3. Necessary cookies and optional cookies do very different jobs
This is the most practical part of what are cookies for websites.
Your Europe still says websites generally need consent before installing cookies, while also reminding people that “Not all cookies require your consent.” It highlights familiar exceptions for cookies used only to carry a communication or to provide an online service the user explicitly requested, such as load balancing or shopping-basket continuity.
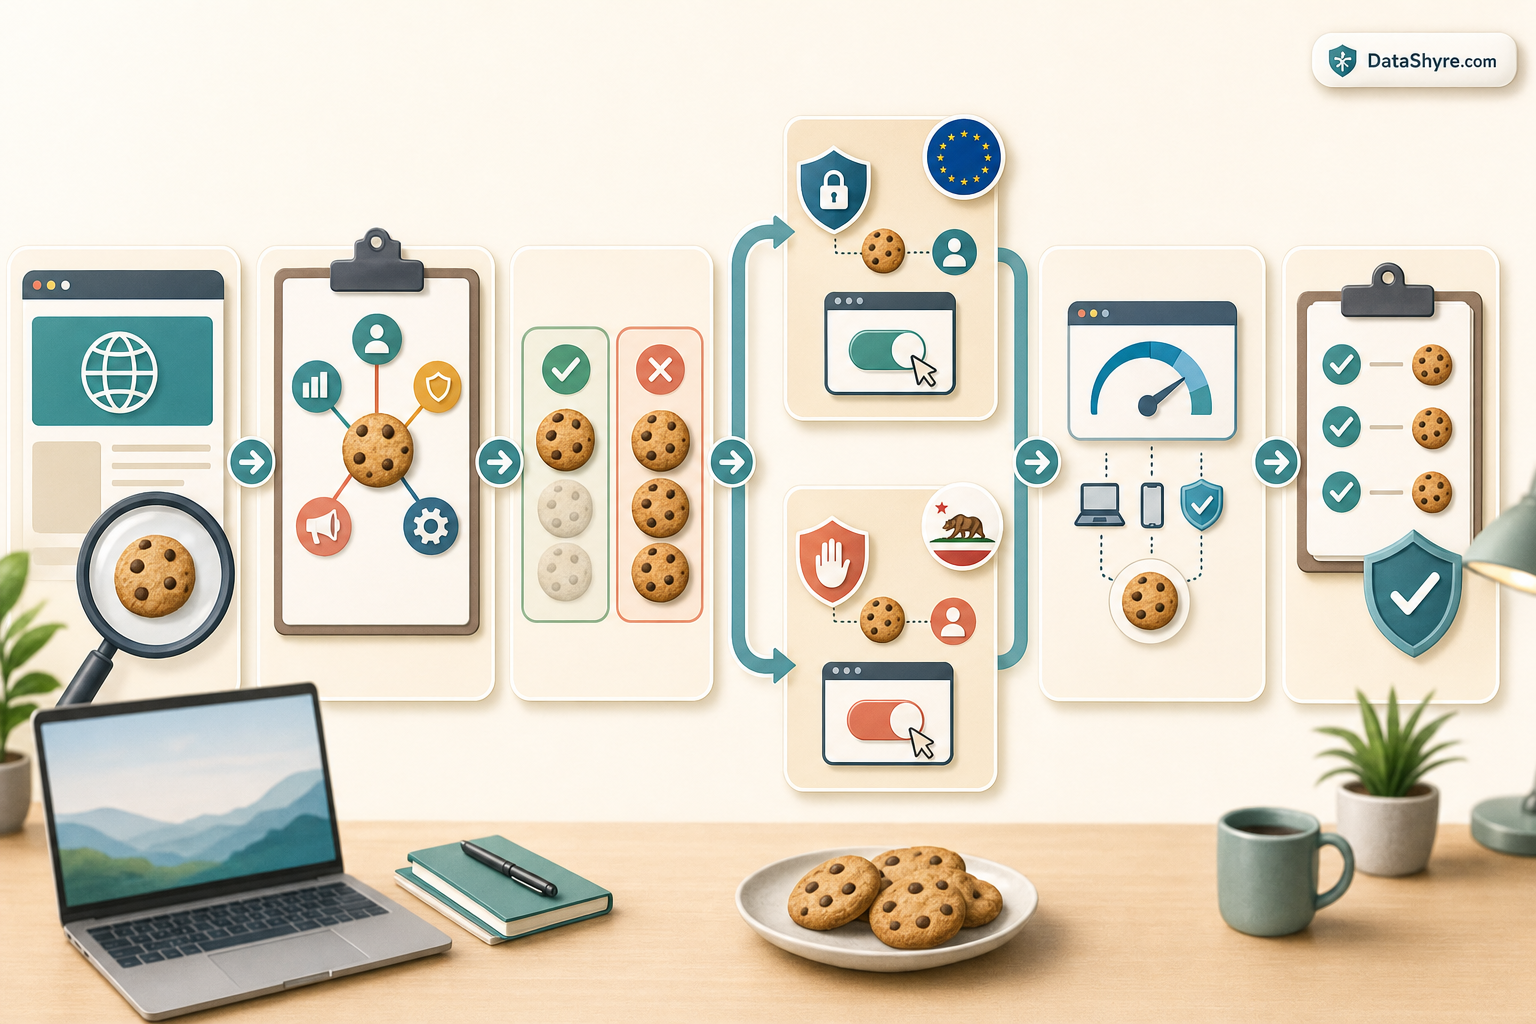
That means a good website-cookies review usually separates purposes into groups like:
- necessary login, basket, or security support;
- site-preference memory;
- analytics and measurement;
- advertising and retargeting;
- personalization and profiling;
- embedded third-party tools.
This is where many weak implementations fail.
They treat everything as necessary, even when some cookies mainly support analytics or advertising.
So a sharper answer to what are cookies for websites is:
some are for the service the user asked for, and some are for the business goals around that service.
Those are not the same thing.
4. Cookies are not the whole tracking picture anymore
A narrow answer to what are cookies for websites can miss the modern implementation problem.
The ICO’s current guidance deliberately uses the broader label “storage and access technologies” because websites may rely on scripts, pixels, tags, fingerprinting, or web storage in addition to classic cookies.
That matters because a website can reduce obvious third-party-cookie usage while still running a stack that does roughly the same measurement or advertising work through other methods.
So when reviewing what are cookies for websites, do not stop at:
- cookie names;
- first-party versus third-party labels;
- the banner text alone.
Also check:
- which scripts and tags load before a choice;
- which vendors receive data;
- whether consent or refusal changes the network behavior;
- whether the policy describes the live stack accurately.
If the cookie list looks clean but the page still loads optional tracking before the user acts, the review is not finished.
5. The rules change depending on where the website operates
This is where what are cookies for websites turns from a technical question into a compliance question.
EU and UK branch
The European Commission’s current consent guidance still says a consent request must be “clear and concise”, easy to understand, and distinguishable from other information. The ICO’s finalized guidance from April 29, 2026 also makes clear that prior-consent analysis now covers a broader set of storage and access technologies, not just old-school cookie files.
So for many EU- or UK-facing sites, optional analytics, advertising, and personalization cookies still trigger a prior-consent review unless an exception applies.
California branch
California changes the practical question.
The California Department of Justice still describes Global Privacy Control as a “stop selling or sharing my data switch.” The CPPA FAQ also says businesses must honor qualifying opt-out preference signals such as GPC and, in most instances, must still provide a clear and conspicuous link such as Do Not Sell or Share My Personal Information, Your Privacy Choices, or Your California Privacy Choices.
That means what are cookies for websites is not answered the same way everywhere.
For California-facing properties, the useful audit may focus less on prior consent and more on:
- whether sale or sharing logic exists;
- whether the opt-out path works;
- whether GPC is honored where required;
- whether downstream advertising behavior actually changes.
If a website uses one polished banner to imply that every regional rule is handled automatically, it is probably overstating what the control really does.
6. Enforcement still turns on real purpose, not just wording
This topic is not theoretical.
On October 22, 2026, the CNIL fined FNAC DARTY PARTICIPATIONS ET SERVICES and FNAC DIRECT 7 million euros over a tracker used in a mobile app without prior consent. The CNIL said the tracker collected browsing-history information to show personalized recommendations and to train a recommendation algorithm.
That matters for what are cookies for websites because it reinforces a simple point:
regulators still care what the technology is actually doing.
Not just what the banner says.
If a cookie or adjacent tracker supports personalized recommendations, cross-context advertising, or behavior-based profiling, teams should not assume a vague improve your experience sentence is enough.
7. A better audit question is why each cookie exists
If I were auditing what are cookies for websites on a live property this week, I would not start by asking whether the banner looks modern.
I would ask:
- what business or product function each cookie supports;
- whether the user requested that function;
- whether the same result could be achieved with less data or a shorter lifetime;
- whether another vendor receives the data;
- whether refusal or opt-out measurably changes the page behavior;
- whether the privacy notice and cookie controls match the runtime;
- whether the team re-tests after new tags, embeds, or vendors go live.
That sequence answers the real version of what are cookies for websites much faster than another banner redesign.
FAQ
Are cookies for websites always used for tracking?
No. Many websites still use cookies for expected functions such as login state, basket memory, language settings, or consent preferences. The higher-risk branch is usually optional analytics, advertising, or profiling.
Why do some websites still need cookies if browsers are changing tracking features?
Because websites still need state and continuity. Browser changes mainly affect how far websites and vendors can use that state for cross-site tracking, attribution, or profiling.
Does every website cookie need consent?
No. Official EU guidance still distinguishes between strictly necessary cookies and optional uses such as many analytics or advertising functions. California also asks a different question in many cases, especially when sale or sharing and GPC are involved.
Bottom line
The best short answer to what are cookies for websites is:
they help a website remember something useful, commercial, or behavioral between interactions.
The important follow-up is:
which of those purposes are necessary, which are optional, and which controls actually change the live behavior?
That is the line between ordinary website memory and privacy trouble.
Official sources used
- ICO guidance on storage and access technologies
- ICO announcement on the final SAT guidance, April 29, 2026
- Your Europe guidance on data protection and online privacy
- European Commission information for individuals on consent
- California DOJ page on Global Privacy Control
- California Privacy Protection Agency FAQ
- CNIL enforcement notice on the FNAC DARTY cookies and mobile app case