
Website Popups in 2026: 7 Privacy Checks Before You Push One Live
If you are searching for website popups on November 15, 2026, the wrong first question is usually will this increase conversions.
The more useful question is whether the popup changes your privacy surface in ways your team can still explain, control, and prove later.
That matters even more in late 2026. On March 19, 2026, the European Data Protection Board launched its coordinated enforcement action on GDPR “transparency and information obligations.” On April 29, 2026, the UK’s ICO finalized its current storage-and-access technologies guidance, keeping a strong focus on consent mechanics and runtime behavior. And California’s current CCPA regulations, effective January 1, 2026, still require privacy-request and consent methods to be “Easy to understand” and to preserve symmetry in choice.
If you want nearby context first, start with our guides to cookie policy popup, website privacy checker, and privacy policy for website. This page stays broader than cookie banners alone. It is the website popups review I would use this week before a lead capture, notice, or consent popup goes live.
If your team is trying to line up popup behavior, privacy disclosures, consent logic, and downstream systems, DataShyre can help with consent management, data mapping, and DSR automation. The risky part is rarely making the popup appear. The risky part is everything the popup starts behind the scenes.
1. Decide what the popup is legally doing before you design it
The first website popups mistake is treating every popup like the same legal object.
They are not the same.
One popup might be:
- asking for consent before optional tracking starts;
- giving notice at the point of data collection;
- capturing an email address for a newsletter;
- collecting a demo request or callback request;
- reopening privacy choices later.
If you blur those jobs together, the wording gets sloppy fast.
The European Commission’s current GDPR guidance still makes the key point many teams skip: consent is only one possible legal ground. Depending on the processing, the right basis may instead be contract, legal obligation, legitimate interests, or another lawful basis. So before building website popups, decide whether the popup is truly collecting consent, simply giving notice, or starting a form workflow that depends on a different legal basis.
That one decision affects the copy, the buttons, the timing, the downstream systems, and the proof you need to keep.
2. Put the privacy explanation at or before the point of collection
This is where attractive website popups often become weak privacy interfaces.
A popup that asks for an email address, phone number, location, or other personal data is not just a design pattern. It is a collection point.
California’s current regulations say the Notice at Collection must be made readily available at or before the point of collection, and for webforms can be linked in close proximity to the fields or the submit button. The European Commission’s GDPR guidance points in the same practical direction by requiring privacy information in clear and plain language.
So when reviewing website popups, test whether a normal person can tell:
- who is collecting the data;
- what data is being requested;
- why the data is being requested;
- whether another company will receive the data;
- where the full privacy explanation lives.
If the popup is doing real collection work, the privacy explanation cannot be buried in a footer that only appears after submission.
3. Test what starts before any click, not just what the popup says
Many website popups look harmless until you test the runtime.
The popup itself might appear to be a simple message or form. But the actual stack behind it may also trigger:
- cookies or local storage for frequency control;
- analytics events for impressions or dismissals;
- ad-platform pixels;
- tag-manager rules;
- embedded form scripts from another vendor.
The ICO’s live guidance is still explicit that non-exempt storage and access technologies need prior consent, and that valid consent mechanisms must give users control over those technologies. Its checklist also asks whether the mechanism makes it “as easy to refuse consent as it is to accept.”
That means a serious website popups review should inspect the runtime before any interaction:
- what cookies, storage, or identifiers appear immediately;
- what network requests fire when the popup loads;
- whether reject changes anything in practice;
- whether accept changes only the intended purposes;
- whether hidden embeds or scripts start earlier than the popup implies.
If the runtime behavior disagrees with the copy, trust the runtime.
4. Make the privacy-protective path no harder than the yes path
This is one of the clearest quality tests for website popups.
California’s current rules say methods for submitting privacy requests or obtaining consent must preserve symmetry in choice, meaning the more privacy-protective option cannot be longer, harder, or more time-consuming than the less protective option. The ICO’s current consent guidance lands in nearly the same place operationally: refusal and withdrawal need to be easy in practice, not just theoretically available.
So for website popups, review the interface like this:
- is the privacy-protective option visible on the first layer when consent is being requested;
- is the reject or close route smaller, dimmer, slower, or buried;
- does mobile behavior change the fairness of the flow;
- can the user revisit the choice later without detective work;
- does the later withdrawal route use the same level of effort as the original yes.
A popup can be visually polished and still fail this test.
That is why popup review should never stop at typography, animation, or conversion rate.
5. Match the popup fields and follow-up use to the real lawful basis
This is where website popups often create quiet compliance drift.
A team starts with one purpose, then reuses the same popup for another:
- a newsletter signup becomes a product-updates campaign;
- an ebook gate becomes an SDR follow-up trigger;
- a discount popup becomes an audience-building source for paid media;
- a callback form starts feeding enrichment or lead-scoring tools.
The European Commission’s guidance on legal grounds still matters here because it forces a more honest question: what basis actually supports this processing, and does the explanation match that basis?
If the popup is collecting marketing consent, say that clearly.
If it is starting a contract or demo workflow, explain that accurately instead of lazily labeling everything as consent.
For website popups, the useful check is simple: could your legal, marketing, sales, and ops teams all describe the popup’s real purpose the same way?
If not, the interface is probably promising less than the backend is doing.
6. Follow the data after submission, not just to the thank-you state
Some of the biggest website popups risks live after the form is submitted.
The EDPB’s small-business guidance still distinguishes clearly between controllers and processors, and it expects controllers to choose processors carefully, keep records, and make sure the processor relationship is governed properly.
That matters because a popup rarely ends at the browser.
It often sends data into:
- a CRM;
- an email platform;
- a webinar or booking tool;
- a support platform;
- a webhook or enrichment workflow.
So when reviewing website popups, map the full path:
- which vendor receives the submission first;
- which vendors receive it next;
- whether suppression or consent signals travel with the record;
- whether delete or access requests can reach the downstream tools later;
- whether the published privacy explanation still matches the real destinations.
If the popup looks lightweight but the vendor chain is sprawling, the privacy risk lives in the chain.
7. Save proof and re-review after changes
The easiest way to over-trust website popups is to judge them only at launch.
The EDPB’s 2026 transparency action is a reminder that what users are told, when they are told it, and how consistently that matches the real processing still matters. The European Commission’s obligations guidance also keeps pushing data protection by design and by default, which means privacy review belongs in release work, not only in a one-time policy pass. And if the popup introduces high-risk profiling or another high-risk processing branch, the EDPB’s 2026 DPIA template is another signal that regulators still expect structured assessment rather than vague reassurance.
That means the proof pack for website popups should include:
- the live popup copy and fields;
- the linked privacy or notice text;
- the storage and network behavior under reject, accept, and later withdrawal;
- the downstream vendor path;
- the date the popup or connected campaign changed afterward.
If you cannot reconstruct what the popup said and did at go-live, the next audit or complaint will be much harder than it needs to be.
A practical website popups review for this week
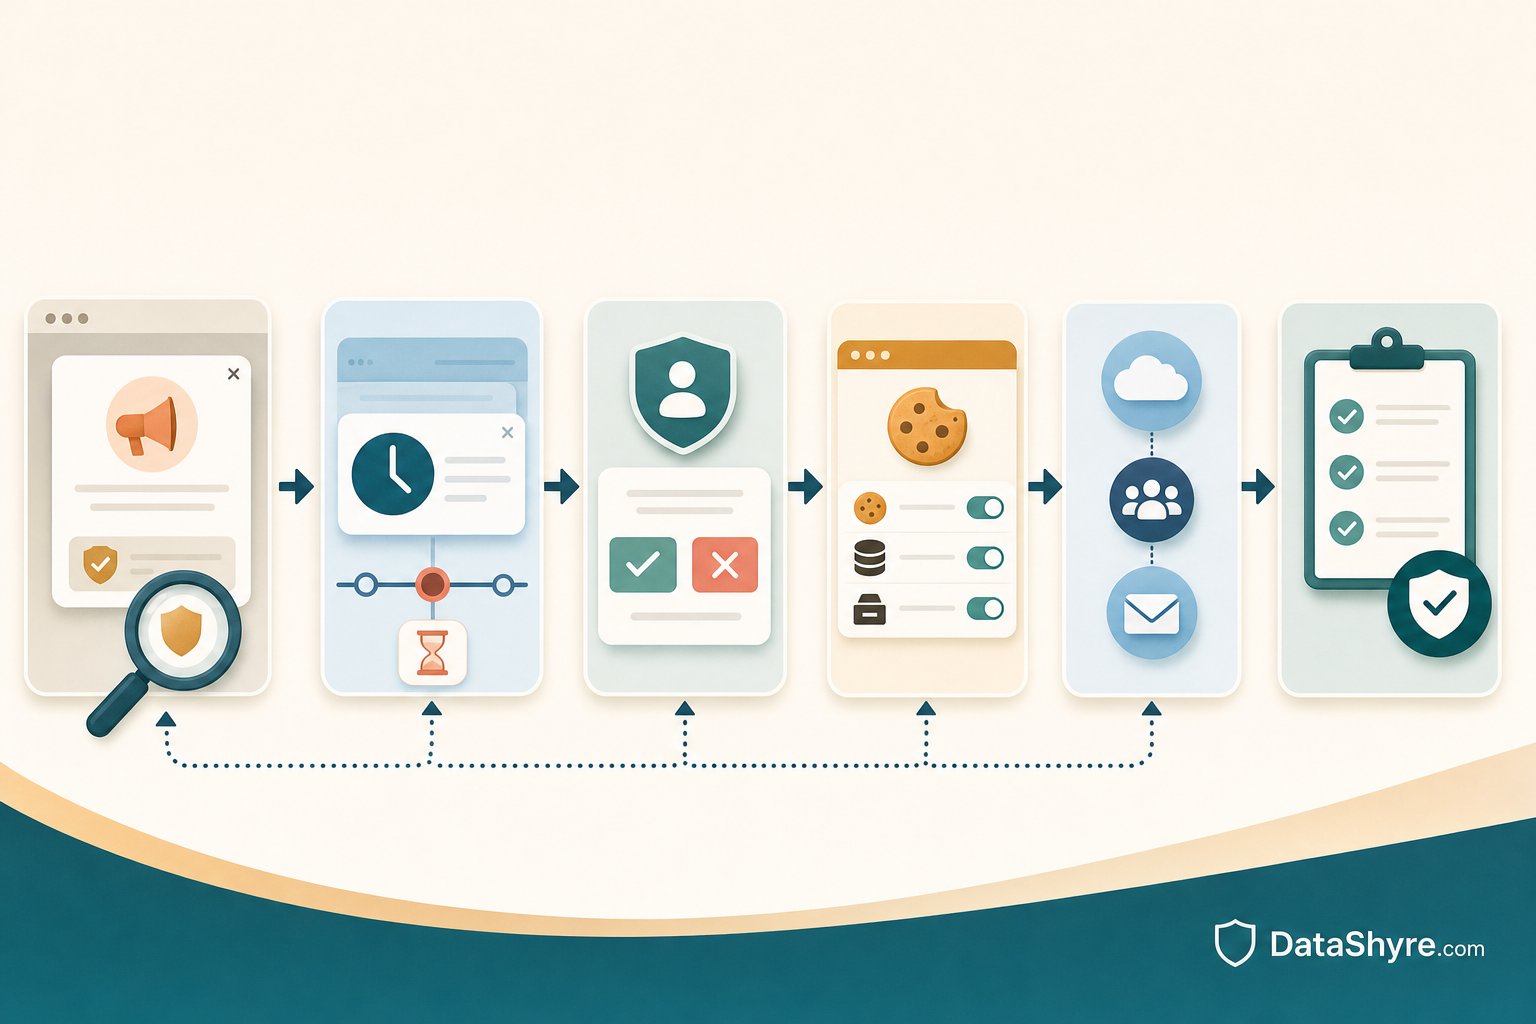
If I were auditing website popups today, I would use this order:
- classify the popup by purpose before touching the copy;
- test whether privacy information appears at or before collection;
- inspect cookies, storage, scripts, and network requests before interaction;
- compare the privacy-protective path with the yes path on desktop and mobile;
- confirm the lawful basis and follow-up use match the wording;
- trace the data through every downstream vendor and workflow;
- save evidence and re-test after changes.
That sequence usually reveals much more truth than another design review in Figma.
FAQ
Are website popups automatically a consent issue?
No. Some website popups are asking for consent, but others are giving notice or starting a form flow that depends on a different lawful basis. You have to classify the job first.
If a website popup only collects an email address, is the risk low?
Not necessarily. The risk depends on the purpose, the disclosure, the storage behavior, the downstream vendor chain, and whether rights requests can still be honored later.
Is a popup privacy review mostly about the text on the screen?
No. The text matters, but the runtime matters more. Storage, tags, scripts, vendor handoffs, and later withdrawal behavior are often where the real problems appear.
Official sources used
- European Data Protection Board, CEF 2026 on transparency and information obligations
- European Commission, Application of the GDPR
- European Commission, Legal grounds for processing data
- European Commission, Obligations under the GDPR
- European Commission, Information for individuals
- European Data Protection Board, Data controller or data processor
- European Data Protection Board, Data protection impact assessment
- European Data Protection Board, Enhancing compliance and consistency: EDPB adopts DPIA template
- ICO, Guidance on the use of storage and access technologies
- ICO, How do we manage consent in practice?
- California Privacy Protection Agency, What General Notices Are Required By The CCPA?
- California Privacy Protection Agency, CCPA Regulations effective January 1, 2026