

Website Consent Management in 2026: 7 Live Checks Before You Trust the Banner
If you are reviewing website consent management in 2026, the fastest mistake is assuming the website problem begins and ends with the banner.
It does not. A website consent setup has to connect what the visitor sees, what the region requires, what scripts and embeds actually do, and what evidence your team can still produce after the next release. Plenty of sites still look compliant from the front end while optional measurement, ad tech, or embedded tools begin working too early underneath.
If you want the closest companion reads first, start with our guides to consent management platform, consent management system, and cookie consent requirements. This page is narrower. It is the seven-check review I would use this week before trusting website consent management on a live property.
What website consent management really has to control
A useful website consent management program has to govern more than a pop-up.
On a real site, the consent layer usually sits between:
- the notice or preference center a person interacts with;
- the region logic that decides which rule path applies;
- the scripts, tags, pixels, SDK bridges, and embeds that collect or activate data; and
- the records that explain what happened later.
That definition matters because a polished banner alone is not a working website control.
1. Start with the site inventory, not the banner copy
The first serious test for website consent management is whether your team knows everything the site can load before you even discuss button labels.
The European Commission still says consent has to be freely given, informed, specific, and based on a clear affirmative act, and that the information should use “clear and plain language.” The ICO’s final storage-and-access-technologies guidance, published on April 29, 2026, also keeps the scope broader than old cookie lists. It covers cookies, scripts, tracking pixels, fingerprinting, and similar technologies used to store information or gain access to information on a device.
So the first review question is simple: can you name every technology your website consent management setup is supposed to control?
That usually includes:
- analytics and advertising tags;
- tag-manager rules;
- chat, video, booking, and form embeds;
- A/B testing and personalization scripts;
- downstream sharing paths tied to website activity.
If the inventory is incomplete, the banner is already ahead of the real control.
2. Separate regional branches instead of forcing one website flow
Weak website consent management often collapses different legal and operational models into one generic website experience.
That is where teams get into trouble. For EU and UK traffic, the live website question often starts with whether optional technologies remain off until valid consent exists. For California traffic, the path may turn on opt-out rights, sale or sharing logic, and browser-based privacy signals. California’s Department of Justice still describes Global Privacy Control as a “stop selling or sharing my data switch” and says covered businesses must honor it as a valid consumer request.
So a credible website consent management review should verify that:
- EU or UK traffic can follow a prior-consent path where required;
- California traffic can follow the right opt-out and GPC path where applicable;
- website copy, controls, and behavior stay aligned inside each branch; and
- your team is not pretending one button pattern solves every jurisdiction equally well.
One website can serve several regions. One consent flow should not flatten the obligations until they stop making sense.
3. Make categories and purposes specific enough to mean something
This is the middle layer where website consent management usually becomes either practical or misleading.
Categories like analytics, advertising, preferences, and necessary only help if they map to real website behavior. The European Commission’s guidance still points back to specific, informed consent, and the ICO’s 2026 materials explicitly ask practical questions about whether the same storage or access technology is being used for multiple purposes.
That means the website review should go beyond the label shown on screen and ask:
- which scripts or vendors sit inside each category;
- what exact purpose each one serves;
- whether one tool is quietly doing more than one job;
- what happens to each tool on reject, accept, and later withdrawal.
If the category list looks tidy but your team cannot explain what actually fires under each state, the website consent management layer is decorative.
4. Treat runtime enforcement as the real product
This is the technical center of website consent management.
Google’s current consent-mode setup guidance still says the default consent state should be set on every page before commands that send measurement data, and that consent updates should be tracked on the page where they occur before any page transition. That is a website behavior requirement, not just a configuration note.
So when you test website consent management, check at least these live states:
- first visit with no saved choice;
- explicit reject;
- explicit accept;
- later withdrawal or preference change; and
- another page load or route change after each state.
Then compare the promise on screen with the actual network and tag behavior. If optional website activity starts first and the CMP catches up later, the stack is not ready.
5. Keep the Google and publisher branch separate when it applies
Some website consent management reviews stop once the banner talks to analytics.
That is not always enough. If the website depends on Google publisher products such as AdSense, Ad Manager, or AdMob for affected traffic, Google’s current publisher guidance still requires a Google-certified CMP integrated with the IAB Transparency and Consent Framework when serving personalized ads to users in the EEA, UK, or Switzerland.
So if ads matter, review two separate questions:
- does the website respect the user choice technically; and
- does the website satisfy Google’s product-specific publisher requirement where it applies.
Those are related, but they are not the same check. A site can pass a tag test and still fail a publisher requirement. The reverse can also happen.
6. Make refusal and withdrawal genuinely easy on the website
The interface still matters because it is where the website asks for trust.
The European Commission still says withdrawing consent should be “as easy to use as giving consent.” CNIL continues to say rejecting cookies should be “just as easy as accepting them.” The CPPA’s enforcement advisory captures the broader design lesson cleanly: “Dark patterns aren’t about intent, they’re about effect.”
For website consent management, that means checking whether:
Reject allis visible where prior consent is expected;- refusal is usable on mobile as well as desktop;
- a person can reopen settings later without hunting through the site; and
- the website actually changes what it loads or shares after withdrawal.
If the website makes acceptance immediate but hides refusal or later change, the risk is built into the experience itself.
7. Keep evidence that reconstructs what the website actually did
Consent records matter most when they can explain real website behavior.
A durable website consent management setup should usually let you reconstruct:
- which interface version was shown;
- which categories or purposes were offered;
- what the person chose and when;
- which regional rule set applied; and
- what technical state followed from that choice.
That proof becomes much stronger when it can be compared with browser behavior, logs, or tag-debug traces instead of existing only as a database field that says accepted or rejected.
A short live review sequence for this week
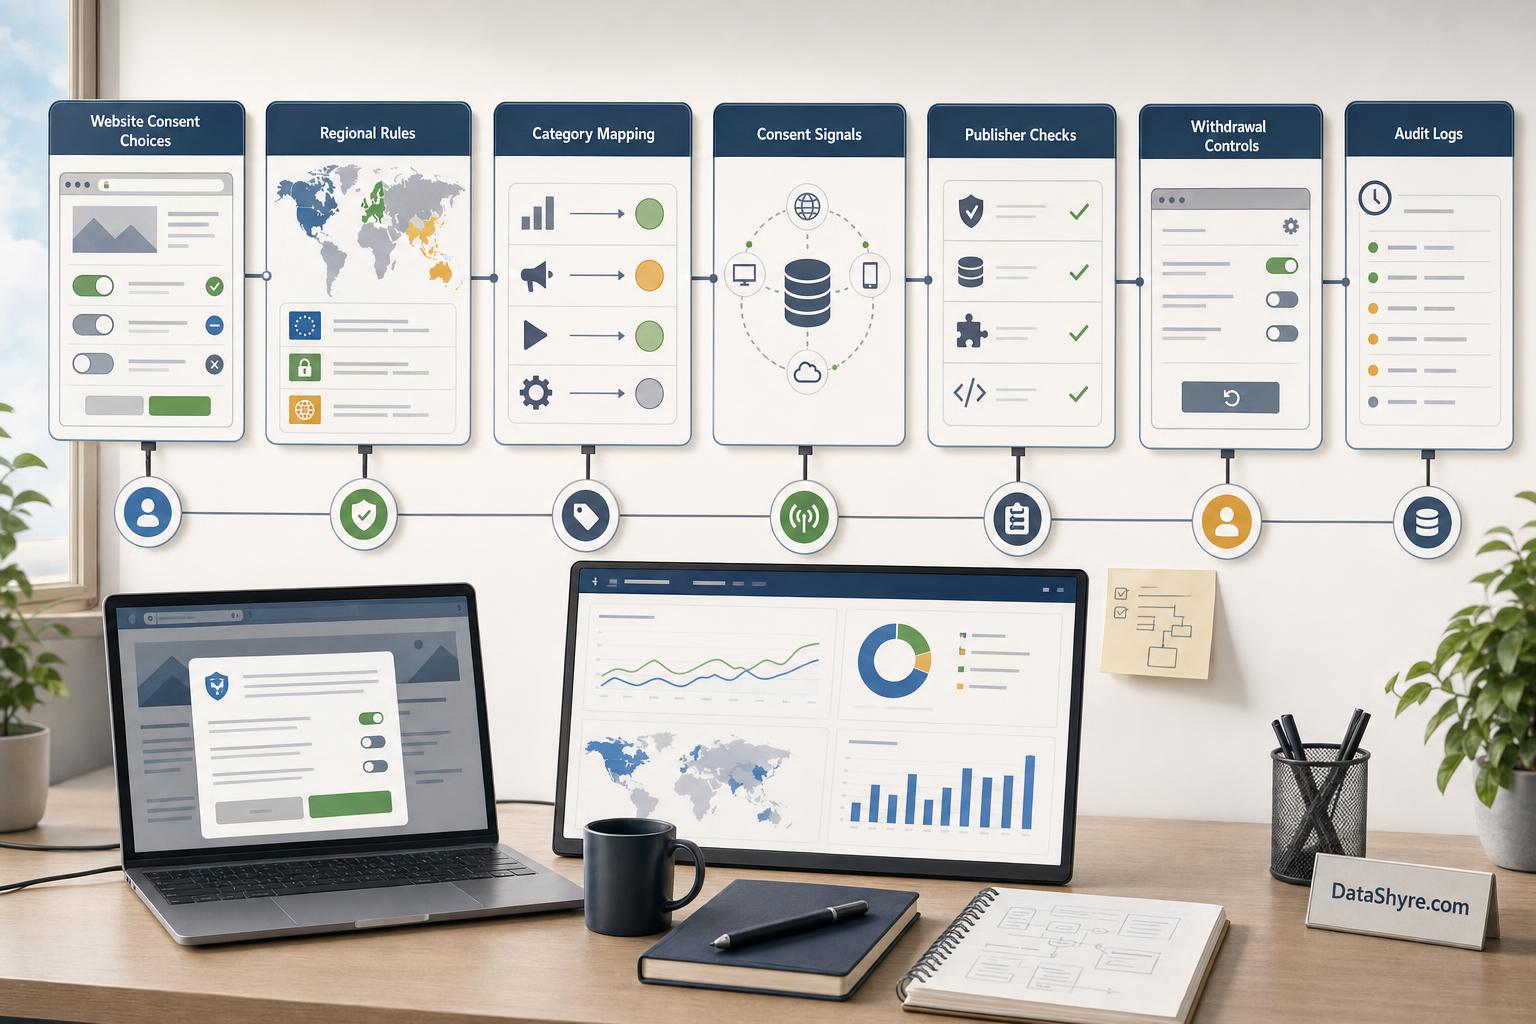
If I were pressure-testing website consent management today, I would work in this order:
- inventory every website technology the consent layer claims to govern;
- test each regional branch separately;
- check the category-to-technology map;
- inspect first-load runtime behavior before any choice;
- test reject, accept, and later withdrawal;
- verify the separate Google publisher branch if ad monetization makes it relevant; and
- compare saved records with real browser behavior.
That usually tells you more than another round of banner-copy revisions.
Bottom line
In 2026, strong website consent management is not the website with the prettiest banner.
It is the website where notices, region logic, technical enforcement, withdrawal, and evidence still match one another after the next deployment. If the stack can do that consistently, the website control is real. If not, the interface may be finished while the website consent management program is not.
Sources
- European Commission, Legal grounds for processing data: https://commission.europa.eu/law/law-topic/data-protection/information-business-and-organisations/legal-grounds-processing-data_en
- European Commission, Information for individuals: https://commission.europa.eu/law/law-topic/data-protection/information-individuals_en
- UK ICO, Final storage and access technologies guidance published: https://ico.org.uk/about-the-ico/media-centre/news-and-blogs/2026/04/final-storage-and-access-technologies-guidance-published/
- UK ICO, Guidance on the use of storage and access technologies: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/
- California Department of Justice, Global Privacy Control: https://oag.ca.gov/privacy/ccpa/gpc
- California Privacy Protection Agency, Enforcement Advisory on Dark Patterns: https://cppa.ca.gov/announcements/2024/20240904.html
- CNIL, Dark Patterns in Cookie Banners: https://www.cnil.fr/en/dark-patterns-cookie-banners-cnil-issues-formal-notice-website-publishers
- Google for Developers, Set up consent mode on websites: https://developers.google.com/tag-platform/security/guides/consent
- Google AdSense Help, Google consent management requirements for serving ads in the EEA, the UK, and Switzerland: https://support.google.com/adsense/answer/13554116
—
Published: October 18, 2026. Updated using current official European Commission, ICO, California DOJ, CPPA, CNIL, and Google materials available at publication time.