
Online Privacy Policy in 2026: 7 Checks Before You Publish or Update It
If you are searching for an online privacy policy on November 5, 2026, the fastest useful answer is this: it is not just a footer page anymore.
It is the public explanation layer for what your site, app, forms, trackers, vendors, and rights workflows are actually doing.
That means a working online privacy policy cannot be judged only by whether the page exists.
It has to match reality.
Current official guidance still pushes in that direction. California’s Department of Justice says privacy policies should be posted on a website homepage, or on the download or landing page of a mobile application, and says the policy should be “updated at least once a year.” The same CCPA guidance says the notice at collection must link to the privacy policy so people can get a fuller description of privacy practices and rights. The GDPR and the ICO’s current transparency guidance still push toward clear, accessible information about who is processing the data, why, who receives it, how long it is kept, and what rights people have. The FTC’s business guidance adds the enforcement reality in one plain rule: if your company makes privacy promises, it must “live up to those claims.”
If you want nearby context first, start with our guides to privacy policy template, privacy policy for website, and website privacy policy template. This page stays focused on the moment an online privacy policy moves from generic copy into a live website or app.
If your team is trying to connect policy text to the systems behind it, DataShyre can help. Our work around data mapping, consent management, and DSR automation is built for exactly that handoff. If you want the short version, book a demo.
1. Start the online privacy policy with the live collection map
The most common online privacy policy mistake happens before anyone edits the first sentence.
Teams start with a template instead of the live collection map.
That usually produces vague language while the real environment is collecting personal data through:
- contact or demo forms;
- newsletter signups;
- account creation and login;
- checkout or billing flows;
- analytics, pixels, and embedded tools;
- support widgets or scheduling tools; and
- mobile-app or app-download journeys.
California DOJ’s privacy-policy guidance still frames the practical questions the page should answer: what information is collected, how it is collected, why it is collected, how it is used, who gets access, and who is accountable for privacy practices. The ICO’s drafting guidance points the same way from a different angle by emphasizing clear information adapted to the audience and the context.
So before you draft or revise an online privacy policy, build a current map of:
- what categories of personal data you collect;
- where each category is collected;
- why each category is used;
- which teams or vendors receive it;
- how long it is kept; and
- what rights or controls can change the downstream use.
The map is the source of truth. The policy is the explanation layer.
2. Make the policy answer the questions regulators still care about
A useful online privacy policy should let a normal person understand what is happening without forcing them to decode legal filler.
California DOJ says a privacy policy gives a broad picture of a business’s online and offline practices for the collection, use, sharing, and sale of personal information, and that it must include information on privacy rights and how to exercise them. GDPR Articles 12 to 14 and the ICO’s current right-to-be-informed guidance still push toward the same operational outcome: concise and accessible notice about the controller, purposes, recipients, retention, rights, and other material facts.
So a working online privacy policy usually needs clear sections for:
- who operates the site or app and how to contact them;
- what categories of personal data are collected;
- where that data comes from;
- why each category is used;
- the legal basis where GDPR or UK GDPR applies;
- who receives the data or what categories of recipients receive it;
- how long data is retained or how the period is decided;
- what rights people have; and
- how to submit a rights or privacy request.
If those blocks are missing, the online privacy policy is usually too thin for 2026.
3. Treat forms, app screens, and the main policy as one system
One reason an online privacy policy fails in production is that the page is drafted in isolation from the places where people actually provide the data.
California DOJ’s current CCPA guidance says a notice at collection must be provided at or before the point where personal information is collected and must include a link to the privacy policy. The same page gives examples that include a website homepage, the page where a person places an order or enters information, and a mobile-app settings menu.
That means your privacy disclosure layer may need both:
- the main online privacy policy page; and
- shorter just-in-time notices near forms, signup flows, checkout, app registration, or other collection points.
The ICO’s current guidance makes the same practical point by telling organizations to make privacy information easy to access and adapt it to the method of collection.
So instead of asking only whether the policy page exists, ask whether the places where data collection actually starts give people enough context at the right moment.
4. Give tracking, cookies, and third-party tools their own honest section
Many weak online privacy policy pages still bury tracking disclosures inside generic language about usage data.
That is rarely enough.
If the site or app uses cookies or similar technologies, the policy should explain in plain language:
- what technologies are used;
- whether they are necessary, analytics, advertising, or embedded-third-party tools;
- whether another party receives information through them;
- how consent, opt-out, or browser-based controls affect them; and
- where a person can review or change those settings later.
This does not mean turning the page into a giant tracker spreadsheet.
It does mean the online privacy policy should not pretend the business only collects data through visible forms if the live environment is also running analytics tags, video embeds, chat widgets, measurement tools, or ad-tech scripts.
If this part is the one breaking down, our privacy policy for website and website privacy policy template guides are the more focused next reads.
5. Make the rights section operational, not decorative
This is where many polished online privacy policy pages still fail.
Listing rights is easy. Showing a person how to use them is harder.
California DOJ’s CCPA guidance says the privacy policy must include information on consumer privacy rights and how to exercise them. Its FAQ also points people back to the privacy policy for instructions on how to submit deletion and correction requests. On the GDPR and UK GDPR side, the right-to-be-informed guidance still expects organizations to explain the relevant rights clearly and accessibly.
That means a practical online privacy policy should explain:
- which rights apply in the relevant jurisdictions;
- how a person submits a request;
- whether there is an account-settings path as well as a public path;
- how opt-out or privacy settings appear on the site or in the app;
- whether browser-based signals such as Global Privacy Control are honored where applicable; and
- where the person goes if the first path fails.
The policy should not stop at naming rights. It should point to real working routes.
6. Match the policy to real vendor behavior and privacy promises
A risky online privacy policy is often not the one with the fewest words.
It is the one that describes a business that no longer exists.
The FTC’s current business guidance says that if a company makes privacy promises, the FTC Act requires it to “live up to those claims.” California’s privacy enforcement page shows the same pattern from another angle. In the Healthline Media settlement summary, the state says Healthline had to maintain accurate online disclosures and privacy policy.
That is the real review standard for an online privacy policy in 2026:
- compare the page against the live vendor stack;
- compare it against the tracking and sharing that really happen;
- compare it against app behavior and settings paths;
- compare it against the rights workflow the person actually experiences.
Generic lines like trusted partners may receive information are not very useful. Categories such as payment processors, cloud hosting providers, customer-support tools, analytics providers, and advertising partners are much more informative when they match reality.
7. Treat privacy-policy updates as product-change work, not a yearly chore
California DOJ says the policy should be updated at least once a year.
That is a floor, not a strategy.
The ICO’s current drafting guidance says privacy information should be kept under review and updated before a new purpose begins. That is the more useful operating model.
So a better online privacy policy workflow is to review the page whenever:
- a new form or account field is launched;
- a new SDK, pixel, or embed goes live;
- a new processor or marketing vendor is onboarded;
- a retention rule changes;
- a new region or rights workflow is added; or
- the consent, opt-out, or settings path changes.
That is the difference between a document that is merely published and one that stays defensible.
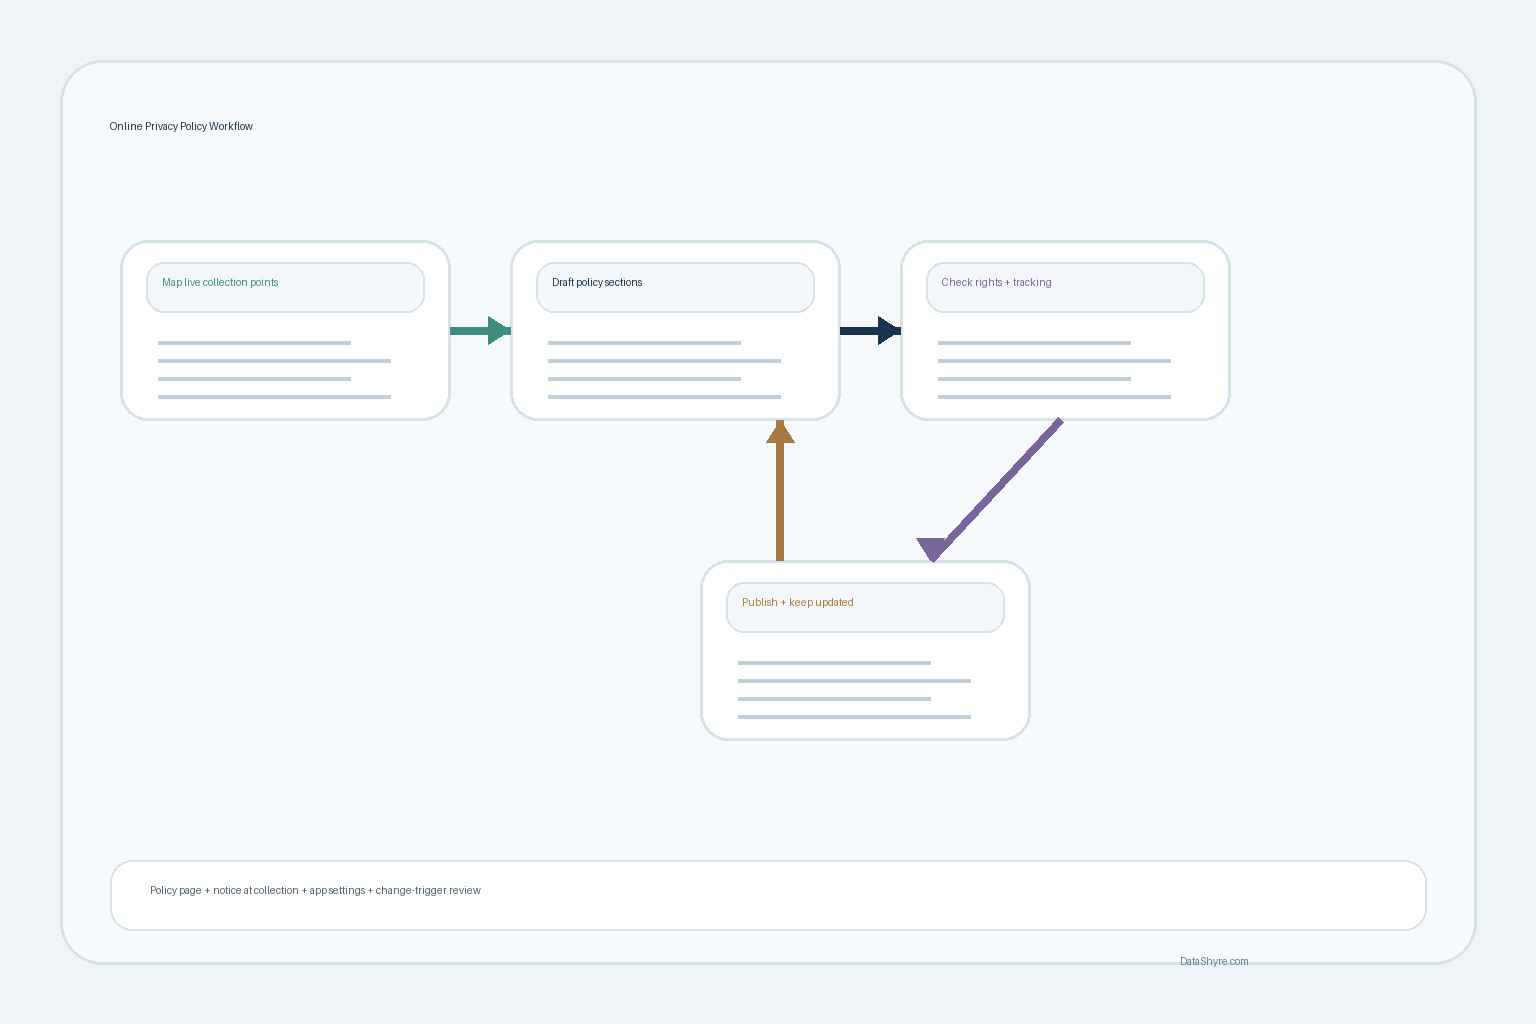
A practical 7-step review for this week
If I were approving an online privacy policy this week, I would use this order:
- map the real collection points and vendors first;
- fill the core sections for collection, purposes, recipients, retention, rights, and contacts;
- connect point-of-collection notices and app settings back to the fuller policy;
- add an honest branch for cookies, tracking, and third-party tools;
- test whether the rights and opt-out paths described in the policy actually work;
- compare the policy against the live site or app behavior; and
- tie future product or vendor changes to a required policy review.
That order produces a much stronger result than polishing legal language before anyone has checked the actual system.
FAQ
Is an online privacy policy the same thing as a website privacy policy?
Not always. A website privacy policy is one common form of an online privacy policy, but the online version may also need to cover mobile-app download pages, app settings, and other digital collection points beyond the public website.
Is an online privacy policy enough on its own?
No. An online privacy policy is the disclosure layer. It does not replace consent controls, vendor governance, security, or rights-handling operations.
Can I reuse one online privacy policy across different sites or apps?
Only if the underlying collection, vendors, rights paths, and jurisdictions are meaningfully the same. The structure can be reused more easily than the actual content.
Bottom line
The best online privacy policy in 2026 is not the one with the most clauses.
It is the one that matches the real collection points, explains tracking and sharing honestly, gives people workable rights paths, and gets updated before the next product change makes it false.
If your current page cannot do that, the real problem is not the copy.
It is the missing connection between the policy and the system it is supposed to describe.
Sources
- California Department of Justice, How to Read a Privacy Policy: https://oag.ca.gov/privacy/facts/online-privacy/privacy-policy
- California Department of Justice, California Consumer Privacy Act (updated August 28, 2026): https://oag.ca.gov/privacy/ccpa
- California Department of Justice, Privacy Enforcement Actions: https://oag.ca.gov/privacy/privacy-enforcement-actions
- EUR-Lex, Regulation (EU) 2016/679: https://eur-lex.europa.eu/eli/reg/2016/679/oj/eng/
- ICO, What privacy information should we provide?: https://ico.org.uk/for-organisations/uk-gdpr-guidance-and-resources/individual-rights/the-right-to-be-informed/what-privacy-information-should-we-provide/
- ICO, How should we draft our privacy information?: https://ico.org.uk/for-organisations/uk-gdpr-guidance-and-resources/individual-rights/the-right-to-be-informed/how-should-we-draft-our-privacy-information/
- Federal Trade Commission, Privacy and Security: https://www.ftc.gov/business-guidance/privacy-security