
California Privacy Law Delete Data in 2026: What Businesses Must Do After a Delete Request
If you are searching california privacy law delete data on October 15, 2026, the real question is usually not whether California has a deletion right. It does. The harder question is what has to happen after the request arrives: how consumers can submit it, how quickly the business has to respond, what can be denied or retained under an exception, and when the newer data-broker workflow changes the analysis.
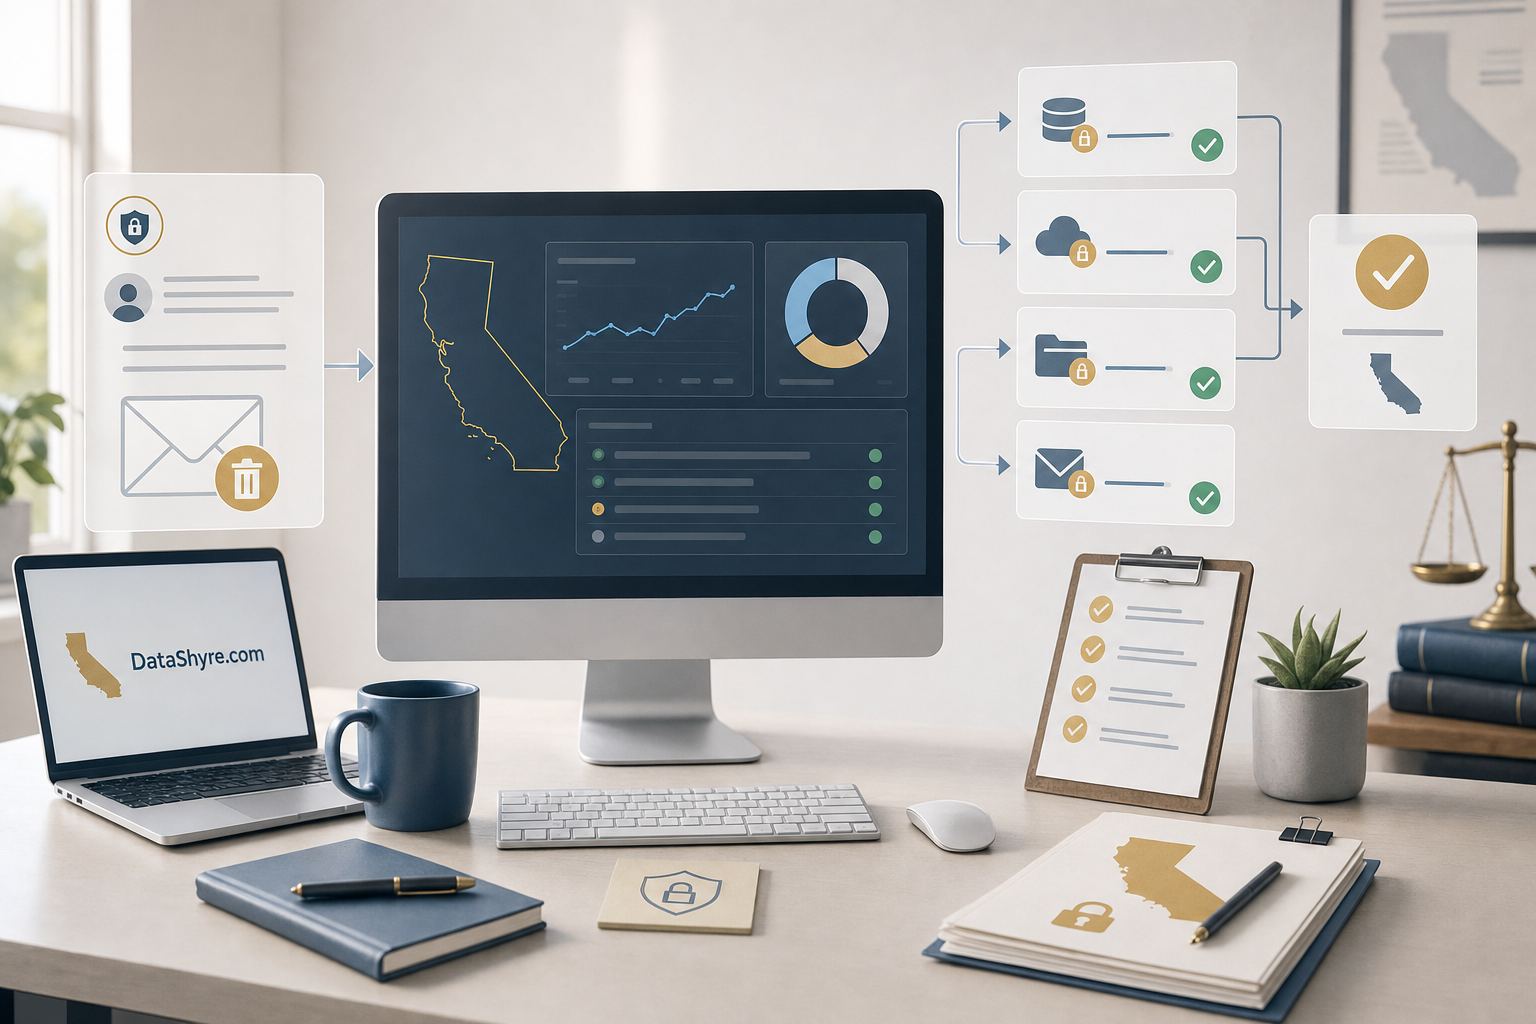
That last part matters more now than it did earlier this year. California’s Delete Request and Opt-out Platform (DROP) has been open to consumers since January 2026, and data brokers have been required to access it and process deletion requests since August 1, 2026. So the phrase california privacy law delete data now points to two operating tracks: the ordinary CCPA delete workflow for covered businesses and the statewide DROP workflow for registered data brokers.
If you want the adjacent California context first, start with our guides to California consumer privacy, California data privacy protection act, and CCPA cookie consent. This page is narrower. It is the practical answer to california privacy law delete data after a request is already in motion.
1. Know which delete track you are actually on
The first mistake with california privacy law delete data is treating every deletion request as the same workflow.
For most companies, the baseline is still the CCPA, as amended, and the current CPPA regulations effective January 1, 2026. That is the path consumers use when they ask a covered business to delete personal information the business collected from them.
For data brokers, there is now an extra branch. The CPPA says the accessible deletion mechanism lets a consumer send a “single verifiable request” directing every registered data broker that maintains that consumer’s personal information to delete it. The agency’s data-broker guidance also says that, beginning August 1, 2026, data brokers must access the system at least once every 45 days and process deletion requests.
So before a team says yes or no to a delete request, it should answer one basic question: are we operating as a covered business, a registered data broker, or both?
2. Make sure consumers can use the right request channels
California’s current materials are still explicit about request intake.
The CPPA FAQ says businesses must generally designate at least two methods for consumers to submit delete, correct, or know requests. One of those methods must be a toll-free number and, if the business has a website, one method must be through the website. If the business operates exclusively online, it only needs to provide an email address for those requests.
The official CCPA FAQ from the California Department of Justice says the same thing in plainer language: consumers should use the business’s designated methods, and those methods may be different from ordinary customer support channels.
That sounds simple, but California’s enforcement examples show how often this still breaks. The Attorney General’s published case examples include businesses that did not tell consumers how to submit requests to know and delete, gave incorrect instructions, or failed to offer working request methods at all.
For california privacy law delete data, that means the first live test is not your policy text. It is whether the request paths are obvious, working, and mapped to a real process.
3. Understand what the delete right actually reaches
This is where teams often overstate or understate the law.
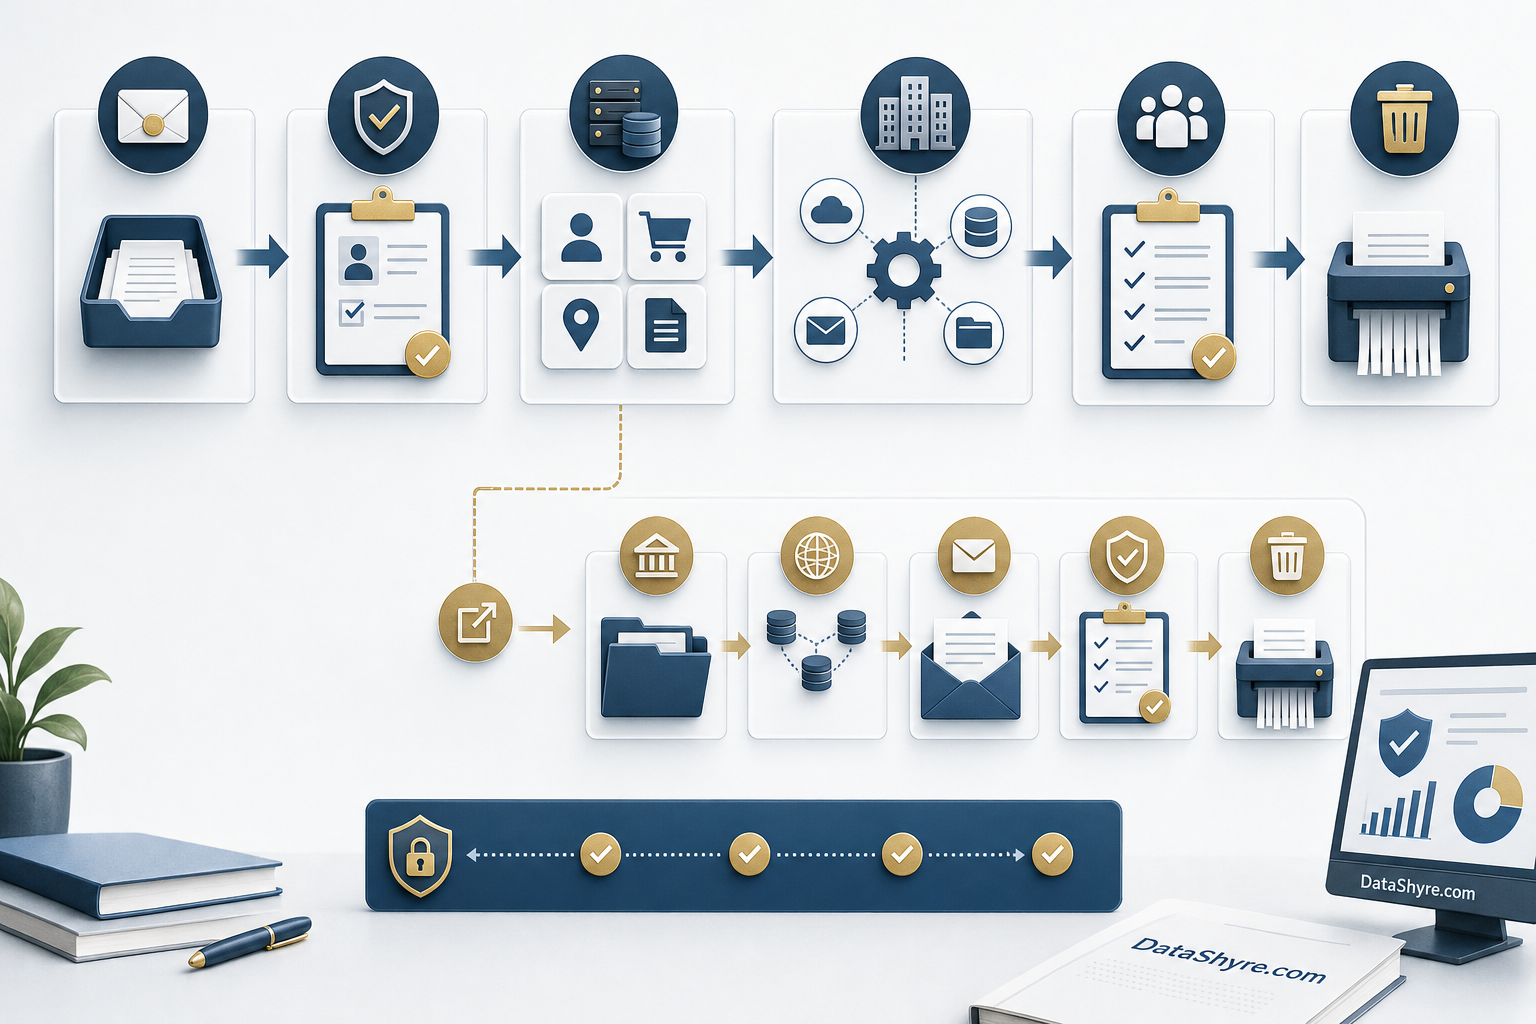
California’s delete right is not just a promise to remove one record from one app. The current CPPA regulations say a business must comply with a verified delete request by permanently erasing the information, deidentifying it, or aggregating it. The same regulations say the business must notify its service providers or contractors to delete the consumer’s personal information collected under their written contract, and must notify third parties to whom it sold or shared the personal information to delete it too unless doing so is impossible or would involve disproportionate effort.
That is a much broader operational duty than many teams expect. It is not only CRM data. It can reach marketing platforms, form vendors, audience tools, analytics-linked identifiers, support systems, and downstream partners depending on what the business actually did with the information.
At the same time, the right is not unlimited. California’s FAQs and regulations still point to exceptions and exempt categories of information. So a business should avoid two opposite mistakes:
- treating every delete request as a total wipe everywhere no matter what;
- treating the right as merely cosmetic because some exceptions exist.
The operational work is in the system map.
4. Watch the deadline clock from day one
This is one of the clearest areas of California’s current rules.
The CPPA FAQ and the 2026-effective regulations say a business must confirm receipt of a delete request within 10 business days and must respond within 45 calendar days. If reasonably necessary, the business may take up to an additional 45 calendar days, for a total of 90 days, as long as it gives notice and explains the delay.
That timing matters because delete requests often stall in real organizations long before any legal review happens. A request arrives through a web form, lands in a support queue, sits unclassified for a week, and only later reaches privacy or engineering. By then, part of the response window is already gone.
If you are reviewing california privacy law delete data this quarter, treat the ten-day acknowledgement as a process health check. When that slips, the rest of the workflow usually slips too.
5. Verification cannot become an excuse for friction
Businesses do not have to process every delete request blindly. California’s official CCPA materials still say businesses must verify that the person making a delete request is the consumer about whom the business has personal information.
But California’s enforcement materials also show the boundary. The Attorney General’s case examples describe companies that required excessive steps, broken paths, or account creation to exercise CCPA rights. The CCPA FAQ says businesses cannot make consumers create an account just to submit a deletion request, even though a business may require an existing account holder to submit through that account.
So for california privacy law delete data, the live question is whether verification is proportional:
- enough to avoid deleting the wrong person’s data;
- not so heavy that ordinary consumers give up;
- matched to the sensitivity of the request and the data involved.
That is especially important when a company already has enough information to locate the record without creating a longer obstacle course.
6. Data brokers now have a separate 45-day deletion duty
This is the newest part of the workflow and the part many general privacy checklists still blur.
The CPPA’s November 13, 2025 announcement said the Delete Act regulations took effect on January 1, 2026 and that California consumers could begin using DROP in January 2026. It also said that, starting August 1, 2026, data brokers must access DROP at least every 45 days to retrieve and process consumer deletion requests.
The statute and the CPPA announcement add another detail that matters operationally: when a consumer’s information matches the broker’s records, the data broker must delete all associated personal data, “including inferences,” unless a legal exemption applies. The broker must also report the status of the deletion request in DROP within 45 days of retrieving it.
That makes california privacy law delete data materially different in late 2026 than it was even a year ago. For registered data brokers, the state has moved deletion from a largely bilateral process into a recurring platform duty.
7. Use exceptions carefully and document them well
California still allows businesses and data brokers to retain information in some circumstances, but official materials do not support vague blanket denials.
The DROP statute cross-references the familiar CCPA exception structure, and the CPPA FAQ still notes that businesses may deny deletion requests when the information falls under an exception, cannot be verified, or is otherwise exempt from the CCPA.
That means a mature california privacy law delete data workflow should do two things at once:
- identify what can be deleted across active systems and downstream partners;
- document the specific reason why a retained category stays in place.
If the company cannot explain why information was kept, that is usually a process weakness rather than a real exception analysis.
A practical review sequence for 2026
If I were auditing california privacy law delete data on a live site or in a live privacy program this week, I would use this order:
- identify whether the request falls under the ordinary CCPA business workflow, the DROP data-broker workflow, or both;
- test every designated request method listed in the privacy policy;
- confirm the acknowledgement process can happen inside 10 business days;
- map all internal systems, service providers, contractors, and third parties touched by the relevant data;
- check whether verification is reasonable rather than punitive;
- verify the business can complete or deny the request within 45 days, or properly extend to 90;
- for data brokers, confirm DROP retrieval, matching, deletion, and status reporting are happening on the now-live 45-day cadence.
That sequence answers the real search intent behind california privacy law delete data better than a generic overview of rights.
Bottom line
In 2026, california privacy law delete data is not just a policy-page topic. It is a live operating workflow.
For covered businesses, the core duties are clear: publish working request methods, verify reasonably, respond on time, delete across your own systems and required downstream relationships, and document any exception you rely on. For data brokers, the Delete Act adds a second live track through DROP, with recurring access and processing duties that have already been in force since August 1, 2026.
If your organization still treats delete requests as an inbox chore instead of a mapped system response, California’s current rules say that is not enough anymore.
Sources
- California Privacy Protection Agency FAQ
- California Privacy Protection Agency: Law & Regulations
- California Privacy Protection Agency: Information for Data Brokers
- California Privacy Protection Agency: Delete Act announcement
- California Privacy Protection Agency: CCPA statute and regulations effective January 1, 2026
- California Privacy Protection Agency: Delete Act statute effective January 1, 2026
- California Department of Justice: California Consumer Privacy Act
- California Department of Justice: CCPA Enforcement Case Examples
—
Published: October 15, 2026. Updated using current official California regulator, government, and statutory materials available at publication time.