

GDPR Consent Form: Best Practices & Implementation 2026
Published Keyword: consent management platform
Executive Summary
With GDPR evolving throughout 2026, organizations must ensure their consent management platforms meet strict legal requirements for explicit, granular, and easily withdrawable consent. This post focuses on implementing effective consent management platforms that comply with GDPR Article 7 and related regulations.
Why a Robust Consent Management Platform Matters
- Legal Compliance – GDPR requires prior, explicit consent before processing personal data, with consent management platforms serving as the central mechanism for obtaining and tracking this consent.
- User Trust – Transparent consent processes build trust and improve user engagement rates.
- Enforcement Readiness – Proper documentation through consent management platforms protects against fines from data protection authorities.
- Operational Efficiency – Centralized consent management reduces complexity and ensures consistent application across digital properties.
Key GDPR Requirements for Consent Management Platforms
Based on current 2026 guidelines from official sources:
| Requirement | Description | Source | |————-|————-|———| | Freely Given | Consent must be voluntary without coercion or negative consequences for refusal | GDPR Article 4(11) | | Specific & Granular | Separate consent for different processing purposes; users must be able to consent to some purposes while refusing others | GDPR Recital 32 | | Informed | Clear information about data controller, types of data, purposes, storage duration, and right to withdraw | GDPR Articles 13-14 | | Unambiguous | Clear affirmative action required; pre-ticked boxes or inactivity do not constitute consent | GDPR Recital 32 | | Easy Withdrawal | Withdrawing consent must be as easy as giving it, accessible at any time | GDPR Article 7(3) | | Proof of Consent | Platforms must maintain records demonstrating when and how consent was obtained | GDPR Article 7(1) | | Children’s Protection | For children under 16 (or lower age set by Member States), parental consent required for information society services | GDPR Article 8 |
Implementation Best Practices
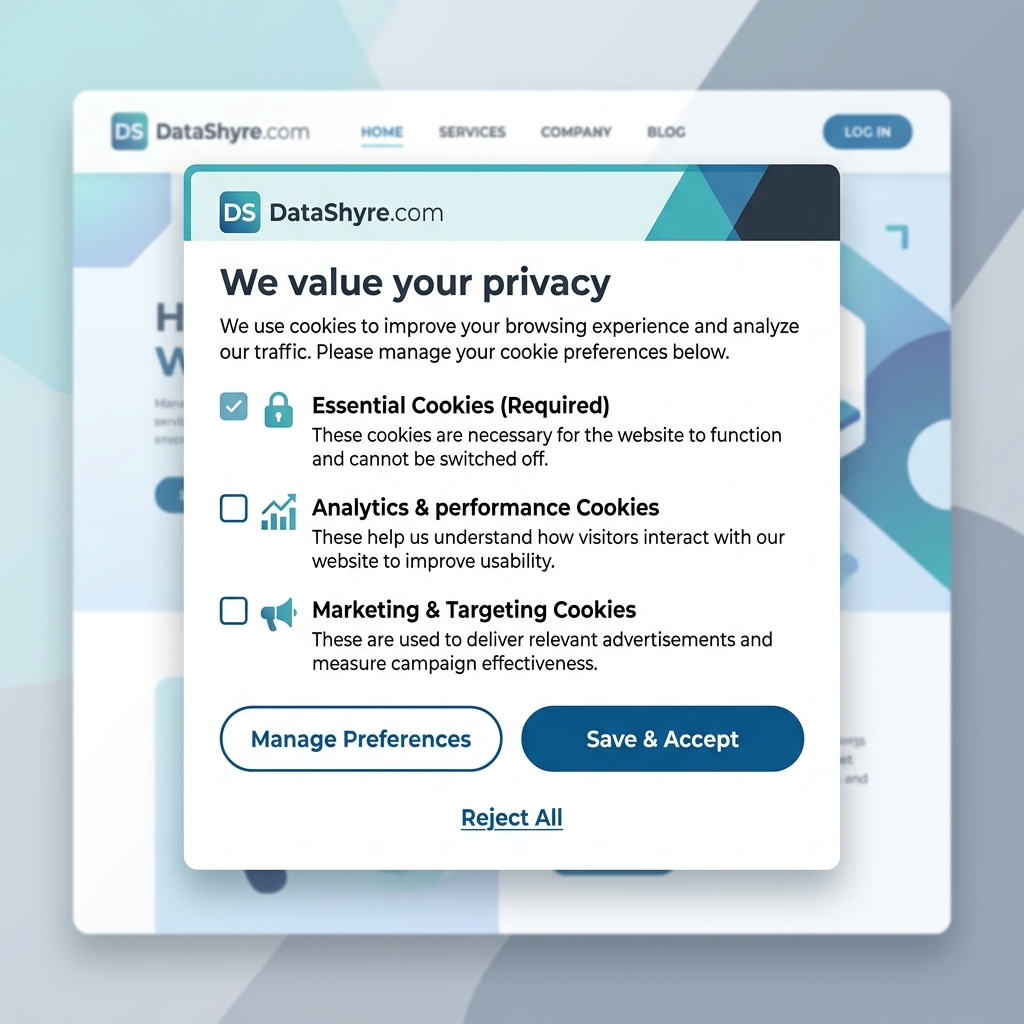
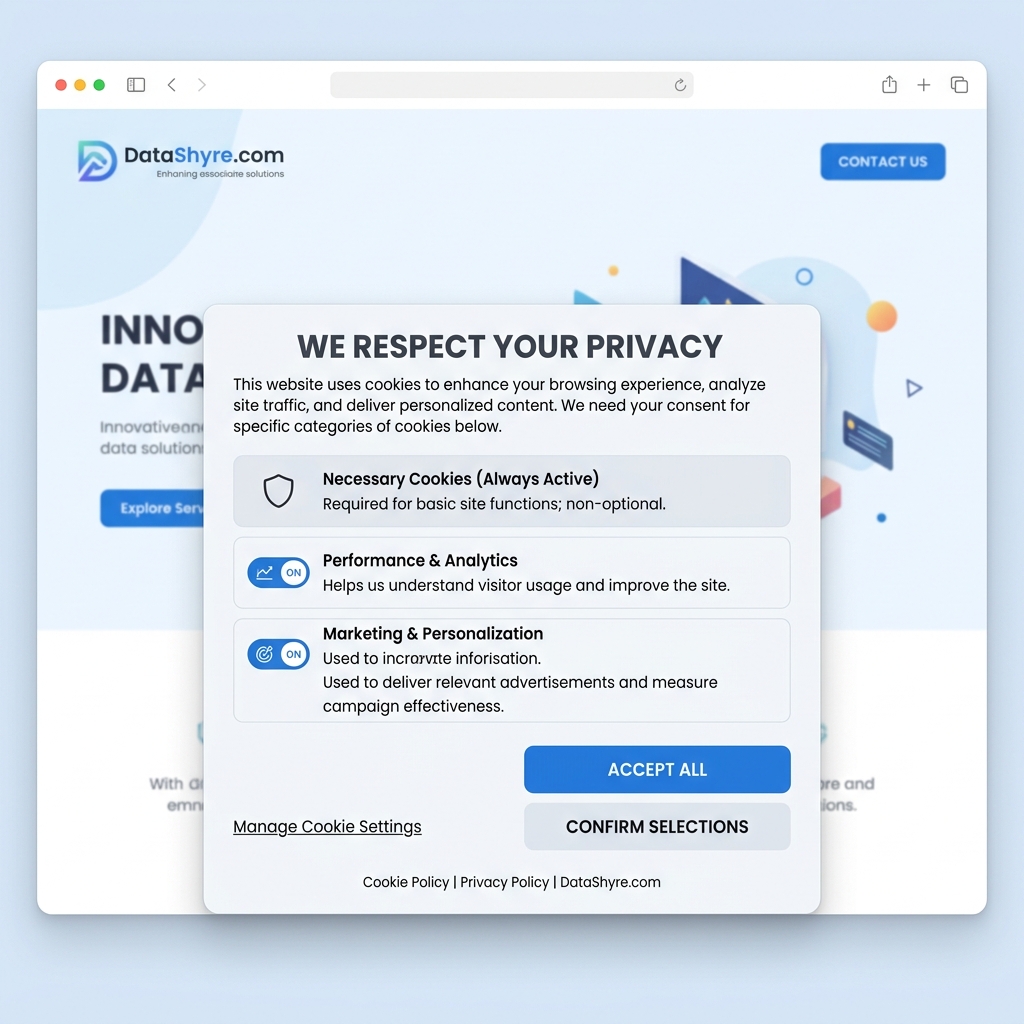
- Implement Granular Controls – Allow users to accept/reject different categories (essential, analytics, marketing, advertising) separately
- Use Clear, Plain Language – Avoid legalese; ensure consent requests are easily understandable
- Provide Equal Prominence – Make “Accept All” and “Reject All” buttons equally visible
- Enable Easy Withdrawal – Include persistent consent management icon/link accessible from all pages
- Maintain Consent Logs – Store timestamp, version of consent request, and user choices for audit purposes
- Regular Reviews – Update consent mechanisms to align with evolving guidelines and regulations
- Geographic Considerations – Account for Member State variations in GDPR implementation, particularly regarding children’s age thresholds
Related Posts
- GDPR Cookie Consent Examples – Practical implementation patterns
- CCPA Consent Requirements – State‑level compliance nuances
- GDPR Compliance Checklist – Step‑by‑step implementation guide
Image Placeholders
Conclusion
A well-implemented consent management platform is essential for GDPR compliance in 2026. By prioritizing transparency, granular control, and easy withdrawal mechanisms, organizations can achieve regulatory compliance while building user trust and reducing enforcement risks.
Published: September 7, 2026