

GDPR Cookie Consent Examples in 2026: 7 Live Patterns That Still Hold Up
Most lists of gdpr cookie consent examples stop at screenshots. That is not enough anymore.
The examples worth copying in 2026 are the ones that survive a live review: the first layer offers a real yes-or-no choice, purposes are explained in plain language, withdrawal is easy later, and the tag behavior matches what the banner promises.
That direction is still visible in current official materials. The European Commission says consent requests must use “clear and plain language”, be tied to a specific purpose, and make withdrawal as easy as giving consent. The UK’s ICO finalized its storage-and-access-technologies guidance on April 29, 2026, and that guidance now reaches beyond classic cookies to tracking pixels, device fingerprinting, and similar technologies. France’s CNIL is still saying refusal should be “just as easy as accepting them.” And Google’s current consent guidance still expects teams to set defaults before measurement tags fire and to validate behavior with Tag Assistant.
If you want nearby context first, start with our guides to cookie consent requirements, cookie consent banner examples, and cookie consent Google Tag Manager. This version is narrower. It focuses on the seven GDPR-first patterns that still hold up when you test them on a live site this week.
1. A balanced first layer with accept, reject, and customize
The strongest gdpr cookie consent examples still start with the same simple move: a first layer that presents acceptance, refusal, and customization without forcing people into a maze just to say no.
That is the clearest practical reading of the European Commission’s consent guidance and CNIL’s banner enforcement. If Accept all is large and immediate while refusal is hidden as a low-contrast text link, the design is doing persuasion work that a valid consent flow should not rely on.
Copy this pattern:
Accept allReject allCustomize choices
All three should be immediately visible where prior consent is required.
2. Purpose-level categories that say what actually happens
Weak banners often use labels like Improve experience or Enhanced browsing because they sound harmless. Strong gdpr cookie consent examples do the opposite. They explain the real purpose at a level users can act on.
That usually means separating:
- strictly necessary technologies;
- analytics or measurement;
- advertising or remarketing;
- personalization or preference storage, if it is truly optional.
The European Commission’s current guidance still ties valid consent to specific purposes and visible explanations. If a user cannot tell the difference between analytics and advertising, the consent choice is too vague to trust.
3. Optional categories off by default
This is still one of the fastest ways to tell whether a banner is mostly decorative.
Good gdpr cookie consent examples do not preload analytics or advertising toggles in the enabled state and then wait for users to discover they need to opt back out. They require an affirmative act first.
That matches both the GDPR consent standard and the ICO’s broader SAT framing in 2026. Once you widen the review surface from cookies to pixels, scripts, fingerprinting, and similar storage or access methods, default-on optional tracking becomes even harder to defend.
4. Equal prominence for refusal, not a polite-looking detour
The difference between a clean example and a risky one is often visual, not legalistic.
CNIL’s current formal-notice language is unusually direct: rejecting cookies should be “just as easy as accepting them.” That means a compliant-looking first layer can still be weak if:
- the reject control is only a text link;
- the reject control is buried inside a paragraph;
- the accept button is repeated while reject appears once;
- refusal takes more screens or more cognitive effort than acceptance.
When teams collect gdpr cookie consent examples, this is the pattern to compare most aggressively. It is where manipulative design shows up fastest.
5. A persistent way to reopen and withdraw later
The best gdpr cookie consent examples do not end when the banner closes.
The European Commission still says withdrawing consent must be as easy as giving it. In practice, that means there should be a visible way back into the preference center later, such as a footer link, account privacy control, or floating settings trigger that is not hidden behind a support flow.
If a visitor can accept in one click but must hunt through legal pages to reverse the choice, the example is incomplete no matter how polished the first layer looks.
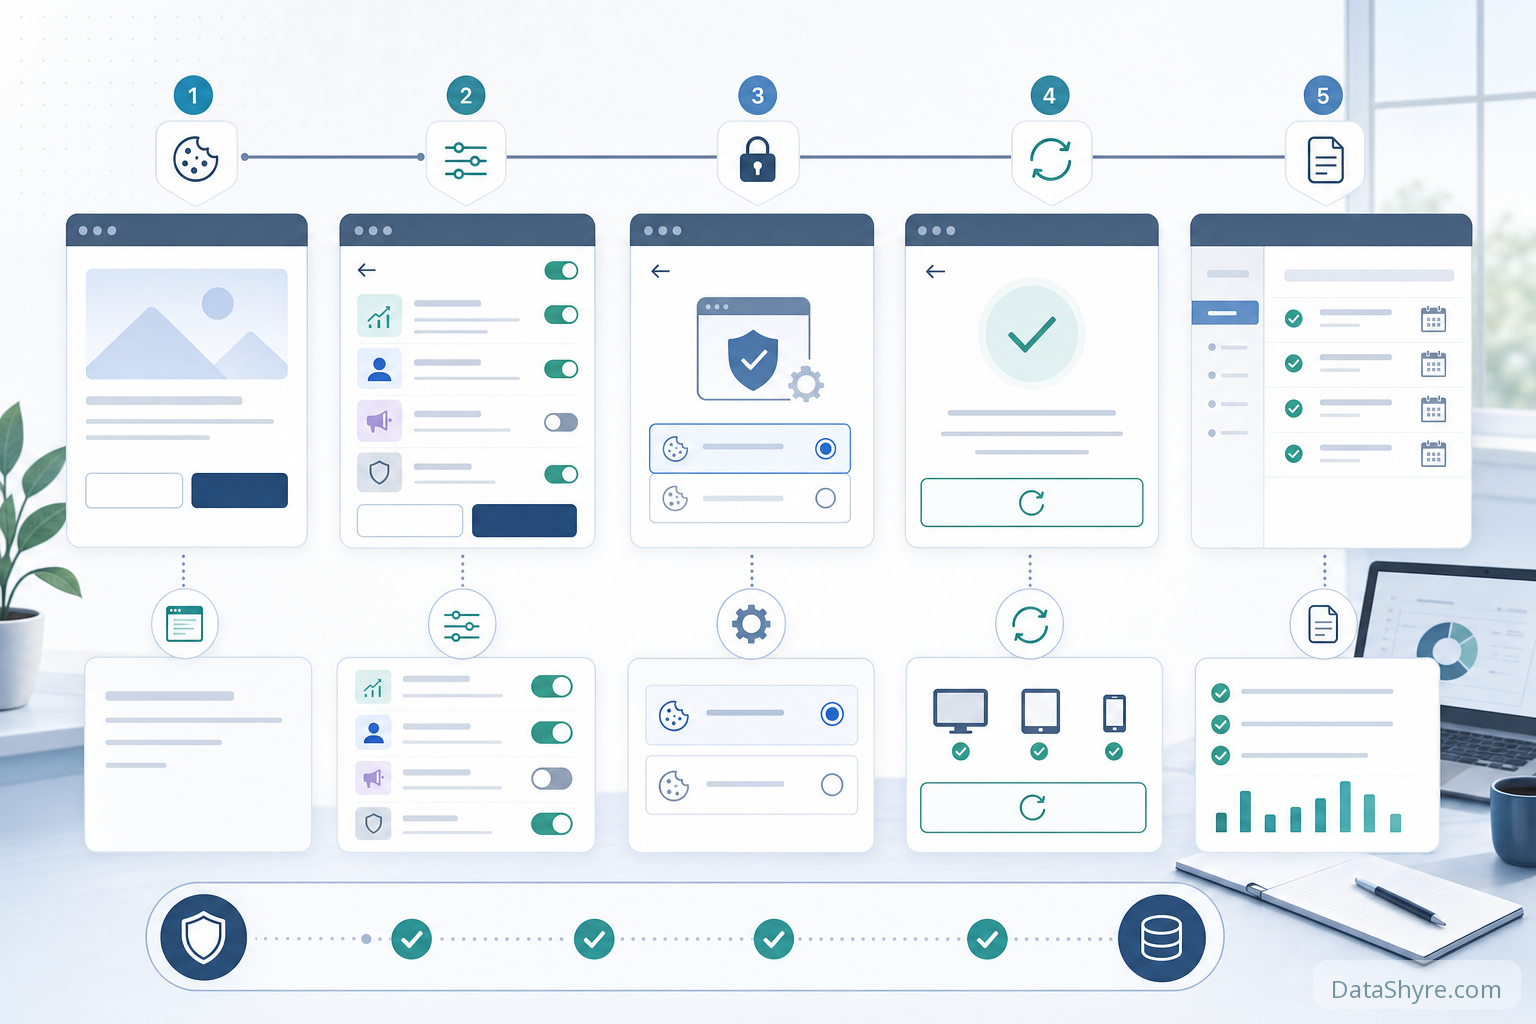
6. Banner text connected to runtime enforcement
Many published gdpr cookie consent examples would fail the moment you open developer tools.
Google’s current setup guide for websites still says consent mode users need to send ad_user_data and ad_personalization in addition to ad_storage and analytics_storage. Its current Tag Assistant troubleshooting guide also still says the default consent state should be set before any tags fire and recommends firing consent-writing template tags on Consent Initialization in Tag Manager.
So one of the most useful example patterns in 2026 is not just visual. It is operational:
- denied defaults land before measurement tags fire;
- updates happen immediately after the user acts;
- Google and non-Google tags respect the same choice;
- rejection and later withdrawal produce a real behavior change.
If the banner says Reject all but the network trace still shows optional measurement running first, it is not one of the gdpr cookie consent examples worth copying.
7. Evidence that survives the next release
The final pattern is the one most screenshot roundups miss: proof.
In the ICO’s April 29, 2026 announcement, William Malcolm said people should have “meaningful control” over how their data is used. That becomes real only when the site can show what happened, not only what the UI intended.
For strong gdpr cookie consent examples, keep evidence for:
- the banner version shown to users;
- the preference categories in force at that time;
- the policy wording and linked notices;
- the consent-mode or CMP version that wrote the signal;
- tests for accept, reject, and withdrawal on the live domain.
This is the pattern that holds up after a theme change, a new pixel, or the next container publish.
What weak examples still get wrong
If you are screening gdpr cookie consent examples quickly, most failing implementations still cluster around the same mistakes:
- no reject option on the first layer;
- vague or bundled purposes;
- optional categories enabled by default;
- no practical way to reopen choices later;
- banner text that says one thing while tags do another.
The ICO’s 2026 compliance update matters here because it shows the baseline is no longer theoretical. Its announcement says 99% of the UK’s top 1,000 websites now meet cookie-banner compliance standards. In other words, the excuses are getting weaker, not stronger.
A practical review sequence for this week
If I were comparing gdpr cookie consent examples for a live site right now, I would review them in this order:
- first-layer balance between accept, reject, and customize;
- purpose wording and category split;
- default states before choice;
- equal prominence of refusal;
- withdrawal path after the banner closes;
- consent-mode signals and tag firing order;
- saved proof after the latest release.
That sequence exposes weak examples faster than collecting another gallery of attractive screenshots.
Bottom line
The most useful gdpr cookie consent examples in 2026 are not the prettiest ones.
They are the ones that give people a real first-layer choice, explain optional purposes honestly, keep refusal as easy as acceptance, make withdrawal easy later, and align banner promises with live tag behavior. If an example cannot pass that test, it is design inspiration at best, not a compliance pattern worth copying.
Sources
- European Commission: https://commission.europa.eu/law/law-topic/data-protection/information-business-and-organisations/legal-grounds-processing-data_en
- ICO announcement: https://ico.org.uk/about-the-ico/media-centre/news-and-blogs/2026/04/final-storage-and-access-technologies-guidance-published/
- ICO storage and access technologies guidance: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guidance-on-the-use-of-storage-and-access-technologies/
- CNIL dark patterns formal notice: https://www.cnil.fr/en/dark-patterns-cookie-banners-cnil-issues-formal-notice-website-publishers
- Google for Developers consent setup: https://developers.google.com/tag-platform/security/guides/consent
- Google for Developers consent debugging: https://developers.google.com/tag-platform/security/guides/consent-debugging
—
Published: October 14, 2026. Updated using current official regulator and platform materials available at publication time.